CarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Notification
  • Autonomous Driving
  • Automotive Ethernet
  • BMS
  • ECU
  • EV
  • ISO/SAE 21434
  • Infotainment
  • OTA Updates
  • OBD-II
  • Pwn2Own
  • RCE
  • SDVs
  • TCU
  • UNECE R155
Cybersecurity

Britain admits 125,000 public chargers have no uniform cyber bar

Cybersecurity

Bosch puts a security gatekeeper on connected motorcycles

Cybersecurity

Trucking group opens a capture-the-flag lab for mechanics

Physical Security

Two California drivers test Axon’s plate database in court

Font ResizerAa
CarThreatCarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
Search
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Sign In Sign In
Follow US
© 2026 Carthreat.com. All right reserved.
Physical Security

A hobbyist toolkit cracks Hyundai head units through their own updater

NEMESIS turns an unsigned update path into root on millions of Gen5W infotainment systems.

CarThreat Staff
Last updated: November 4, 2026 1:49 am
By
ctadmin
2 Min Read
SHARE

A developer publishing as xwtk has released NEMESIS, an open toolkit that gains root on Hyundai Motor Group Gen5W infotainment systems. Hackaday covered the release on November 2.

Contents
What it opensAn unsigned path to rootWhere the charge lands

What it opens

Gen5W units ship in many Hyundai and Kia models from roughly 2015 onward. Once NEMESIS is installed, owners run packages from a community store, including wireless Android Auto and Apple CarPlay on cars that shipped without them, plus turn-by-turn prompts on the driver cluster.

The build requires an Android-based unit with S5W_M in its software version string, and the car must support OTA updates. S5W_L hardware runs a different architecture and cannot be ported. Elantra, Forte, Ioniq 6, and every Canadian Hyundai Motor Group vehicle are excluded because their update schemes lack the flaw.

An unsigned path to root

The documentation says NEMESIS reuses the DSP update agent, which runs unsigned DSP OTA members as root. Installation walks the vehicle into Engineering Mode, opens USB Copy, selects Update DSP, then taps Update OTA. The head unit reboots with the toolkit in place on /system.

That is the security question, not the wireless CarPlay. A shipping vehicle accepts a file from a USB stick and executes part of it with the highest privilege because the update pipeline does not check what it is running.

Where the charge lands

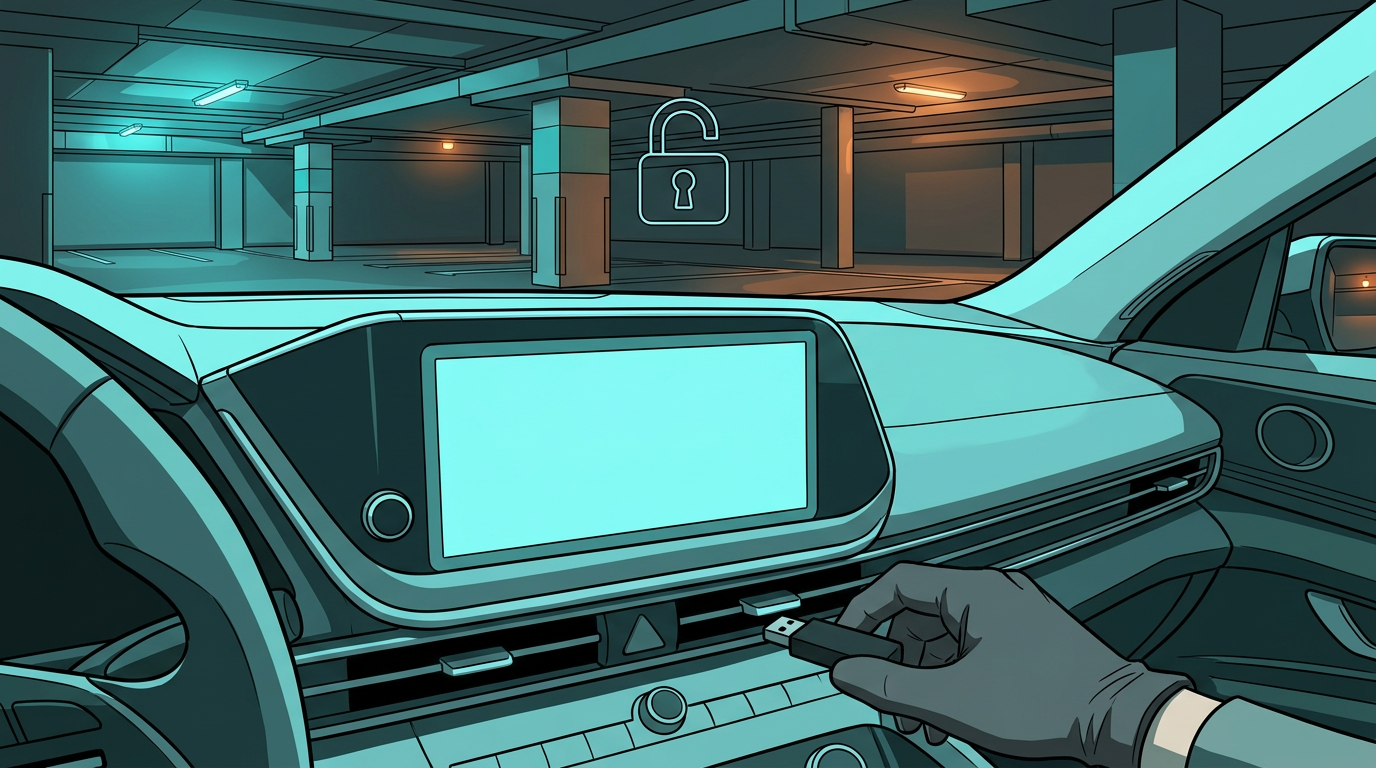
Nothing here is remote; an attacker needs brief access to the USB port. But the property that lets an enthusiast enable a feature lets anyone with a prepared stick install code the owner never approved, with no signing boundary in between.

Hyundai has not published a response. Owners should treat an unattended car and an unfamiliar USB drive the way they would treat a handed-over laptop.
Join Our Newsletter
Subscribe to our newsletter to get our newest articles instantly!
TAGGED:Connected VehiclesECU SecurityFirmware SecurityInfotainment SystemsOTA UpdatesVehicle Software
SOURCES:HackadayGitHub - xwtk/hmg_nemesis
Share This Article
Facebook Email Copy Link

Follow US

Find US on Social Medias
FacebookLike
XFollow
YoutubeSubscribe

You Might Also Like

Policy & Compliance

Connected vehicle security act clears Senate committee hurdle

By
ctadmin
July 22, 2026
Cybersecurity

Florida demands plate readers off highways within 30 days

By
ctadmin
September 1, 2026
Cybersecurity

$60 mirror can make self-driving cars brake for ghosts

By
ctadmin
August 10, 2026
Car NewsCybersecurityPhysical Security

One in seven keyless drivers says thieves tried a relay attack

By
ctadmin
October 19, 2026
Research & Innovation

Cheap AI binary analysis forces a rethink of car firmware defenses

By
ctadmin
September 28, 2026
Cybersecurity

Botslab dash cams ship with 13 flaws and no fix in sight

By
ctadmin
September 26, 2026

CarThreat

Intelligence for the EV and automotive security market
  • News
  • Features
  • Spotlight
  • Events
  • About Carthreat
  • Our Mission
  • Services
  • Contact Us
  • OBD-II
  • Automotive Ethernet
  • TCU
  • Infotainment Systems
  • SDVs
  • BMS
  • ECU Security
  • CAN Bus
  • OTA Updates
  • Vulnerabilities
  • Relay Attacks
  • RCE
  • Threat Intelligence
  • Cybersecurity
  • Digital Keys
  • Bluetooth Security
  • ISO/SAE 21434
  • UNECE R155
  • Regulations
  • Data Privacy
  • EVs
  • Autonomous Driving
  • Pwn2Own Automotive

© 2026 Carthreat.com. All right reserved.  Privacy Policy | Legal

Welcome Back!

Sign in to your account

Username or Email Address
Password

Lost your password?