CarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Notification
  • Autonomous Driving
  • Automotive Ethernet
  • BMS
  • ECU
  • EV
  • ISO/SAE 21434
  • Infotainment
  • OTA Updates
  • OBD-II
  • Pwn2Own
  • RCE
  • SDVs
  • TCU
  • UNECE R155
Cybersecurity

Boston police tested Motorola and Axon readers as Flock exited

Cybersecurity

Leapmotor EVs carry cameras from a supplier Australia banned

Policy & Compliance

BYD rewrites Australian privacy policy after Four Corners questions

Cybersecurity

A passwordless port let a researcher command a moving BYD ute

Font ResizerAa
CarThreatCarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
Search
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Sign In Sign In
Follow US
© 2026 Carthreat.com. All right reserved.
Cybersecurity

Car industry recovery plans buckle within a single day

GitProtect Lab research finds most automotive organisations cannot stay running more than a day after critical systems fail, and recovery work stays stubbornly manual.

CarThreat Staff
Last updated: September 10, 2026 9:56 pm
By
ctadmin
2 Min Read
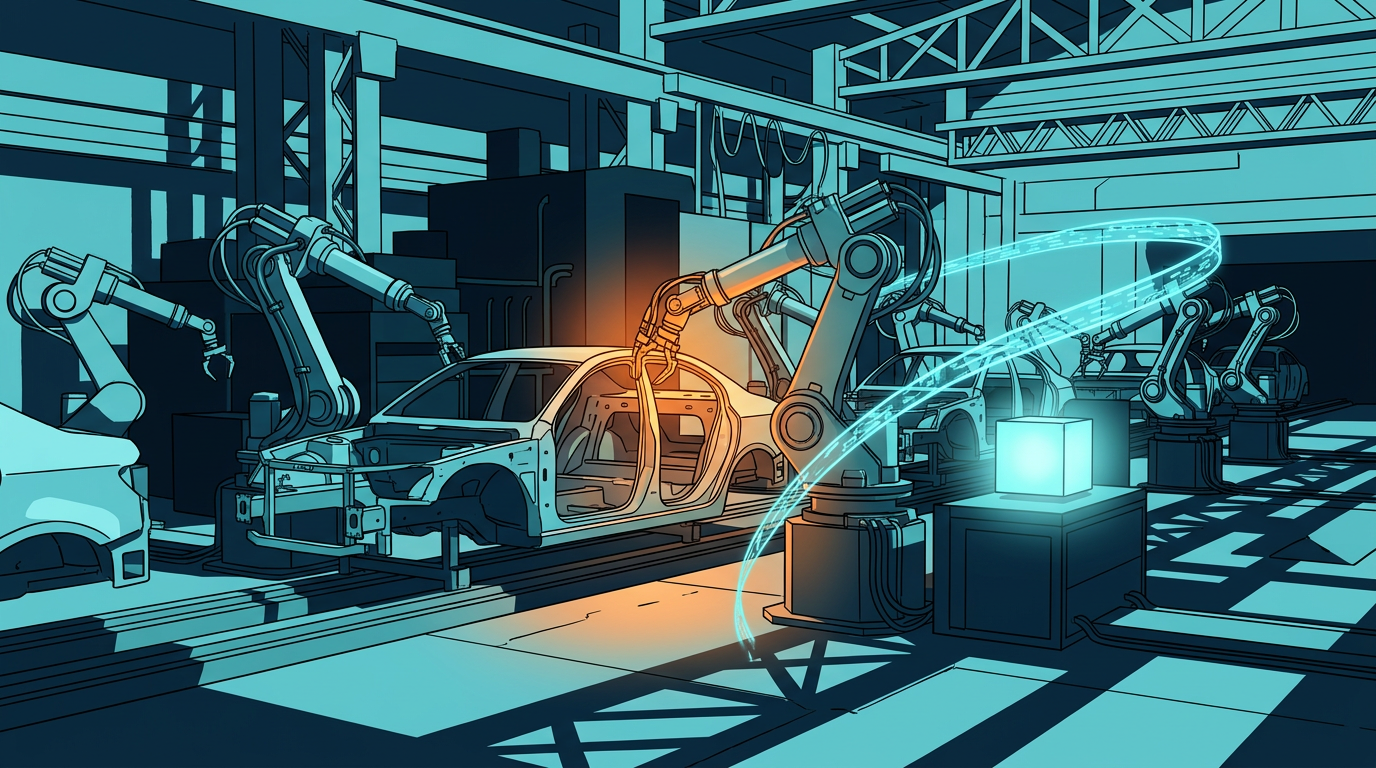
Cel-shaded illustration of stalled robotic assembly arms above a car body with a cyan data loop feeding a glowing storage cube
SHARE

Ransomware planning across the car industry rests on narrow margins, according to GitProtect Lab research that maps how quickly vehicle plants and their suppliers run out of road when critical systems fail.

The shortest fuse belongs to the 19.5% who said an outage turns into an immediate crisis within two hours. A two to 12 hour window is all that 39.5% can manage before downstream distribution breaks down, and reaching a full day takes 28% leaning on physical stock buffers. Just 8.5% said they could absorb one to three days of minor delays. Across the whole sample, 87% could not sustain more than 24 hours offline.

Recovery is where the sector is thinnest. Manual workflows, not automation, set the pace for nearly half of respondents – 46.5% cannot finish a full restore inside a day. Rebuild speed then varies sharply: automated pipelines put a hacked plant’s golden images and configuration data back inside four hours for 23% of teams, while two to five days or longer is the reality for 18%. And 8% have never rehearsed a complete restore across a whole plant’s OT estate.

Network architecture leaves room for an incident to spread. Some 78.5% of the organisations surveyed run flat, dual-homed or poorly segregated IT and OT networks, so an intrusion that lands on corporate systems can travel into production. Only a minority judge plant managers ready to keep assembly lines running if ransomware freezes a manufacturing execution system; 55.5% called them moderately prepared at best.

Isolated backup cover is in place for 70.5% of respondents, so the picture is uneven rather than uniform. A gulf remains for 17.5%, whose protection is only partial. The 12% tail either leaves copies attached to the primary network or has no single backup system at all.
Join Our Newsletter
Subscribe to our newsletter to get our newest articles instantly!
TAGGED:Automotive CybersecurityConnected VehiclesCybersecurityRansomwareSoftware-Defined Vehicles (SDVs)Vehicle SoftwareVulnerabilities
SOURCES:IT Brief UK
Share This Article
Facebook Email Copy Link

Follow US

Find US on Social Medias
FacebookLike
XFollow
YoutubeSubscribe

You Might Also Like

Physical Security

Appeals court hands insurers a second shot at Kia and Hyundai

By
ctadmin
September 18, 2026
AI Race

AI tool chains low-severity bugs into critical automotive attack paths

By
ctadmin
July 27, 2026
Anime illustration of corrupted data racing up an EV charging cable toward the car
Electric Vehicles

Open Charge Alliance will review Korean tool that hijacked an EV charger

By
ctadmin
September 3, 2026
Policy & Compliance

Korean agencies rehearse a car hack response America lacks

By
ctadmin
September 21, 2026
Cybersecurity

Automotive Cyber Vulnerabilities Double Year Over Year as Attacks Get Easier

By
ctadmin
July 1, 2026
Cybersecurity

US Bans Polestar EV Sales Under National Security Connected Vehicle Rule

By
ctadmin
July 1, 2026

CarThreat

Intelligence for the EV and automotive security market
  • News
  • Features
  • Spotlight
  • Events
  • About Carthreat
  • Our Mission
  • Services
  • Contact Us
  • OBD-II
  • Automotive Ethernet
  • TCU
  • Infotainment Systems
  • SDVs
  • BMS
  • ECU Security
  • CAN Bus
  • Threat Intelligence
  • Cybersecurity
  • Digital Keys
  • Bluetooth Security
  • OTA Updates
  • Vulnerabilities
  • Relay Attacks
  • RCE
  • Data Privacy
  • EVs
  • Autonomous Driving
  • Pwn2Own Automotive
  • ISO/SAE 21434
  • UNECE R155
  • Regulations

© 2026 Carthreat.com. All right reserved.  Privacy Policy | Legal

Welcome Back!

Sign in to your account

Username or Email Address
Password

Lost your password?