CarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Notification
  • Autonomous Driving
  • Automotive Ethernet
  • BMS
  • ECU
  • EV
  • ISO/SAE 21434
  • Infotainment
  • OTA Updates
  • OBD-II
  • Pwn2Own
  • RCE
  • SDVs
  • TCU
  • UNECE R155
India's two-part cyber rulebook now has a certification trail
Cybersecurity

India’s two-part cyber rulebook now has a certification trail

Colmobil shuts some counters after intruders reach its network
Cybersecurity

Colmobil shuts some counters after intruders reach its network

A supplier flaw handed car buyers' payment records to criminals
Cybersecurity

A supplier flaw handed car buyers’ payment records to criminals

Physical Security

Rental cars stored video of Norwegian troops and gate codes

Font ResizerAa
CarThreatCarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
Search
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Sign In Sign In
Follow US
© 2026 Carthreat.com. All right reserved.
Cybersecurity

Unlocking QNX IFS Images for Binary Whitelisting in Automotive Embedded Systems

CarThreat Staff
Last updated: May 25, 2026 2:09 am
By
ctadmin
2 Min Read
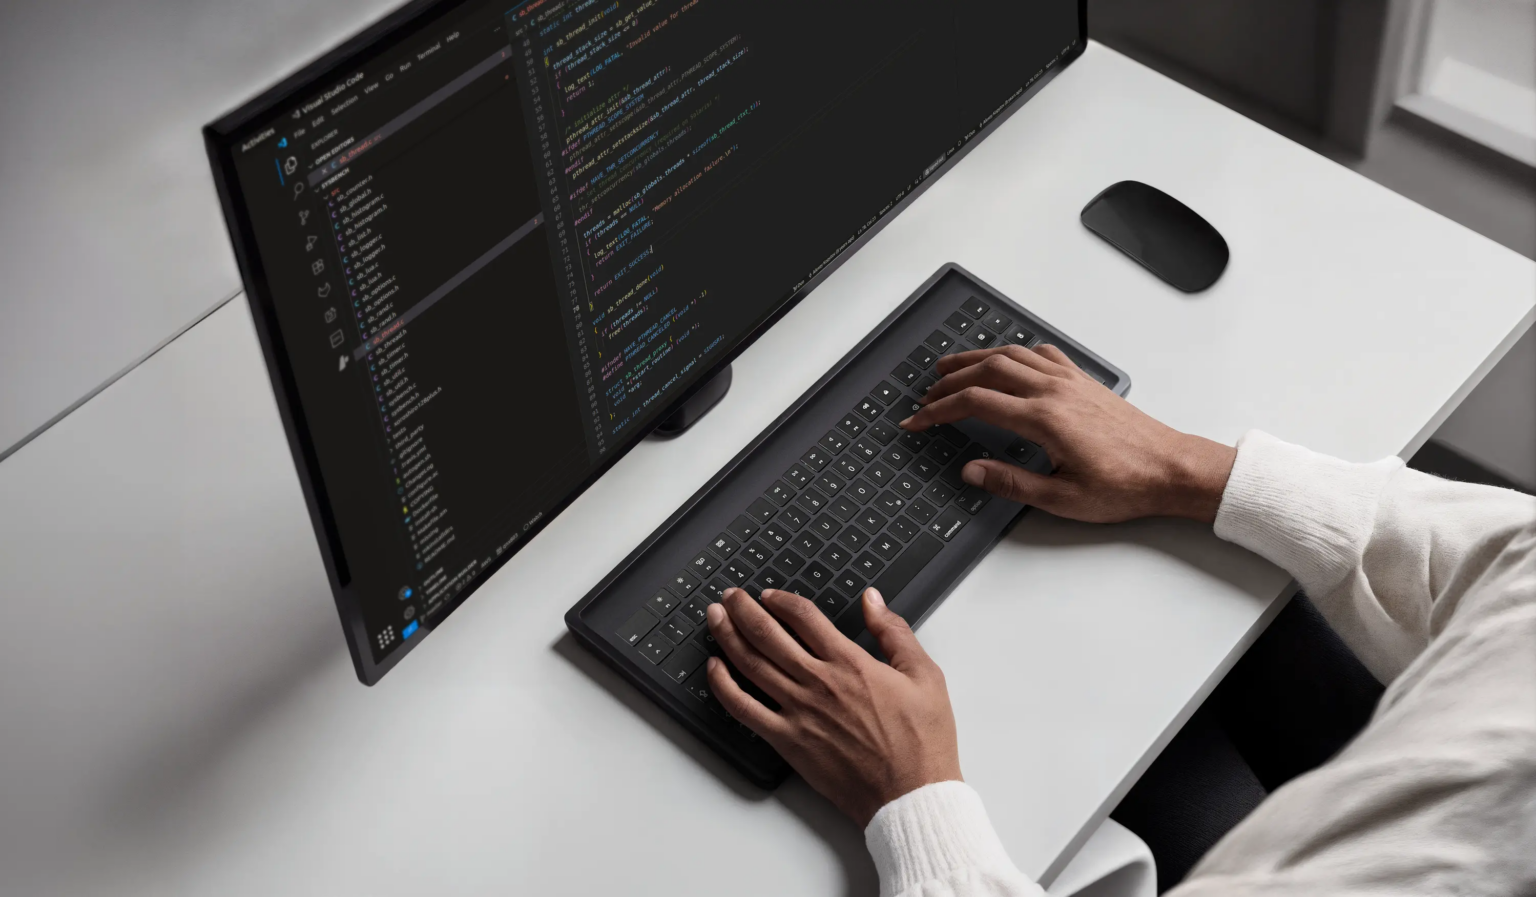
Developer workstation showing code analysis for QNX embedded systems
QNX IFS image analysis for binary whitelisting in automotive systems
SHARE

The Challenge of Extracting QNX IFS Content

For automotive security engineers working with QNX based embedded systems, extracting the contents of an Image File System (IFS) is a critical step for binary whitelisting. When integrating security solutions like Karamba into a QNX IFS image, engineers need to inspect binaries in their final form after the IFS building utility strips debug symbols and applies modifications. The standard dumpifs utility provided by QNX SDP 6.6 offers a “-d” switch to dump files to a specified folder while preserving the IFS directory structure. However, this approach often fails with an error message such as “dumpifs: Unable to open proc/boot/procnto-instr: No such file or directory,” indicating that dumpifs expects the target folder to already contain the IFS directory structure.

Contents
The Challenge of Extracting QNX IFS ContentPractical Solution for Automotive Security Workflows

Practical Solution for Automotive Security Workflows

To overcome this limitation, a practical method involves first learning the IFS directory structure by running dumpifs without switches and redirecting the output to a text file. This prints all file paths within the IFS. A simple bash script can then parse this output and recreate the folder structure on the build machine using the full file paths. Once the directory structure is in place, dumpifs with the “-d” switch can successfully extract all binaries. The flat dumping option (“-b”) is insufficient for whitelisting because it overwrites files with duplicate names, retaining only the last one encountered. This technique ensures every binary is available for inspection, supporting robust whitelist policy creation for QNX based automotive ECUs and infotainment systems.

Source: Karambasecurity
Join Our Newsletter
Subscribe to our newsletter to get our newest articles instantly!
Share This Article
Facebook Email Copy Link

Follow US

Find US on Social Medias
FacebookLike
XFollow
YoutubeSubscribe

You Might Also Like

Cybersecurity

Misuse charges lead Milwaukee to lock down plate reader access

By
ctadmin
September 3, 2026
Cel-shaded illustration of stalled robotic assembly arms above a car body with a cyan data loop feeding a glowing storage cube
Cybersecurity

Car industry recovery plans buckle within a single day

By
ctadmin
September 10, 2026
Cybersecurity

Report warns supplier hacks could cost automakers $100M

By
ctadmin
August 14, 2026
Cybersecurity

Nine Million Kia and Hyundai Vehicles Now Under Formal Recall for Theft Vulnerability

By
ctadmin
July 1, 2026
Cybersecurity

Charger scan finds 720 of 1,000 exposed endpoints skip encryption

By
ctadmin
September 3, 2026
Cybersecurity

Sydney court hears Tesla app gave an abuser remote car control

By
ctadmin
September 9, 2026

CarThreat

Intelligence for the EV and automotive security market
  • News
  • Features
  • Spotlight
  • Events
  • About Carthreat
  • Our Mission
  • Services
  • Contact Us
  • OBD-II
  • Automotive Ethernet
  • TCU
  • Infotainment Systems
  • SDVs
  • BMS
  • ECU Security
  • CAN Bus
  • Threat Intelligence
  • Cybersecurity
  • Digital Keys
  • Bluetooth Security
  • OTA Updates
  • Vulnerabilities
  • Relay Attacks
  • RCE
  • Data Privacy
  • EVs
  • Autonomous Driving
  • Pwn2Own Automotive
  • ISO/SAE 21434
  • UNECE R155
  • Regulations

© 2026 Carthreat.com. All right reserved.  Privacy Policy | Legal

Welcome Back!

Sign in to your account

Username or Email Address
Password

Lost your password?