CarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Notification
  • Autonomous Driving
  • Automotive Ethernet
  • BMS
  • ECU
  • EV
  • ISO/SAE 21434
  • Infotainment
  • OTA Updates
  • OBD-II
  • Pwn2Own
  • RCE
  • SDVs
  • TCU
  • UNECE R155
Cybersecurity

Britain admits 125,000 public chargers have no uniform cyber bar

Cybersecurity

Bosch puts a security gatekeeper on connected motorcycles

Cybersecurity

Trucking group opens a capture-the-flag lab for mechanics

Physical Security

Two California drivers test Axon’s plate database in court

Font ResizerAa
CarThreatCarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
Search
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Sign In Sign In
Follow US
© 2026 Carthreat.com. All right reserved.
The Story

Our car is not the target, the supplier’s software is

This week's four stories share one shape - the weak point sat above the vehicle, in an app, an update pipe, a cloud account or a vendor's tool.

CarThreat Staff
Last updated: November 5, 2026 9:33 pm
By
ctadmin
2 Min Read
SHARE

Four stories crossed the automotive security desk this week and, read together, they describe something more useful than any single bug: almost nothing that went wrong happened inside the car.

Contents
The fixes cannot reach the parts that matterWhat to ask for

Tata Motors owners got a CERT-In advisory over four high-severity flaws in the iRA apps, the worst of them hardcoded service credentials shipped inside the download that anyone can unpack. The attackers never needed the vehicle; they needed a copy of the software that holds an owner’s authority.

The fixes cannot reach the parts that matter

The eSync Alliance’s warning points the same way. Over-the-air systems were built around the infotainment screen and the connectivity unit, while the braking and steering controllers arrive from separate suppliers on separate update paths. A recall becomes the patch mechanism.

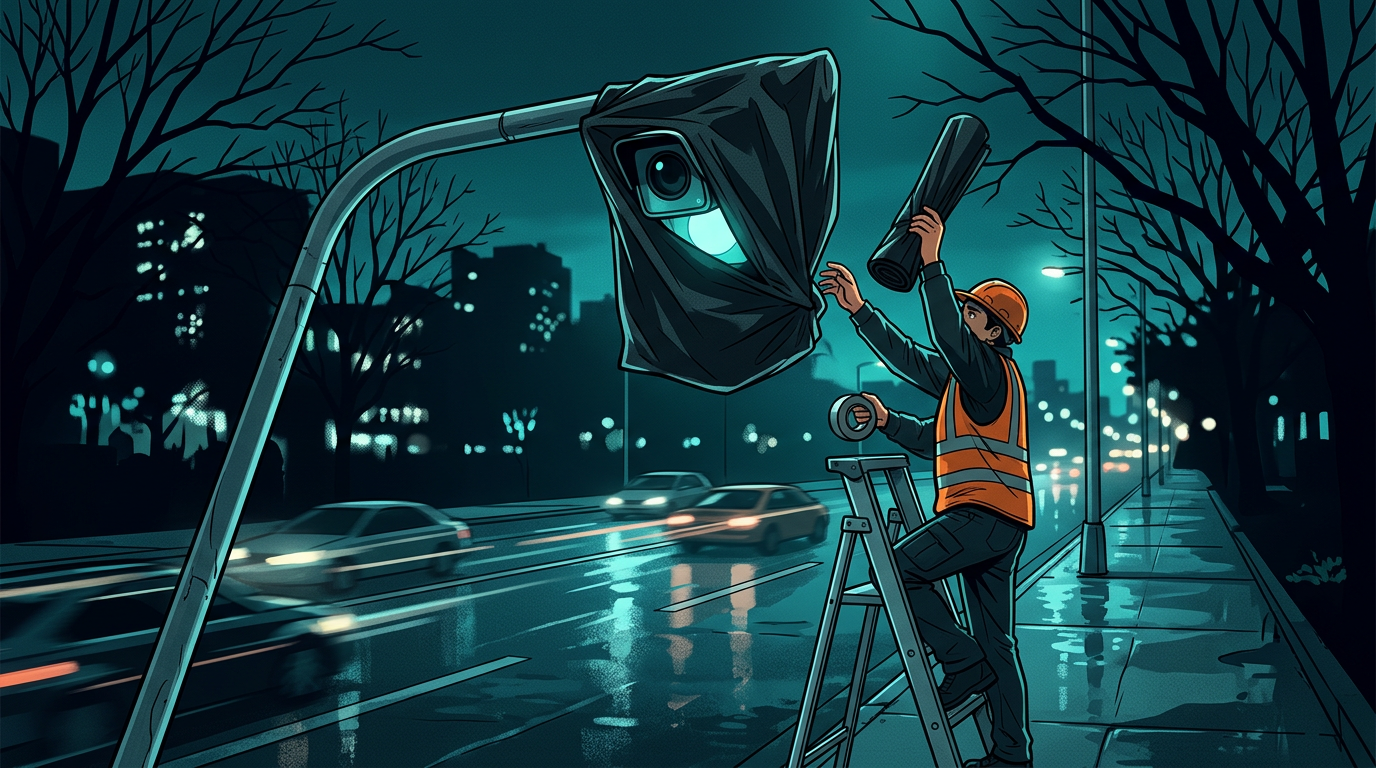
Excelsior Springs found its bagged plate cameras still logging plate characters, which is a vendor-hardware lesson about what off actually means. In Chicago, nine locked cars left the street in three weeks, and the likeliest tool was a legitimate key programmer sold to locksmiths.

Ford, meanwhile, published a promise not to sell driving data to insurers. A pledge is worth what the settings menu is worth next year, and several specialists said so plainly.

What to ask for

Three questions follow. Can the security-critical controller on your car receive a signed update without a workshop visit? Does the phone app carry secrets in its package? And does a stop command at the vendor, a city council or a settings screen actually stop the flow?

None of these are answered by a stronger firewall around the vehicle. They are answered by whoever writes the software above it, and by the length of the supplier list behind them.
Join Our Newsletter
Subscribe to our newsletter to get our newest articles instantly!
TAGGED:Connected VehiclesCybersecurityData PrivacyOTA UpdatesSupply ChainVulnerabilities
SOURCES:Cyber Security NewsAM-onlineFOX4 Kansas CityCWB ChicagoTechCrunch
Share This Article
Facebook Email Copy Link

Follow US

Find US on Social Medias
FacebookLike
XFollow
YoutubeSubscribe

You Might Also Like

Cybersecurity

Vehicle security must follow what an AI agent does next

By
ctadmin
September 29, 2026
The Story

How A Forgotten Letter Reunited Two Old Friends

By
ctadmin
August 28, 2021
Anime illustration of a silver minivan unloading from a container ship at the Port of Los Angeles
Car NewsEV MovementPolicy & Compliance

Waymo keeps shipping Chinese robotaxi shells as a Senate ban waits

By
ctadmin
October 24, 2026
Cybersecurity

One VIN number can unlock years of driver tracking

By
ctadmin
August 9, 2026
Policy & Compliance

Automotive cyber budgets follow regulation more than attacks

By
ctadmin
September 17, 2026
Policy & Compliance

Hawley wants plate reader data deleted after ten days

By
ctadmin
October 2, 2026

CarThreat

Intelligence for the EV and automotive security market
  • News
  • Features
  • Spotlight
  • Events
  • About Carthreat
  • Our Mission
  • Services
  • Contact Us
  • OBD-II
  • Automotive Ethernet
  • TCU
  • Infotainment Systems
  • SDVs
  • BMS
  • ECU Security
  • CAN Bus
  • Threat Intelligence
  • Cybersecurity
  • Digital Keys
  • Bluetooth Security
  • OTA Updates
  • Vulnerabilities
  • Relay Attacks
  • RCE
  • Data Privacy
  • EVs
  • Autonomous Driving
  • Pwn2Own Automotive
  • ISO/SAE 21434
  • UNECE R155
  • Regulations

© 2026 Carthreat.com. All right reserved.  Privacy Policy | Legal

Welcome Back!

Sign in to your account

Username or Email Address
Password

Lost your password?