CarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Notification
  • Autonomous Driving
  • Automotive Ethernet
  • BMS
  • ECU
  • EV
  • ISO/SAE 21434
  • Infotainment
  • OTA Updates
  • OBD-II
  • Pwn2Own
  • RCE
  • SDVs
  • TCU
  • UNECE R155
Cybersecurity

Britain admits 125,000 public chargers have no uniform cyber bar

Cybersecurity

Bosch puts a security gatekeeper on connected motorcycles

Cybersecurity

Trucking group opens a capture-the-flag lab for mechanics

Physical Security

Two California drivers test Axon’s plate database in court

Font ResizerAa
CarThreatCarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
Search
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Sign In Sign In
Follow US
© 2026 Carthreat.com. All right reserved.
Cybersecurity

Dealer software vendor traces Storm intrusion to a support tool

Auto-IT says a third party's remote monitoring tool was misused to reach a small number of its dealership customer systems, as Storm ransomware keeps naming Australian dealers.

CarThreat Staff
Last updated: September 16, 2026 1:16 am
By
ctadmin
2 Min Read
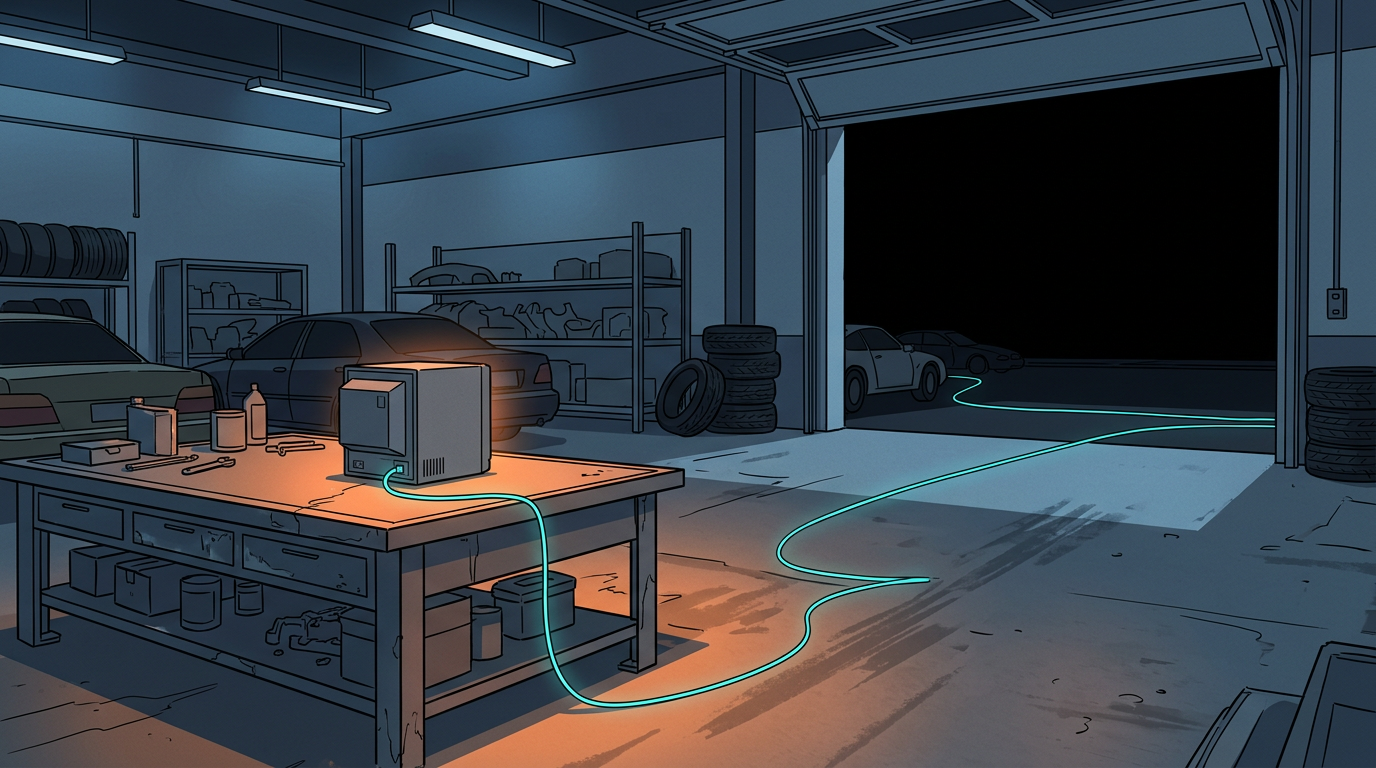
cel-shaded illustration of an IT appliance on a workbench in a dark dealership service bay, a cyan cable running out through the open bay door
SHARE

A support tool built by one company became the doorway into dealership systems run by another, and the vendor at the centre of it has now confirmed a limited intrusion.

Auto-IT responded this week to dark web claims from the Storm ransomware group, which has listed more than half a dozen Australian car dealerships and heavy machinery suppliers since August 18. Several of those businesses have pointed at a third-party technology supplier as the source of their trouble.

Auto-IT’s own account, given to Cyber Daily, is narrower. It describes a security incident in a small number of customer environments, where an intruder misused a remote monitoring tool belonging to another firm. That class of software is the plumbing that lets an outside IT provider reach a client’s machines; stolen credentials for that layer hand an attacker a legitimate path into every client it touches.

The company said a small number of customer businesses were named on a dark web listing, that the incident had been contained, and that affected environments remain secure and fully operational. Independent forensic specialists were engaged, impacted dealers were contacted directly, and the matter was referred to the Australian Cyber Security Centre.

Auto-IT is careful not to call this its own breach. The distinction matters commercially, and it will not comfort dealers who buy software precisely because they cannot staff a security team of their own.

A franchise store holds licence scans, finance applications and service histories. A single supplier-side credential is enough to reach all of it at once.
Join Our Newsletter
Subscribe to our newsletter to get our newest articles instantly!
TAGGED:Access ControlsCybersecurityData BreachRansomwareSupply ChainThreat Intelligence
SOURCES:Cyber Daily
Share This Article
Facebook Email Copy Link

Follow US

Find US on Social Medias
FacebookLike
XFollow
YoutubeSubscribe

You Might Also Like

Cybersecurity

Trucking group opens a capture-the-flag lab for mechanics

By
ctadmin
November 6, 2026
Cybersecurity

rFpro Extends AV Simulation Platform With Cabin Monitoring Support

By
ctadmin
June 12, 2026
Car NewsCybersecurity

Tesla keyless theft vulnerability exposes CAN injection risks across EV fleets

By
ctadmin
July 18, 2026
Cybersecurity

Toyota defends its connected car data as Australian regulators dig in

By
ctadmin
October 11, 2026
Anime illustration of corrupted data racing up an EV charging cable toward the car
Electric Vehicles

Open Charge Alliance will review Korean tool that hijacked an EV charger

By
ctadmin
September 3, 2026
Policy & Compliance

Wisconsin churches take plate reader searches to the top court

By
ctadmin
October 20, 2026

CarThreat

Intelligence for the EV and automotive security market
  • News
  • Features
  • Spotlight
  • Events
  • About Carthreat
  • Our Mission
  • Services
  • Contact Us
  • OBD-II
  • Automotive Ethernet
  • TCU
  • Infotainment Systems
  • SDVs
  • BMS
  • ECU Security
  • CAN Bus
  • OTA Updates
  • Vulnerabilities
  • Relay Attacks
  • RCE
  • Threat Intelligence
  • Cybersecurity
  • Digital Keys
  • Bluetooth Security
  • ISO/SAE 21434
  • UNECE R155
  • Regulations
  • Data Privacy
  • EVs
  • Autonomous Driving
  • Pwn2Own Automotive

© 2026 Carthreat.com. All right reserved.  Privacy Policy | Legal

Welcome Back!

Sign in to your account

Username or Email Address
Password

Lost your password?