CarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Notification
  • Autonomous Driving
  • Automotive Ethernet
  • BMS
  • ECU
  • EV
  • ISO/SAE 21434
  • Infotainment
  • OTA Updates
  • OBD-II
  • Pwn2Own
  • RCE
  • SDVs
  • TCU
  • UNECE R155
Cybersecurity

Britain admits 125,000 public chargers have no uniform cyber bar

Cybersecurity

Bosch puts a security gatekeeper on connected motorcycles

Cybersecurity

Trucking group opens a capture-the-flag lab for mechanics

Physical Security

Two California drivers test Axon’s plate database in court

Font ResizerAa
CarThreatCarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
Search
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Sign In Sign In
Follow US
© 2026 Carthreat.com. All right reserved.
Physical Security

A Renault owner rooted his dashboard clock and found a 2011 kernel

Fixing a daylight saving glitch meant jailbreaking a TomTom unit that had never been patched in 15 years.

CarThreat Staff
Last updated: November 4, 2026 1:49 am
By
ctadmin
2 Min Read
SHARE

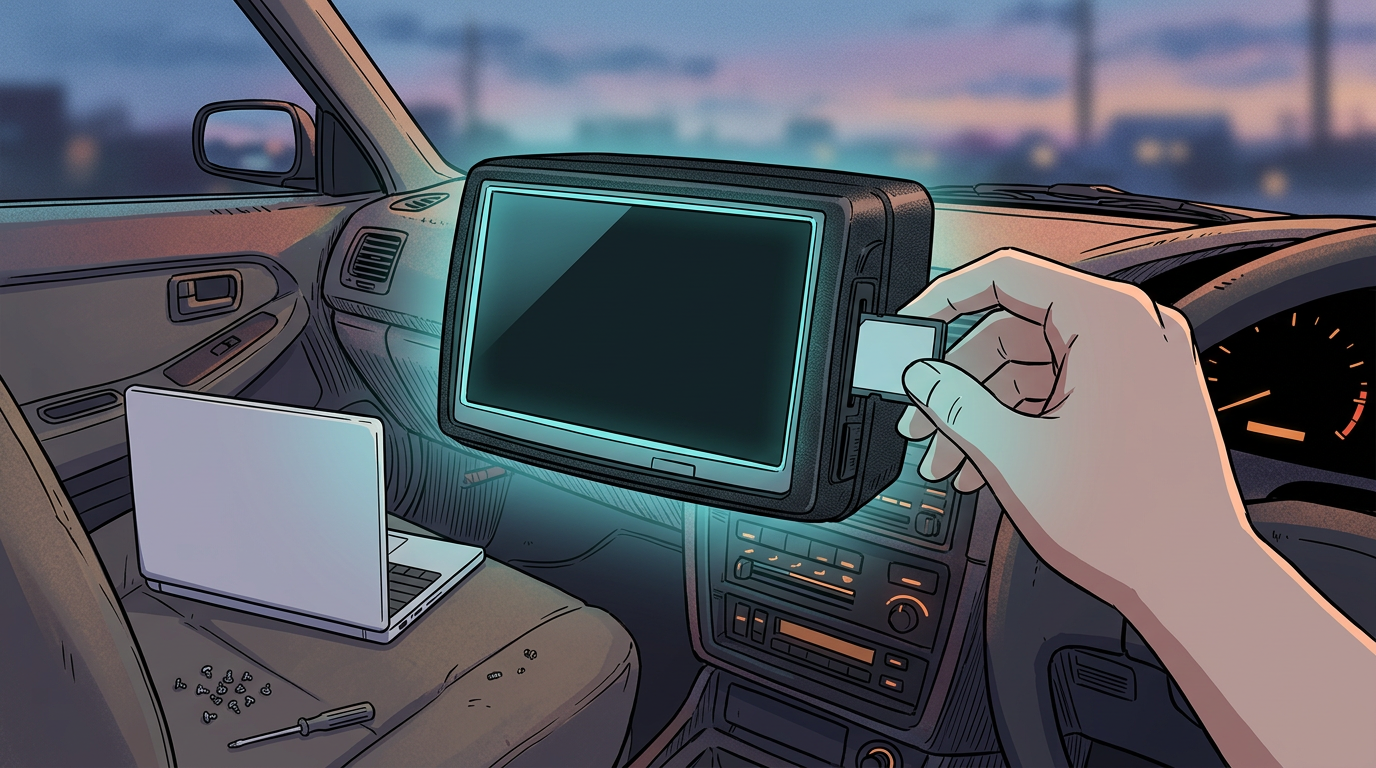
Rasmus Moorats wanted to change the clock on his 2014 Renault Latitude. The Set time option was missing, and the settings menu refused to open without a genuine map SD card. He ended up with root on the navigation unit.

Contents
A menu stored on removable mediaThree lines and a core dumpWhat the stunt actually shows

A menu stored on removable media

The unit is a TomTom Carminat LIVE running a custom system on Linux 2.6.28.10. Writing up the work on November 2, Moorats found the menu definition itself lived on the SD card, so the unit could not reach its settings without one.

TomTom and Renault hardened it beyond what 2011 code usually gets: read-only partitions, signed updates.

Three lines and a core dump

Moorats built a QEMU emulator with a stub CAN bus to watch what the unit reads at boot. One file, master.script, is parsed by a program called ttn that runs as root. Its LOG command wrote to an unsanitized path, so adding ../ let a root process write anywhere.

He aimed that write at core_pattern, the Linux setting for what happens after a crash. He piped a shell and a script from the card into it, then launched dbus-monitor, which aborts on a machine with no system bus. The kernel ran the script as root.

The payload was three lines. He found the timezone offset in internal storage and moved it from 180 minutes to 120.

What the stunt actually shows

This is not remote. Someone must insert a prepared card, and the driver must approve the Execute master.script prompt. A rental, a shared car, or a shop visit supplies both.

The flaws are ordinary. Removable media is trusted at boot, the parser runs privileged, and paths go unvalidated. Head units outlive their support windows by a decade, so those mistakes sit in traffic long after anyone remembers the fix.
Join Our Newsletter
Subscribe to our newsletter to get our newest articles instantly!
TAGGED:Connected VehiclesFirmware SecurityInfotainment SystemsRemote Code Execution (RCE)Vehicle SoftwareVulnerabilities
SOURCES:nns.eeCyber Security News
Share This Article
Facebook Email Copy Link

Follow US

Find US on Social Medias
FacebookLike
XFollow
YoutubeSubscribe

You Might Also Like

Physical Security

A hobbyist toolkit cracks Hyundai head units through their own updater

By
ctadmin
November 4, 2026
Cybersecurity

Car eSIMs get a security stamp built to last a decade

By
ctadmin
September 24, 2026
Policy & Compliance

How the EU Cyber Resilience Act Reshapes Compliance for Software Defined Vehicles

By
ctadmin
June 19, 2026
cel-shaded illustration of a heavy truck brake drum with a glowing cyan barrier blocking orange wireless signal waves
Cybersecurity

Stoneridge puts truck brakes behind a hardware partition

By
ctadmin
September 16, 2026
A connected sedan on a government plaza at dusk emitting sound-wave arcs toward a departing official
Cybersecurity

A car is not a private room, Dutch spy service tells officials

By
ctadmin
September 30, 2026
A locked barrier at an Israeli car import terminal at dusk
Car NewsCybersecurity

SETTRA ransomware turns up behind the Colmobil import outage

By
ctadmin
October 29, 2026

CarThreat

Intelligence for the EV and automotive security market
  • News
  • Features
  • Spotlight
  • Events
  • About Carthreat
  • Our Mission
  • Services
  • Contact Us
  • OBD-II
  • Automotive Ethernet
  • TCU
  • Infotainment Systems
  • SDVs
  • BMS
  • ECU Security
  • CAN Bus
  • Relay Attacks
  • RCE
  • Threat Intelligence
  • Cybersecurity
  • Digital Keys
  • Bluetooth Security
  • OTA Updates
  • Vulnerabilities
  • UNECE R155
  • Regulations
  • Data Privacy
  • EVs
  • Autonomous Driving
  • Pwn2Own Automotive
  • ISO/SAE 21434

© 2026 Carthreat.com. All right reserved.  Privacy Policy | Legal

Welcome Back!

Sign in to your account

Username or Email Address
Password

Lost your password?