CarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Notification
  • Autonomous Driving
  • Automotive Ethernet
  • BMS
  • ECU
  • EV
  • ISO/SAE 21434
  • Infotainment
  • OTA Updates
  • OBD-II
  • Pwn2Own
  • RCE
  • SDVs
  • TCU
  • UNECE R155
Cybersecurity

Britain admits 125,000 public chargers have no uniform cyber bar

Cybersecurity

Bosch puts a security gatekeeper on connected motorcycles

Cybersecurity

Trucking group opens a capture-the-flag lab for mechanics

Physical Security

Two California drivers test Axon’s plate database in court

Font ResizerAa
CarThreatCarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
Search
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Sign In Sign In
Follow US
© 2026 Carthreat.com. All right reserved.
CybersecurityInnovation

Swedish study finds car software flaws drift to the cloud

A Swedish review of 413 connected-car flaws finds the largest share now sits in apps and manufacturer cloud services rather than the vehicle itself.

CarThreat Staff
Last updated: October 22, 2026 2:09 am
By
ctadmin
2 Min Read
SHARE

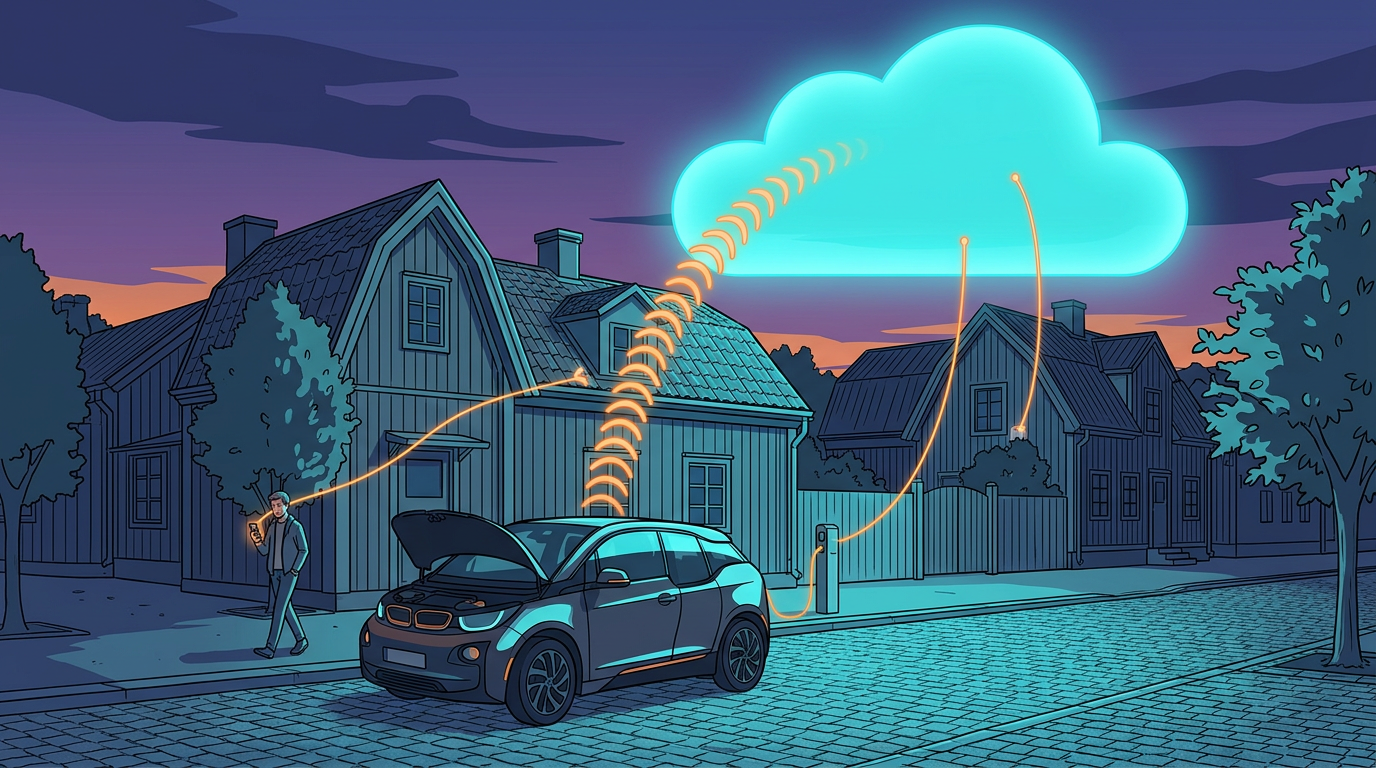
A study of 413 reported software flaws in connected cars, covering 2022 through 2024, has been set against the decade before it by researchers at Chalmers University of Technology and the University of Gothenburg. External software – apps, websites and manufacturer cloud platforms – now accounts for more than a third of the total. That is close to three times the share earlier studies recorded.

Srijita Basu, a postdoctoral researcher in software engineering at both institutions, traced the shift: a decade ago the cars’ own systems supplied most of the vulnerabilities, whereas apps, websites and cloud services have since multiplied their share by roughly three.

Where the bugs sit changes what an attack looks like. A flaw in a vehicle module forces someone to reach the vehicle. A flaw in a booking site or companion app needs only a login form. Cars talk to dealer portals, charging networks, phone applications and the manufacturer’s own stack, and each handshake is a potential doorway.

The study also found reported risks are graded more severely than they once were. The data at stake is not mechanical either. Location histories, commute times and home addresses accumulate in cloud services because that is where connected features do their work.

Basu’s team points to a December 2024 disclosure, when records for about 800,000 electric cars from Volkswagen, Audi, Seat and Skoda sat openly accessible for months. GPS positions plus owner emails, phone numbers and street addresses were exposed through the upload service. The leak was closed after an ethical hacking group acted on a whistleblower tip.

For manufacturers, the finding argues against treating the vehicle as the security perimeter. Supplier contracts, app updates and cloud tenancy settings now carry as much risk as any control unit.
Join Our Newsletter
Subscribe to our newsletter to get our newest articles instantly!
TAGGED:Connected VehiclesCybersecurityData PrivacyResearchTelematics Control Units (TCU)Vehicle SoftwareVulnerabilities
SOURCES:University of Gothenburg (press release)New Atlas
Share This Article
Facebook Email Copy Link

Follow US

Find US on Social Medias
FacebookLike
XFollow
YoutubeSubscribe

You Might Also Like

Policy & Compliance

Oklahoma judge finds a Flock lookup breached the Fourth Amendment

By
ctadmin
October 4, 2026
Policy & Compliance

India orders forensic audit of its vehicle record portals

By
ctadmin
October 25, 2026
Cybersecurity

Repeated patterns hijack depth readings of car stereo cameras

By
ctadmin
August 13, 2026
CybersecurityPolicy & Compliance

Al Carns links the Jaguar Land Rover shutdown to a state

By
ctadmin
October 28, 2026
My Eicher fleet API flaws exposed 676,000 trucks to takeover
Cybersecurity

My Eicher fleet API flaws exposed 676,000 trucks to takeover

By
ctadmin
August 1, 2026
CybersecurityPhysical Security

Franklin County audit finds a deputy inside the plate database

By
ctadmin
November 2, 2026

CarThreat

Intelligence for the EV and automotive security market
  • News
  • Features
  • Spotlight
  • Events
  • About Carthreat
  • Our Mission
  • Services
  • Contact Us
  • OBD-II
  • Automotive Ethernet
  • TCU
  • Infotainment Systems
  • SDVs
  • BMS
  • ECU Security
  • CAN Bus
  • OTA Updates
  • Vulnerabilities
  • Relay Attacks
  • RCE
  • Threat Intelligence
  • Cybersecurity
  • Digital Keys
  • Bluetooth Security
  • ISO/SAE 21434
  • UNECE R155
  • Regulations
  • Data Privacy
  • EVs
  • Autonomous Driving
  • Pwn2Own Automotive

© 2026 Carthreat.com. All right reserved.  Privacy Policy | Legal

Welcome Back!

Sign in to your account

Username or Email Address
Password

Lost your password?