CarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Notification
  • Autonomous Driving
  • Automotive Ethernet
  • BMS
  • ECU
  • EV
  • ISO/SAE 21434
  • Infotainment
  • OTA Updates
  • OBD-II
  • Pwn2Own
  • RCE
  • SDVs
  • TCU
  • UNECE R155
India's two-part cyber rulebook now has a certification trail
Cybersecurity

India’s two-part cyber rulebook now has a certification trail

Colmobil shuts some counters after intruders reach its network
Cybersecurity

Colmobil shuts some counters after intruders reach its network

A supplier flaw handed car buyers' payment records to criminals
Cybersecurity

A supplier flaw handed car buyers’ payment records to criminals

Physical Security

Rental cars stored video of Norwegian troops and gate codes

Font ResizerAa
CarThreatCarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
Search
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Sign In Sign In
Follow US
© 2026 Carthreat.com. All right reserved.
Cybersecurity

My Eicher fleet API flaws exposed 676,000 trucks to takeover

Unauthenticated APIs in the Volvo-Eicher fleet platform let a researcher seize control of 676,000 commercial vehicles and their owners' data.

CarThreat Staff
Last updated: August 1, 2026 9:54 am
By
ctadmin
2 Min Read
My Eicher fleet API flaws exposed 676,000 trucks to takeover
SHARE

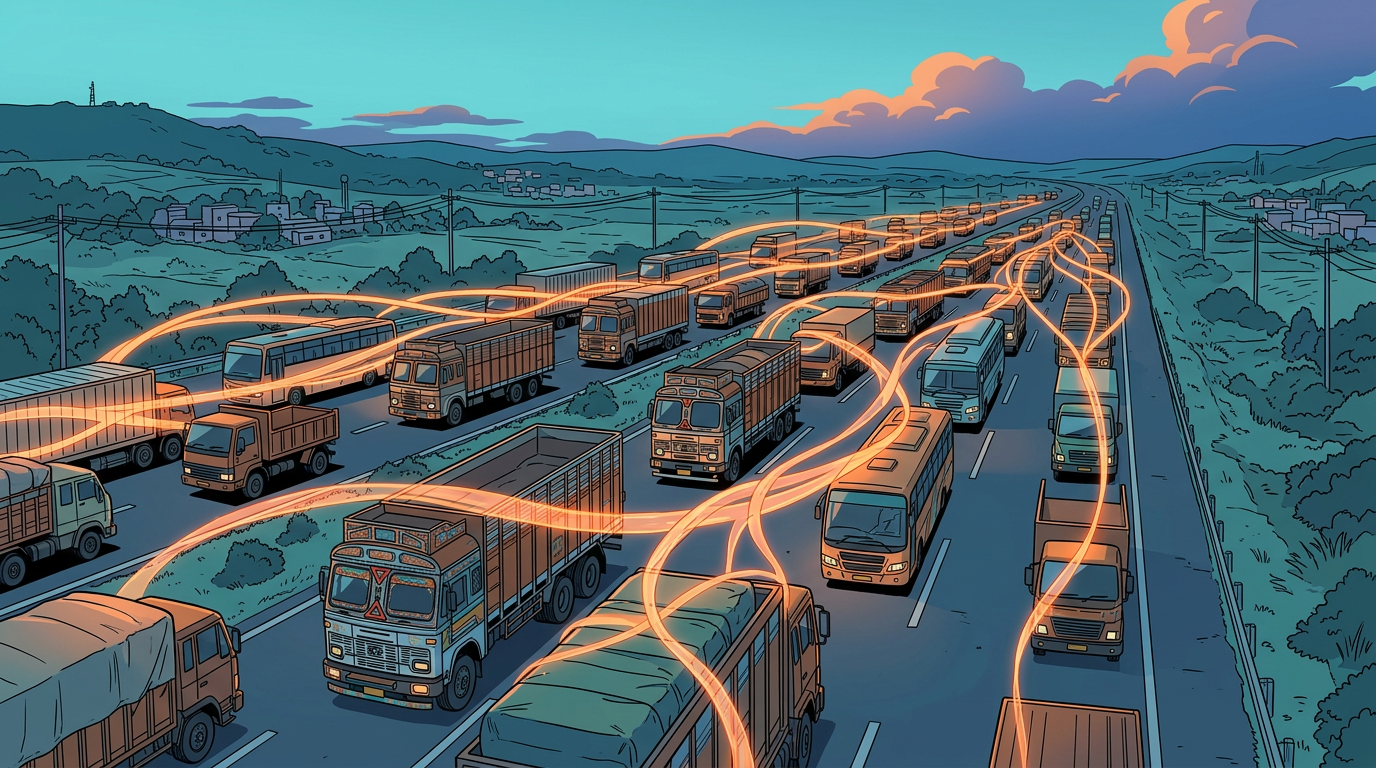
A researcher demonstrated that flaws in the My Eicher fleet platform could have handed attackers control of more than 676,000 commercial vehicles in India, along with the personal data of nearly 750,000 customers.

Eaton Zveare of Harness documented the vulnerabilities in a disclosure published July 27. My Eicher is the fleet management and GPS tracking system from VE Commercial Vehicles, the joint venture between the Volvo Group and Eicher Motors. Its customers include truck and bus operators across India.

Zveare found that walking up an API path on the platform’s website exposed a directory of hidden internal endpoints, many unauthenticated. Those endpoints returned lists of 748,000 customers, 174,000 users and 676,000 vehicles, plus 76,000 uploaded documents including Aadhaar cards and driving licenses. Another API exposed roughly 2.5 million one-time passwords going back to 2021.

By pulling the OTP for a target phone number and plugging it into the login flow, Zveare said he gained full control of any account, and by extension the entire fleet tied to it, which could span hundreds of trucks. A second method let him reset account passwords without alerting the owner.

The researcher reported the issues in November 2025. The primary vulnerability was closed that month, and the company remediated remaining concerns on July 28, days after the disclosure went public. VE Commercial Vehicles says there is no current threat to any customer or vehicle.

The case is a reminder that fleet telematics APIs can be as dangerous as vehicle ECUs. Exposed OTP stores, missing authentication and weak access controls turned a customer portal into a nationwide vehicle-takeover machine. OEMs building connected commercial fleets should treat internal APIs as attack surface and audit them for unauthenticated access before attackers do.
Join Our Newsletter
Subscribe to our newsletter to get our newest articles instantly!
TAGGED:Connected VehiclesCybersecurityData PrivacyTelematics Control Units (TCU)Vehicle SoftwareVulnerabilities
SOURCES:Eaton Zveare / My Eicher disclosureSecurityWeek
Share This Article
Facebook Email Copy Link

Follow US

Find US on Social Medias
FacebookLike
XFollow
YoutubeSubscribe

You Might Also Like

Autonomous & AI SystemsCar NewsCybersecurityPolicy & Compliance

Zoox recalls robotaxis after smoke-blind software fails at fire scene

By
ctadmin
July 18, 2026
Policy & Compliance

BYD rewrites Australian privacy policy after Four Corners questions

By
ctadmin
September 21, 2026
CybersecurityEV & Infrastructure

EV Energy charging platform flaws allow full grid hijack with no patch

By
ctadmin
July 18, 2026
Snapdragon Digital Chassis concept illustration of an electric vehicle with glowing internal components
Cybersecurity

Stellantis Pushes Hands-Free Driving With Qualcomm Snapdragon Ride Pilot

By
ctadmin
May 25, 2026
Cybersecurity

Researchers find 36 million GPS trackers open to vehicle theft

By
ctadmin
August 6, 2026
Cybersecurity

An app sold vehicle owner records for two rupees a lookup

By
ctadmin
September 30, 2026

CarThreat

Intelligence for the EV and automotive security market
  • News
  • Features
  • Spotlight
  • Events
  • About Carthreat
  • Our Mission
  • Services
  • Contact Us
  • OBD-II
  • Automotive Ethernet
  • TCU
  • Infotainment Systems
  • SDVs
  • BMS
  • ECU Security
  • CAN Bus
  • Vulnerabilities
  • Relay Attacks
  • RCE
  • Threat Intelligence
  • Cybersecurity
  • Digital Keys
  • Bluetooth Security
  • OTA Updates
  • ISO/SAE 21434
  • UNECE R155
  • Regulations
  • Data Privacy
  • EVs
  • Autonomous Driving
  • Pwn2Own Automotive

© 2026 Carthreat.com. All right reserved.  Privacy Policy | Legal

Welcome Back!

Sign in to your account

Username or Email Address
Password

Lost your password?