CarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Notification
  • Autonomous Driving
  • Automotive Ethernet
  • BMS
  • ECU
  • EV
  • ISO/SAE 21434
  • Infotainment
  • OTA Updates
  • OBD-II
  • Pwn2Own
  • RCE
  • SDVs
  • TCU
  • UNECE R155
Cybersecurity

Britain admits 125,000 public chargers have no uniform cyber bar

Cybersecurity

Bosch puts a security gatekeeper on connected motorcycles

Cybersecurity

Trucking group opens a capture-the-flag lab for mechanics

Physical Security

Two California drivers test Axon’s plate database in court

Font ResizerAa
CarThreatCarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
Search
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Sign In Sign In
Follow US
© 2026 Carthreat.com. All right reserved.
Cybersecurity

Arnold Clark concedes its own security gap enabled a 2022 raid

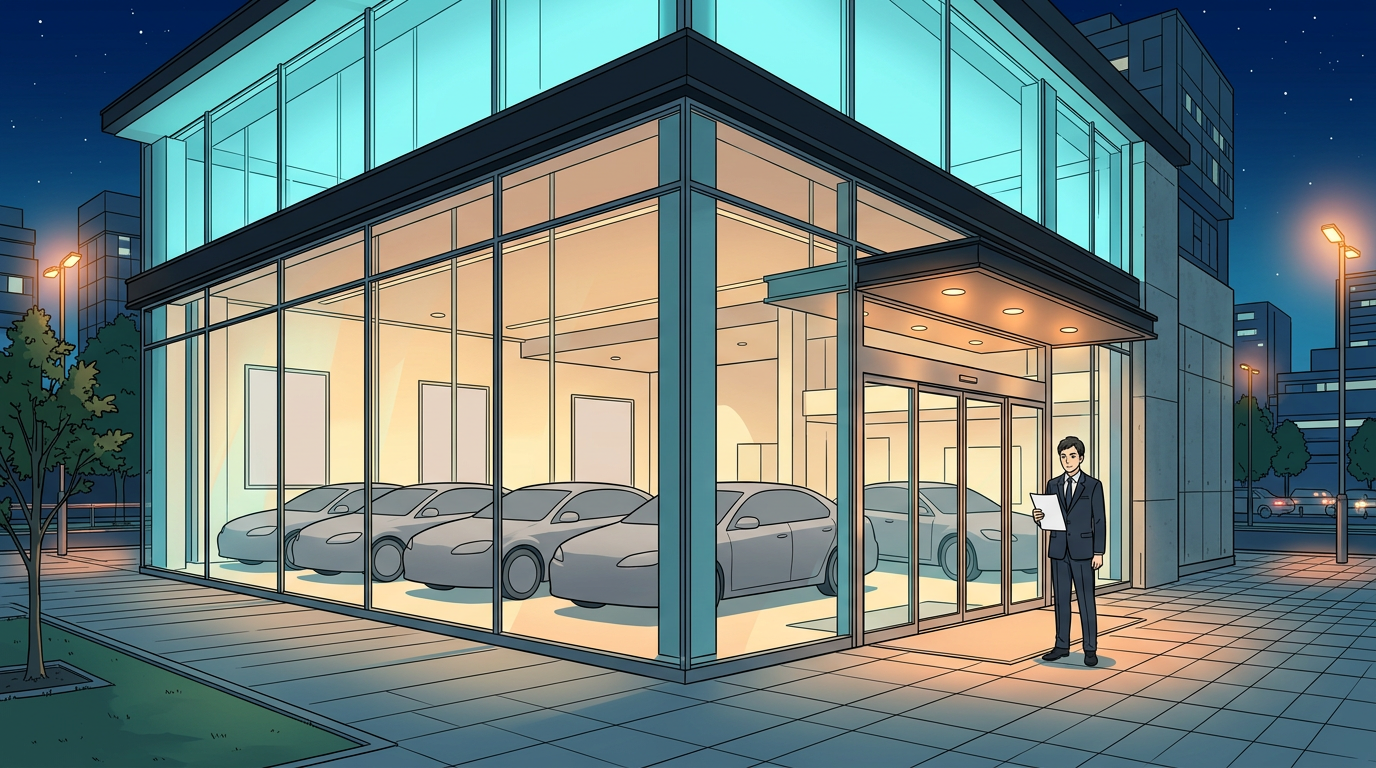
Scotland's biggest car dealer has told the Court of Session that the December 2022 intrusion would not have happened without its data protection failures.

CarThreat Staff
Last updated: October 21, 2026 3:32 am
By
ctadmin
2 Min Read
SHARE

===== 5771 =====
In a formal document lodged at the Court of Session, the dealer has conceded that its failure to protect customer information broke data protection law, and that the December 2022 intrusion could not have happened otherwise.

The admission, first reported by Newsquest titles, hands the group action a significant procedural win. In principle, the dealer accepts liability to pay members who can evidence harm. Individual claims and the size of any award remain open, and the company has reserved its position on causation and quantum.

## What the attackers took

The intrusion ran on the evening of December 23, 2022. The network came down on Christmas Eve 2022 as investigators moved in. Notification to customers followed in January and February 2023, once extraction of data had been established.

What the attackers are thought to have carried off spans names, addresses, birth dates, vehicle and contact details, National Insurance numbers, passport and driving licence copies, and banking details. Some customers were told unsigned finance agreements from 2019 and earlier may also have been stolen. The firm offered two years of Experian monitoring.

## The claim runs in two jurisdictions

Filed as Robert Adamson v Arnold Clark Automobiles Limited, the action proceeds under Chapter 26A of the Rules of the Court of Session, reference GP9-26. Lord Sandison earlier approved the Scottish group after rejecting the dealer’s argument that England was the better forum, noting more than 95 per cent of proposed members lived in Scotland.

Jones Whyte, which represents over 3,000 people in the Scottish action, says the number may grow. Eligibility is understood to cover roughly 15,000 motorists. Parallel English proceedings continue, with the company’s lawyers signalling a comparable stance there.
Join Our Newsletter
Subscribe to our newsletter to get our newest articles instantly!
TAGGED:Connected VehiclesCybersecurityData PrivacyRegulationsThreat Intelligence
SOURCES:Glasgow TimesDumbarton and Vale of Leven Reporter
Share This Article
Facebook Email Copy Link

Follow US

Find US on Social Medias
FacebookLike
XFollow
YoutubeSubscribe

You Might Also Like

Cybersecurity

BYD pins the Shark 6 hack on a software defect

By
ctadmin
October 2, 2026
Cybersecurity

Stellantis Deploys AI Digital Twins Across Global Plants with Nvidia and Accenture

By
ctadmin
May 22, 2026
Policy & Compliance

UN takes its automated driving rulebook on tour through Beijing

By
ctadmin
October 30, 2026
Cybersecurity

4D LiDAR Traffic Platform Chosen for Snowy City Intersections to Improve Road Safety

By
ctadmin
June 12, 2026
Physical Security

Two California drivers test Axon’s plate database in court

By
ctadmin
November 6, 2026
Cybersecurity

rFpro Extends AV Simulation Platform With Cabin Monitoring Support

By
ctadmin
June 12, 2026

CarThreat

Intelligence for the EV and automotive security market
  • News
  • Features
  • Spotlight
  • Events
  • About Carthreat
  • Our Mission
  • Services
  • Contact Us
  • OBD-II
  • Automotive Ethernet
  • TCU
  • Infotainment Systems
  • SDVs
  • BMS
  • ECU Security
  • CAN Bus
  • Relay Attacks
  • RCE
  • Threat Intelligence
  • Cybersecurity
  • Digital Keys
  • Bluetooth Security
  • OTA Updates
  • Vulnerabilities
  • UNECE R155
  • Regulations
  • Data Privacy
  • EVs
  • Autonomous Driving
  • Pwn2Own Automotive
  • ISO/SAE 21434

© 2026 Carthreat.com. All right reserved.  Privacy Policy | Legal

Welcome Back!

Sign in to your account

Username or Email Address
Password

Lost your password?