CarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Notification
  • Autonomous Driving
  • Automotive Ethernet
  • BMS
  • ECU
  • EV
  • ISO/SAE 21434
  • Infotainment
  • OTA Updates
  • OBD-II
  • Pwn2Own
  • RCE
  • SDVs
  • TCU
  • UNECE R155
Cybersecurity

Britain admits 125,000 public chargers have no uniform cyber bar

Cybersecurity

Bosch puts a security gatekeeper on connected motorcycles

Cybersecurity

Trucking group opens a capture-the-flag lab for mechanics

Physical Security

Two California drivers test Axon’s plate database in court

Font ResizerAa
CarThreatCarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
Search
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Sign In Sign In
Follow US
© 2026 Carthreat.com. All right reserved.
Policy & Compliance

Michigan puts dealer data behind a locked counter

Michigan's new dealer data law fences off customer records inside dealership systems but leaves vehicle-generated data outside its reach.

CarThreat Staff
Last updated: October 17, 2026 2:02 am
By
ctadmin
2 Min Read
SHARE

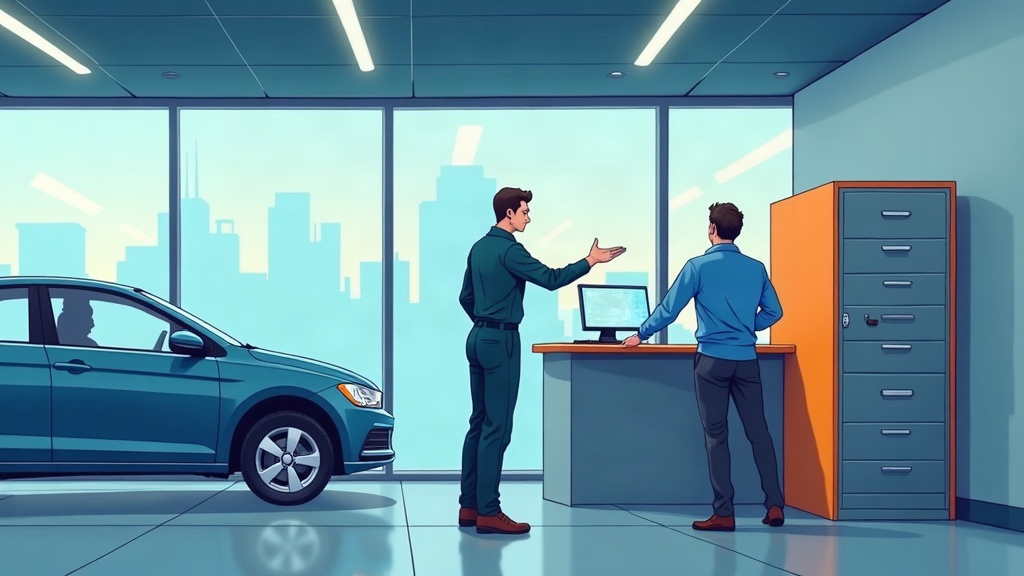
Inside a franchise dealership’s computer systems sits a trove of records, and Michigan has drawn a line around who may reach it. The state’s answer is the Motor Vehicle Dealer Data Collection Act. Lawmakers numbered it Public Act 113 of 2026. It took effect October 9, the day it won the governor’s signature.

Contents
Three protected categoriesGaps in the statuteDuties on the vendorsThe stakes

Three protected categories

A dealership’s systems hold data in three protected forms. Records about the dealer’s own business count, and so do customer information and vehicle diagnostic data. Most of that data lives inside a dealership management system.

No outside vendor can compel a dealer to hand over access, and neither can a manufacturer. Diagnostic data is where manufacturers keep a narrower path. Warranty claims and recall notices stay open to them, since what those require needs no consent.

Gaps in the statute

Vehicle diagnostic data does not become dealer property because of the act, nor do the use and sharing rights belong to dealers, beyond what warranty, repair, or service work needs. Data generated outside dealership systems also sits beyond the statute’s scope.

That gap lands on collision and repair shops. Telemetry from the vehicle itself, plus connected-car feeds that never touch a dealer’s software, stay outside the law’s reach.

Duties on the vendors

Vendors warehousing dealer data carry their own duties: open integration, a 90-day exit window once a dealer gives notice, and no withholding of access to collect payments no written contract agreed to.

The stakes

One platform, a dealership management system, concentrates purchase prices, financing terms, and customer identities together. Attackers hit that profile this month in Germany, where a single supplier flaw exposed buyer records at hundreds of Volkswagen Group retailers.

Michigan built a data-access boundary, not a security mandate, settling who may pull records and who may be refused.
Join Our Newsletter
Subscribe to our newsletter to get our newest articles instantly!
TAGGED:Connected VehiclesCybersecurityData PrivacyDealer NetworksPolicyRegulationsVehicle Software
SOURCES:Autobody News
Share This Article
Facebook Email Copy Link

Follow US

Find US on Social Medias
FacebookLike
XFollow
YoutubeSubscribe

You Might Also Like

Physical Security

Ohio cameras become targets as plate reader backlash turns physical

By
ctadmin
October 20, 2026
Physical Security

Columbus closes a theft lawsuit against Kia and Hyundai for $1M

By
ctadmin
September 28, 2026
Policy & Compliance

Wisconsin lawsuit demands warrants before police search plate data

By
ctadmin
September 12, 2026
CybersecurityPhysical Security

Franklin County audit finds a deputy inside the plate database

By
ctadmin
November 2, 2026
Policy & Compliance

How the EU Cyber Resilience Act Reshapes Compliance for Software Defined Vehicles

By
ctadmin
June 19, 2026
Policy & Compliance

Carmakers’ lobby presses Congress to bar Chinese connected vehicles this year

By
ctadmin
September 5, 2026

CarThreat

Intelligence for the EV and automotive security market
  • News
  • Features
  • Spotlight
  • Events
  • About Carthreat
  • Our Mission
  • Services
  • Contact Us
  • OBD-II
  • Automotive Ethernet
  • TCU
  • Infotainment Systems
  • SDVs
  • BMS
  • ECU Security
  • CAN Bus
  • OTA Updates
  • Vulnerabilities
  • Relay Attacks
  • RCE
  • Threat Intelligence
  • Cybersecurity
  • Digital Keys
  • Bluetooth Security
  • ISO/SAE 21434
  • UNECE R155
  • Regulations
  • Data Privacy
  • EVs
  • Autonomous Driving
  • Pwn2Own Automotive

© 2026 Carthreat.com. All right reserved.  Privacy Policy | Legal

Welcome Back!

Sign in to your account

Username or Email Address
Password

Lost your password?