CarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Notification
  • Autonomous Driving
  • Automotive Ethernet
  • BMS
  • ECU
  • EV
  • ISO/SAE 21434
  • Infotainment
  • OTA Updates
  • OBD-II
  • Pwn2Own
  • RCE
  • SDVs
  • TCU
  • UNECE R155
India's two-part cyber rulebook now has a certification trail
Cybersecurity

India’s two-part cyber rulebook now has a certification trail

Colmobil shuts some counters after intruders reach its network
Cybersecurity

Colmobil shuts some counters after intruders reach its network

A supplier flaw handed car buyers' payment records to criminals
Cybersecurity

A supplier flaw handed car buyers’ payment records to criminals

Physical Security

Rental cars stored video of Norwegian troops and gate codes

Font ResizerAa
CarThreatCarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
Search
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Sign In Sign In
Follow US
© 2026 Carthreat.com. All right reserved.
CybersecurityEV & Infrastructure

Hydro-Quebec EV charger websocket bug opens door to privilege escalation

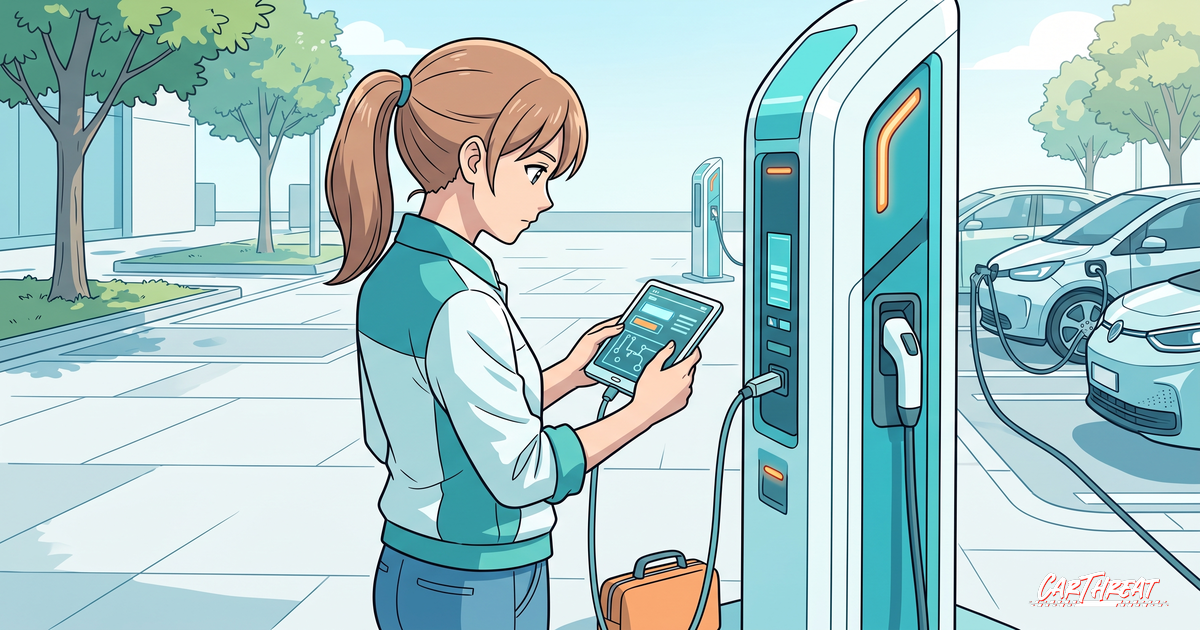
A critical privilege escalation vulnerability affecting Hydro-Quebec’s Le Circuit Electrique EV charging station network has been disclosed, tracked as CVE-2026-20744.

CarThreat Staff
Last updated: July 18, 2026 7:24 am
By
ctadmin
2 Min Read
SHARE

A critical privilege escalation vulnerability affecting Hydro-Quebec’s Le Circuit Electrique electric vehicle charging station network has been disclosed, tracked as CVE-2026-20744.

The flaw originates in the charging station’s WebSocket endpoint, which accepts connections without requiring proper authentication. Researchers found that the backend infrastructure allows unauthenticated parties to establish communication channels that should be restricted to authorized management systems. This oversight can lead to privilege escalation, enabling unauthorized users to access sensitive backend functionalities.

The vulnerability was classified as an improper access control issue within the charging network’s infrastructure. The WebSocket protocol is used by the charging stations to communicate with the central management platform for status updates, charging session data, and remote commands. Without authentication gates on these endpoints, an attacker who identifies a station’s WebSocket address can inject commands or extract operational data.

Hydro-Quebec operates one of the largest public EV charging networks in Canada, with hundreds of stations across Quebec. The Le Circuit Electrique network supports multiple connector types and provides charging services for both casual users and commercial fleets.

The utility has implemented authentication improvements for certain charging stations that rely on the OCPP protocol. However, the advisory notes that not all stations may be fully protected depending on their specific configuration and firmware version. Hydro-Quebec recommends that operators contact the company directly to verify their charging equipment’s security posture.

Security researchers noted that EV charger backend vulnerabilities are particularly concerning because they can affect multiple stations simultaneously through a single platform weakness, rather than requiring individual physical access to each charger.
Join Our Newsletter
Subscribe to our newsletter to get our newest articles instantly!
TAGGED:CanadaCVE-2026-20744EV chargerHydro-QuebecLe Circuit ElectriqueOCPPPrivilege EscalationWebSocket
SOURCES:SecurityOnlineCVE Feed
Share This Article
Facebook Email Copy Link

Follow US

Find US on Social Medias
FacebookLike
XFollow
YoutubeSubscribe

You Might Also Like

Cybersecurity

Vehicle security must follow what an AI agent does next

By
ctadmin
September 29, 2026
Cybersecurity

City cameras could expose fake vehicles clogging navigation apps

By
ctadmin
August 13, 2026
Cybersecurity

ECARX and TPK Partner on ORCA LiDAR Platform Targeting ADAS and Robotaxi Security

By
ctadmin
May 30, 2026
Cybersecurity

Risk scoring framework cuts attack success in autonomous vehicles

By
ctadmin
August 13, 2026
Cybersecurity

Indiana prosecutors turn plate reader misuse into criminal charges

By
ctadmin
September 26, 2026
Canada's privacy commissioner opens a PIPEDA probe into IDScan.net
Cybersecurity

Canada’s privacy commissioner opens a PIPEDA probe into IDScan.net

By
ctadmin
September 25, 2026

CarThreat

Intelligence for the EV and automotive security market
  • News
  • Features
  • Spotlight
  • Events
  • About Carthreat
  • Our Mission
  • Services
  • Contact Us
  • OBD-II
  • Automotive Ethernet
  • TCU
  • Infotainment Systems
  • SDVs
  • BMS
  • ECU Security
  • CAN Bus
  • Threat Intelligence
  • Cybersecurity
  • Digital Keys
  • Bluetooth Security
  • OTA Updates
  • Vulnerabilities
  • Relay Attacks
  • RCE
  • Data Privacy
  • EVs
  • Autonomous Driving
  • Pwn2Own Automotive
  • ISO/SAE 21434
  • UNECE R155
  • Regulations

© 2026 Carthreat.com. All right reserved.  Privacy Policy | Legal

Welcome Back!

Sign in to your account

Username or Email Address
Password

Lost your password?