CarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Notification
  • Autonomous Driving
  • Automotive Ethernet
  • BMS
  • ECU
  • EV
  • ISO/SAE 21434
  • Infotainment
  • OTA Updates
  • OBD-II
  • Pwn2Own
  • RCE
  • SDVs
  • TCU
  • UNECE R155
India's two-part cyber rulebook now has a certification trail
Cybersecurity

India’s two-part cyber rulebook now has a certification trail

Colmobil shuts some counters after intruders reach its network
Cybersecurity

Colmobil shuts some counters after intruders reach its network

A supplier flaw handed car buyers' payment records to criminals
Cybersecurity

A supplier flaw handed car buyers’ payment records to criminals

Physical Security

Rental cars stored video of Norwegian troops and gate codes

Font ResizerAa
CarThreatCarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
Search
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Sign In Sign In
Follow US
© 2026 Carthreat.com. All right reserved.
Cybersecurity

US Bans Polestar EV Sales Under National Security Connected Vehicle Rule

CarThreat Staff
Last updated: July 1, 2026 1:52 am
By
ctadmin
2 Min Read
SHARE

Regulatory Action and Ownership Nexus

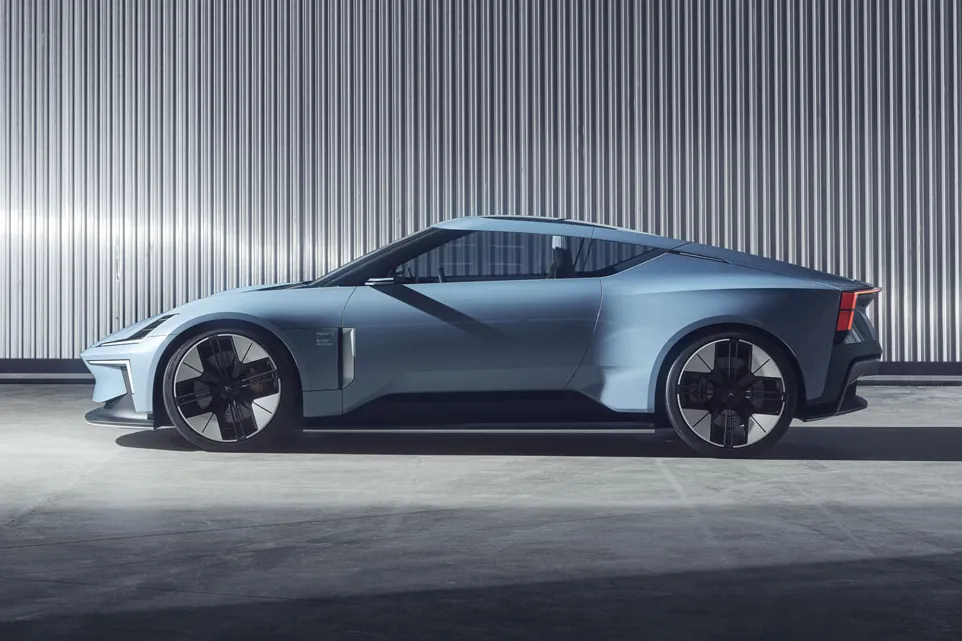
The U.S. Commerce Department’s Bureau of Industry and Security has refused to grant Polestar authorization to sell its vehicles in the American market, starting with the 2027 model year. This decision stems from the Connected Vehicle Rule, finalized in January 2025, which restricts importation and sale of vehicles with connected technology linked to China or Russia. Polestar is majority owned by China’s Geely Holding Co., triggering the rule despite the Polestar 3 being built in South Carolina and the Polestar 4 in South Korea, neither of which are assembled in China.

Contents
Regulatory Action and Ownership NexusImpact on Automotive Supply Chain and OEM Strategy

The rule covers telematics, cameras, microphones, GPS, Bluetooth, cellular modules, and automated driving software across all vehicle types. Software prohibitions take effect for model year 2027, with hardware restrictions following in 2030. This effectively ends new car sales in the U.S. for the Swedish electric vehicle brand, as its ownership structure creates a sufficient nexus to China under the regulation.

Impact on Automotive Supply Chain and OEM Strategy

Volvo Cars, also owned by Geely, received authorization to continue U.S. sales, reflecting its status as a separately listed automaker with a larger American footprint and less direct entanglement with Geely’s corporate structure. The disparate treatment between Volvo and Polestar signals a clear precedent: any automaker with Chinese capital upstream, regardless of where vehicles are actually manufactured, faces potential exclusion from the U.S. market under this rule.

Polestar CEO Michael Lohscheller announced a strategic pivot toward Europe, which represents nearly 80% of the brand’s retail volumes. The company also plans to target growth markets in Southeast Asia, Eastern Europe, Latin America, and Canada. This case demonstrates that connected vehicle regulations can effectively wall off brands based on ownership rather than manufacturing location, directly impacting OEM supply chain strategies, global market access planning, and the viability of cross border connected vehicle technology deployments.

Source: Axios
Join Our Newsletter
Subscribe to our newsletter to get our newest articles instantly!
TAGGED:Automotive RegulationConnected Vehicle RuleGeelyMarket AccessPolestarSupply Chain Security
Share This Article
Facebook Email Copy Link

Follow US

Find US on Social Medias
FacebookLike
XFollow
YoutubeSubscribe

You Might Also Like

Cybersecurity

Automotive Cybersecurity Market Forecast Predicts $3.14 Billion by 2033 as Connected Vehicle Risks Mount

By
ctadmin
June 19, 2026
Cybersecurity

EV salary scheme broker driver records listed for $600

By
ctadmin
August 31, 2026
Canada's privacy commissioner opens a PIPEDA probe into IDScan.net
Cybersecurity

Canada’s privacy commissioner opens a PIPEDA probe into IDScan.net

By
ctadmin
September 25, 2026
Cybersecurity

DIY firewall blocks CAN injection attacks on truck data buses

By
ctadmin
August 12, 2026
Cybersecurity

Miami pair accused of jamming trackers to take luxury cars

By
ctadmin
October 5, 2026
Cybersecurity

Nordic Regulators Block Tesla FSD Over Speed Limit Bypass Feature

By
ctadmin
June 30, 2026

CarThreat

Intelligence for the EV and automotive security market
  • News
  • Features
  • Spotlight
  • Events
  • About Carthreat
  • Our Mission
  • Services
  • Contact Us
  • OBD-II
  • Automotive Ethernet
  • TCU
  • Infotainment Systems
  • SDVs
  • BMS
  • ECU Security
  • CAN Bus
  • OTA Updates
  • Vulnerabilities
  • Relay Attacks
  • RCE
  • Threat Intelligence
  • Cybersecurity
  • Digital Keys
  • Bluetooth Security
  • ISO/SAE 21434
  • UNECE R155
  • Regulations
  • Data Privacy
  • EVs
  • Autonomous Driving
  • Pwn2Own Automotive

© 2026 Carthreat.com. All right reserved.  Privacy Policy | Legal

Welcome Back!

Sign in to your account

Username or Email Address
Password

Lost your password?