CarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Notification
  • Autonomous Driving
  • Automotive Ethernet
  • BMS
  • ECU
  • EV
  • ISO/SAE 21434
  • Infotainment
  • OTA Updates
  • OBD-II
  • Pwn2Own
  • RCE
  • SDVs
  • TCU
  • UNECE R155
India's two-part cyber rulebook now has a certification trail
Cybersecurity

India’s two-part cyber rulebook now has a certification trail

Colmobil shuts some counters after intruders reach its network
Cybersecurity

Colmobil shuts some counters after intruders reach its network

A supplier flaw handed car buyers' payment records to criminals
Cybersecurity

A supplier flaw handed car buyers’ payment records to criminals

Physical Security

Rental cars stored video of Norwegian troops and gate codes

Font ResizerAa
CarThreatCarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
Search
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Sign In Sign In
Follow US
© 2026 Carthreat.com. All right reserved.
Cybersecurity

A Peterbilt lab hunts intruders on the truck data bus

A Waterloo team is using a working semi to find where an attacker could slip onto a truck network.

CarThreat Staff
Last updated: October 3, 2026 12:20 am
By
ctadmin
2 Min Read
SHARE

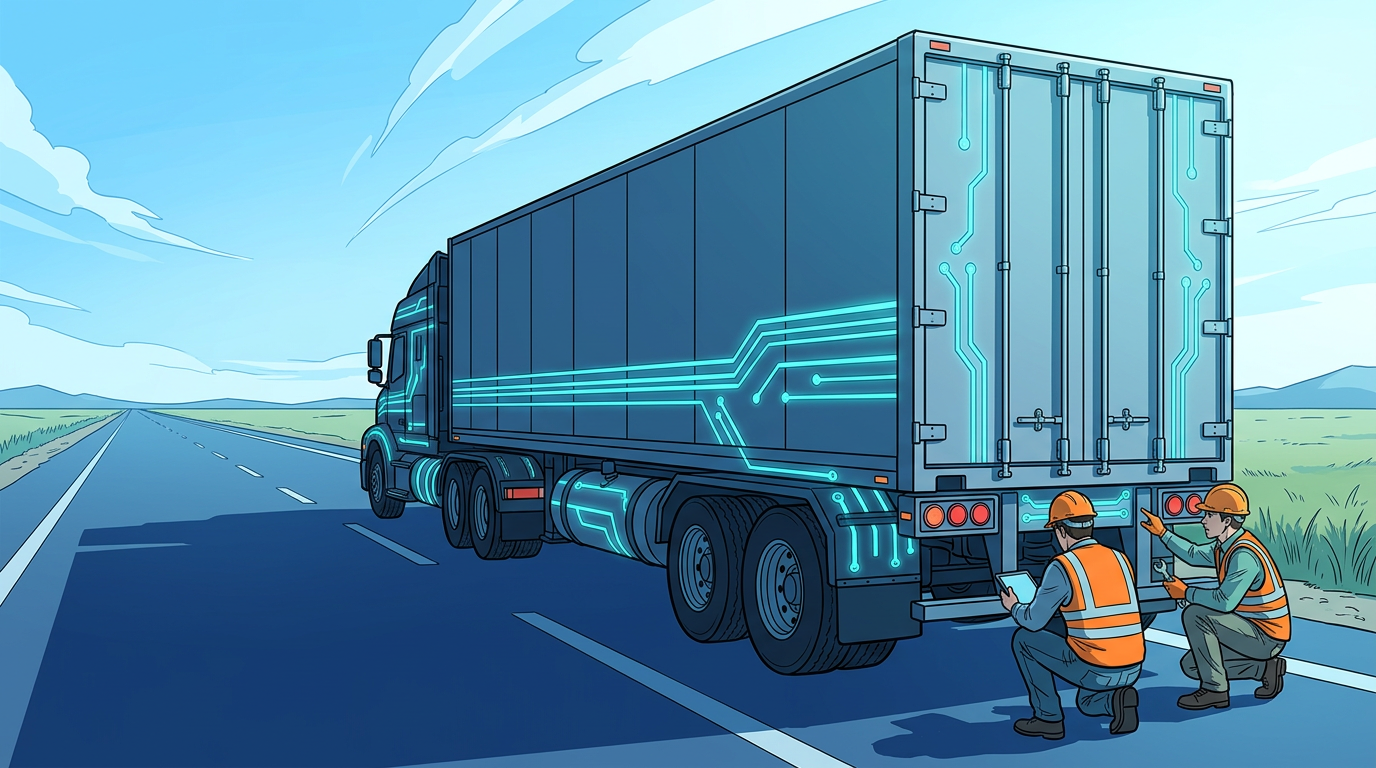
Most passenger cars keep their wiring a secret. Heavy trucks do not, and that difference is why a security group at the University of Waterloo is using one as a rolling laboratory. Professor Sebastian Fischmeister and his team are probing a Peterbilt supplied by Challenger Motor Freight for the weak points an attacker could use, and for the earliest signs that someone is already inside.

The project pulls together Transport Canada, Challenger, Geotab, the Automotive Parts Manufacturers’ Association and the European firm EVList. The truck gives the researchers something a bench cannot: live traffic on SAE J1939, the open standard that carries messages across heavy-vehicle networks. Passenger cars bury their architectures in proprietary designs, which makes traffic hard to decode. J1939 can be read, modeled and tested.

Beneath it sits the Controller Area Network, and with it a flaw engineers have known about for years. The bus has no sender authentication, so a device on the network can broadcast a message pretending to be another part. It does not encrypt, either. Once someone is on the bus, that gap opens the door to impersonating an electronic control unit, which matters when braking and acceleration travel as messages.

So the work looks past keeping intruders out. It weighs whether a truck can tell that a message did not come from the part it claims to represent, and how quickly an intrusion can be caught before it reaches systems a driver depends on.

Commercial fleets are a softer target than many assume. Telematics units, logging apps and dealer add-ons widen the surface, and trucks stay in service far longer than cars. Proving that a working semi can flag a counterfeit message is the first step toward hardware that does it on the road.
Join Our Newsletter
Subscribe to our newsletter to get our newest articles instantly!
TAGGED:CAN BusCybersecurityECU SecurityTelematics Control Units (TCU)Vehicle SoftwareVulnerabilities
SOURCES:Truck News
Share This Article
Facebook Email Copy Link

Follow US

Find US on Social Medias
FacebookLike
XFollow
YoutubeSubscribe

You Might Also Like

CybersecurityEV & Infrastructure

EV Energy charging platform flaws allow full grid hijack with no patch

By
ctadmin
July 18, 2026
Electric Vehicles

Fake plug-and-charge stations bill EV owners for stranger fills

By
ctadmin
August 9, 2026
Cybersecurity

EV charger worm escapes a Tesla wall plug and hops to rival brands

By
ctadmin
August 22, 2026
Cybersecurity

ZF gives city buses automated steering and suspension for precision docking

By
ctadmin
July 21, 2026
Cybersecurity

Botslab dash cams ship with 13 flaws and no fix in sight

By
ctadmin
September 26, 2026
CybersecurityIndustry & Culture

Tata Electronics breach leaks Apple and Tesla supply chain secrets

By
ctadmin
July 18, 2026

CarThreat

Intelligence for the EV and automotive security market
  • News
  • Features
  • Spotlight
  • Events
  • About Carthreat
  • Our Mission
  • Services
  • Contact Us
  • OBD-II
  • Automotive Ethernet
  • TCU
  • Infotainment Systems
  • SDVs
  • BMS
  • ECU Security
  • CAN Bus
  • OTA Updates
  • Vulnerabilities
  • Relay Attacks
  • RCE
  • Threat Intelligence
  • Cybersecurity
  • Digital Keys
  • Bluetooth Security
  • ISO/SAE 21434
  • UNECE R155
  • Regulations
  • Data Privacy
  • EVs
  • Autonomous Driving
  • Pwn2Own Automotive

© 2026 Carthreat.com. All right reserved.  Privacy Policy | Legal

Welcome Back!

Sign in to your account

Username or Email Address
Password

Lost your password?