CarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Notification
  • Autonomous Driving
  • Automotive Ethernet
  • BMS
  • ECU
  • EV
  • ISO/SAE 21434
  • Infotainment
  • OTA Updates
  • OBD-II
  • Pwn2Own
  • RCE
  • SDVs
  • TCU
  • UNECE R155
India's two-part cyber rulebook now has a certification trail
Cybersecurity

India’s two-part cyber rulebook now has a certification trail

Colmobil shuts some counters after intruders reach its network
Cybersecurity

Colmobil shuts some counters after intruders reach its network

A supplier flaw handed car buyers' payment records to criminals
Cybersecurity

A supplier flaw handed car buyers’ payment records to criminals

Physical Security

Rental cars stored video of Norwegian troops and gate codes

Font ResizerAa
CarThreatCarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
Search
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Sign In Sign In
Follow US
© 2026 Carthreat.com. All right reserved.
Cybersecurity

Used car head units leak keys that hijack their last owner’s phone

Researchers pulled Bluetooth pairing keys from a salvaged 2016 Honda Pilot head unit and used them to impersonate the stereo to the previous owner's phone.

CarThreat Staff
Last updated: August 10, 2026 9:24 pm
By
ctadmin
2 Min Read
SHARE

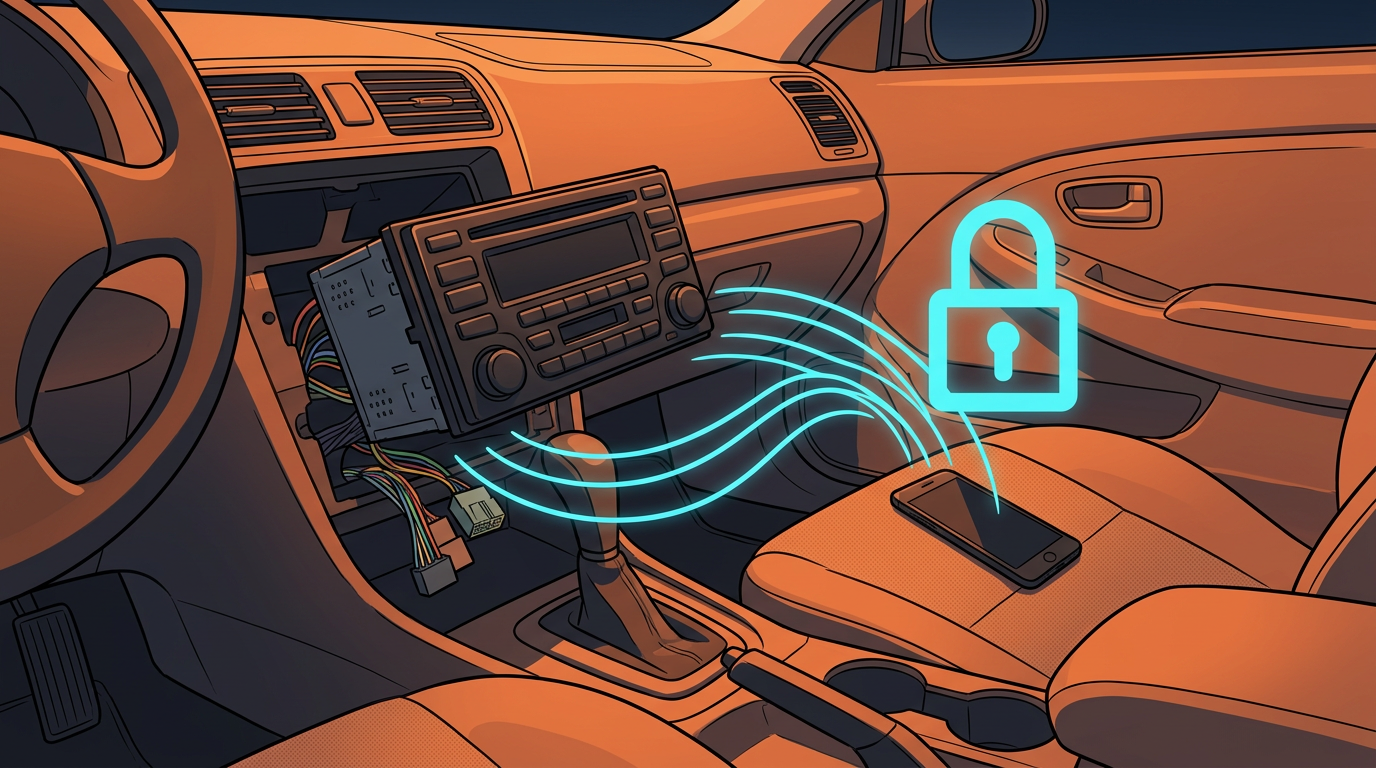
The phone you connected to your old car may still be talking to it, long after the car belongs to someone else. Researchers at the University of Memphis found that used infotainment stereos keep the Bluetooth credentials of every handset ever paired with them, together with personal records from the previous owner.

Their demonstration started with a wrecked 2016 Honda Pilot head unit bought as salvage. After pulling the BR/EDR link keys from the stereo, the team could pose as the head unit to any phone that had previously paired with it. The handset assumes it is reconnecting with the vehicle and restores the access it once granted, including hands-free calling, contact and call-log permissions, and messaging profiles.

From there, an attacker can silently read SMS one-time passwords, record calls, or wake the phone’s voice assistant, and the team succeeded in several of these scenarios even when the phone was locked. Data recovered alongside the keys, such as names, addresses, GPS breadcrumbs, and lists of paired gadgets, makes it easy to pick a specific victim rather than gamble on a random one.

Millions of used cars pass through auctions and resellers with their infotainment systems never wiped, so stale pairing state is common. The research team says the practical defenses are simple: unpair phones before selling and factory-reset the stereo, while automakers should clear pairing keys automatically when ownership changes.

The finding stands apart from the usual keyless-entry theft stories because the target is the driver’s digital identity, not the vehicle. The attack chain was presented live at the VehicleSec ’26 demo session in Baltimore.
Join Our Newsletter
Subscribe to our newsletter to get our newest articles instantly!
TAGGED:Bluetooth SecurityConnected VehiclesData PrivacyInfotainment SystemsResearchTelematics Control Units (TCU)Vulnerabilities
SOURCES:USENIX VehicleSec '26
Share This Article
Facebook Email Copy Link

Follow US

Find US on Social Medias
FacebookLike
XFollow
YoutubeSubscribe

You Might Also Like

Cybersecurity

NHTSA tells self-driving car makers to stop blocking ambulances

By
ctadmin
July 12, 2026
Policy & Compliance

Missouri’s governor orders a 30-day limit on plate reader data

By
ctadmin
September 17, 2026
Cybersecurity

Vehicles are getting their own offline AI brain thanks to FEV and Microsoft

By
ctadmin
July 12, 2026
Anime illustration of a fleet van whose rooftop telematics signal breaks apart
Cybersecurity

Fleet tracker Cartrack draws a South African privacy probe after August ransomware

By
ctadmin
September 19, 2026
Cybersecurity

Leapmotor EVs carry cameras from a supplier Australia banned

By
ctadmin
September 21, 2026
Cybersecurity

Vector Solectrix Collaboration Targets ADAS and Autonomous Driving Validation

By
ctadmin
May 22, 2026

CarThreat

Intelligence for the EV and automotive security market
  • News
  • Features
  • Spotlight
  • Events
  • About Carthreat
  • Our Mission
  • Services
  • Contact Us
  • OBD-II
  • Automotive Ethernet
  • TCU
  • Infotainment Systems
  • SDVs
  • BMS
  • ECU Security
  • CAN Bus
  • OTA Updates
  • Vulnerabilities
  • Relay Attacks
  • RCE
  • Threat Intelligence
  • Cybersecurity
  • Digital Keys
  • Bluetooth Security
  • ISO/SAE 21434
  • UNECE R155
  • Regulations
  • Data Privacy
  • EVs
  • Autonomous Driving
  • Pwn2Own Automotive

© 2026 Carthreat.com. All right reserved.  Privacy Policy | Legal

Welcome Back!

Sign in to your account

Username or Email Address
Password

Lost your password?