CarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Notification
  • Autonomous Driving
  • Automotive Ethernet
  • BMS
  • ECU
  • EV
  • ISO/SAE 21434
  • Infotainment
  • OTA Updates
  • OBD-II
  • Pwn2Own
  • RCE
  • SDVs
  • TCU
  • UNECE R155
India's two-part cyber rulebook now has a certification trail
Cybersecurity

India’s two-part cyber rulebook now has a certification trail

Colmobil shuts some counters after intruders reach its network
Cybersecurity

Colmobil shuts some counters after intruders reach its network

A supplier flaw handed car buyers' payment records to criminals
Cybersecurity

A supplier flaw handed car buyers’ payment records to criminals

Physical Security

Rental cars stored video of Norwegian troops and gate codes

Font ResizerAa
CarThreatCarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
Search
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Sign In Sign In
Follow US
© 2026 Carthreat.com. All right reserved.
CybersecurityEV & Infrastructure

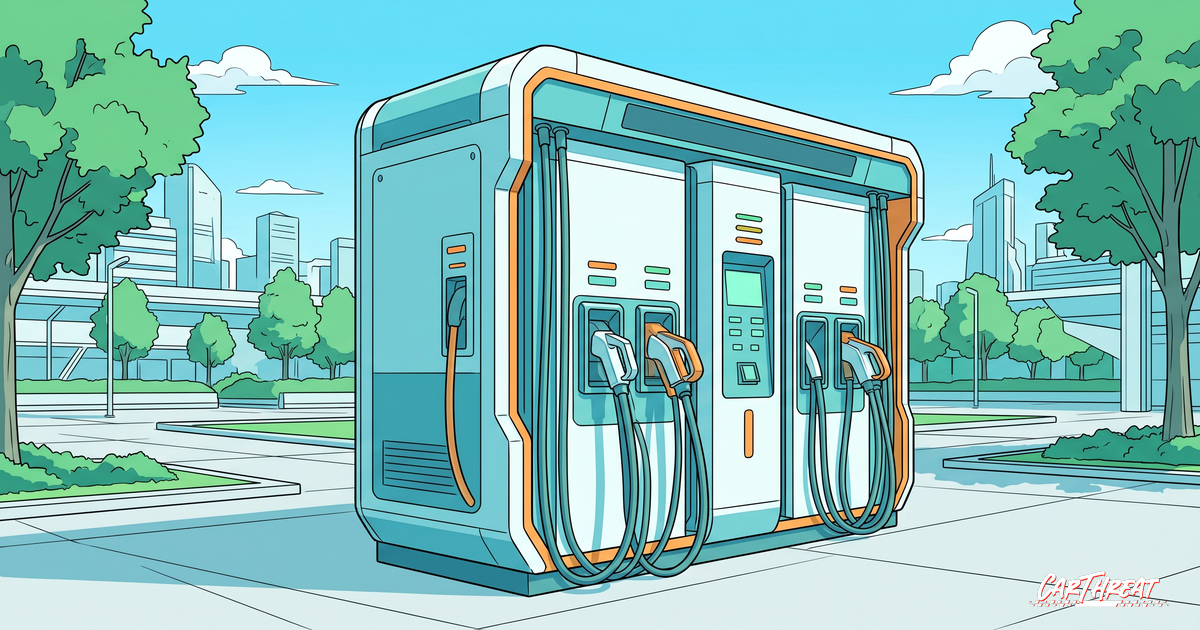
CISA warns of critical flaws in XCharge C6 EV charging stations

The Cybersecurity and Infrastructure Security Agency issued an advisory warning that XCharge C6 EV charging controllers contain three security flaws, including one rated critical with a CVSS score of 9.8.

CarThreat Staff
Last updated: July 18, 2026 7:24 am
By
ctadmin
2 Min Read
SHARE

The Cybersecurity and Infrastructure Security Agency issued an advisory warning that XCharge C6 electric vehicle charging controllers contain three security flaws, including one rated critical with a CVSS score of 9.8.

The most severe vulnerability, tracked as CVE-2026-9037, involves a missing firmware validation mechanism that allows attackers to execute arbitrary code on the device by connecting a malicious unit through the charging port. The flaw stems from the controller’s failure to cryptographically verify update packages before installation.

CVE-2026-9038 describes a stack-based buffer overflow in the device’s SLAC protocol handling, a communication standard used in vehicle-to-grid connections. An attacker physically connected to the charger can trigger memory corruption that leads to remote code execution. Research demonstrated that any EV charger using Qualcomm’s open-plc-utils library could be vulnerable to related issues.

The third vulnerability, CVE-2026-9039, exposes a configuration weakness in the remote management service that allows an authenticated session to be established over a communication channel intended solely for vehicle-charger signaling. The service accepts default administrative credentials accessible through interfaces exposed via the charging connector.

CISA rated the first two vulnerabilities as critical and the third as high severity. The devices are deployed in transportation environments worldwide, and while no public exploitation has been reported yet, experts warn that the physical accessibility of charging stations makes them attractive targets for attackers seeking grid-level disruption.

XCharge has not released a coordinated patch timeline. CISA recommends that operators isolate the charging controllers from corporate networks and restrict physical access to authorized personnel only.
Join Our Newsletter
Subscribe to our newsletter to get our newest articles instantly!
TAGGED:C6CISACVE-2026-9037CVE-2026-9038CVE-2026-9039EV chargerRemote Code ExecutionXCharge
SOURCES:CISASecurityOnline
Share This Article
Facebook Email Copy Link

Follow US

Find US on Social Medias
FacebookLike
XFollow
YoutubeSubscribe

You Might Also Like

Cybersecurity

Smart Edge Architecture Wins PlaxidityX vCore the AutoTech Cybersecurity Excellence Award

By
ctadmin
June 4, 2026
Cybersecurity

Vehicle security must follow what an AI agent does next

By
ctadmin
September 29, 2026
Cybersecurity

Automotive IQ names its top 20 cybersecurity leaders for 2026

By
ctadmin
July 12, 2026
Cybersecurity

Indiana prosecutors turn plate reader misuse into criminal charges

By
ctadmin
September 26, 2026
Anime illustration of a rental counter ID scanner leaking license data into a dark void
Cybersecurity

Rental car ID scans linked to 153 million license trove

By
ctadmin
September 3, 2026
Cybersecurity

Boston police tested Motorola and Axon readers as Flock exited

By
ctadmin
September 21, 2026

CarThreat

Intelligence for the EV and automotive security market
  • News
  • Features
  • Spotlight
  • Events
  • About Carthreat
  • Our Mission
  • Services
  • Contact Us
  • OBD-II
  • Automotive Ethernet
  • TCU
  • Infotainment Systems
  • SDVs
  • BMS
  • ECU Security
  • CAN Bus
  • OTA Updates
  • Vulnerabilities
  • Relay Attacks
  • RCE
  • Threat Intelligence
  • Cybersecurity
  • Digital Keys
  • Bluetooth Security
  • ISO/SAE 21434
  • UNECE R155
  • Regulations
  • Data Privacy
  • EVs
  • Autonomous Driving
  • Pwn2Own Automotive

© 2026 Carthreat.com. All right reserved.  Privacy Policy | Legal

Welcome Back!

Sign in to your account

Username or Email Address
Password

Lost your password?