CarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Notification
  • Autonomous Driving
  • Automotive Ethernet
  • BMS
  • ECU
  • EV
  • ISO/SAE 21434
  • Infotainment
  • OTA Updates
  • OBD-II
  • Pwn2Own
  • RCE
  • SDVs
  • TCU
  • UNECE R155
India's two-part cyber rulebook now has a certification trail
Cybersecurity

India’s two-part cyber rulebook now has a certification trail

Colmobil shuts some counters after intruders reach its network
Cybersecurity

Colmobil shuts some counters after intruders reach its network

A supplier flaw handed car buyers' payment records to criminals
Cybersecurity

A supplier flaw handed car buyers’ payment records to criminals

Physical Security

Rental cars stored video of Norwegian troops and gate codes

Font ResizerAa
CarThreatCarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
Search
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Sign In Sign In
Follow US
© 2026 Carthreat.com. All right reserved.
Research & Innovation

Cheap AI binary analysis forces a rethink of car firmware defenses

A VicOne analysis argues that as AI drives down the cost of reading binaries, firmware protection can no longer rest on signing alone.

CarThreat Staff
Last updated: September 28, 2026 1:25 pm
By
ctadmin
2 Min Read
SHARE

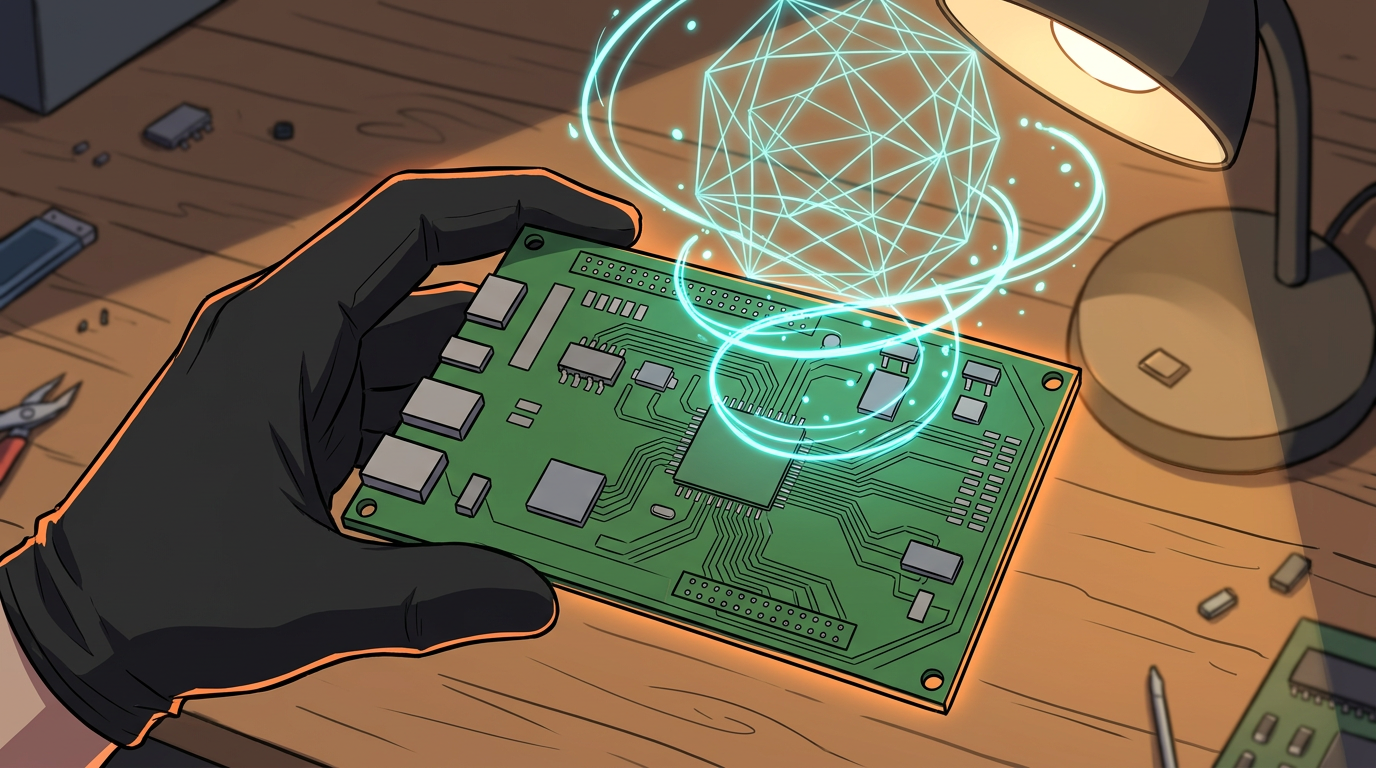
Automotive firmware protection built around code signing alone is no longer enough, argues a two-part VicOne analysis published this week. The reason is economic: AI is collapsing the cost of reading binaries.

Author Seigo Yamamoto cites Anthropic's Claude Mythos Preview reconstructing plausible source code from a stripped binary, cross-referencing that reconstruction against the original, and surfacing a flaw that could have granted administrator privileges on a smartphone. OpenAI's GPT-5.4-Cyber, he notes, was given the ability to analyze compiled software without source access.

Reverse engineering a stripped image used to demand scarce expertise and long hours. That entry price is falling. Attackers consequently gain little from first compromising a build or distribution server. Images pulled off a maintenance laptop, a diagnostic port, a reflash tool or a debug interface supply the same starting material.

Yamamoto's remedy is architectural. Secure boot with anti-rollback enforcement, encryption, key management and runtime protection should be engineered together, he writes, not bolted on one layer at a time. Plaintext updates, a key reused across several product lines, or firmware a service tool can lift without resistance each widen the opening.

Coverage is the second gap he identifies. New ECUs and OTA-capable hardware are the easy cases. End-of-life parts and supplier-supplied images belong in the same threat model, since a weakness proven against an old asset can resurface in a new vehicle line. Sitting outside UN Regulation No. 155 type approval buys no exemption.

Last comes monitoring. Rather than treating a leak as an incident to investigate afterwards, Yamamoto wants defenders to assume one has happened. Watching for full images alone is insufficient, he argues, because update packages, manifests, diff patches, service manuals, debug scripts, flashing tools and symbol files each reveal structure worth inferring from.
Join Our Newsletter
Subscribe to our newsletter to get our newest articles instantly!
TAGGED:ECU SecurityFirmware SecuritySoftware-Defined Vehicles (SDVs)Threat IntelligenceVehicle SoftwareVulnerabilities
SOURCES:VicOne
Share This Article
Facebook Email Copy Link

Follow US

Find US on Social Medias
FacebookLike
XFollow
YoutubeSubscribe

You Might Also Like

Policy & Compliance

China freezes vehicle software to end patch-later OTA era

By
ctadmin
August 27, 2026
Cybersecurity

VicOne hooks fresh CVE feeds into vehicle risk models

By
ctadmin
September 24, 2026
Cybersecurity

Toyota defends its connected car data as Australian regulators dig in

By
ctadmin
October 11, 2026
Anime illustration of a relay attack bridging a key fob signal from a house to a car in a driveway
Cybersecurity

Half of keyless cars still relay-open after a decade of ADAC testing

By
ctadmin
September 3, 2026
AI Race

Engineers gave a chatbot control of a rented Corolla

By
ctadmin
October 2, 2026
Anime illustration of a rental counter ID scanner leaking license data into a dark void
Cybersecurity

Rental car ID scans linked to 153 million license trove

By
ctadmin
September 3, 2026

CarThreat

Intelligence for the EV and automotive security market
  • News
  • Features
  • Spotlight
  • Events
  • About Carthreat
  • Our Mission
  • Services
  • Contact Us
  • OBD-II
  • Automotive Ethernet
  • TCU
  • Infotainment Systems
  • SDVs
  • BMS
  • ECU Security
  • CAN Bus
  • Threat Intelligence
  • Cybersecurity
  • Digital Keys
  • Bluetooth Security
  • OTA Updates
  • Vulnerabilities
  • Relay Attacks
  • RCE
  • Data Privacy
  • EVs
  • Autonomous Driving
  • Pwn2Own Automotive
  • ISO/SAE 21434
  • UNECE R155
  • Regulations

© 2026 Carthreat.com. All right reserved.  Privacy Policy | Legal

Welcome Back!

Sign in to your account

Username or Email Address
Password

Lost your password?