CarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Notification
  • Autonomous Driving
  • Automotive Ethernet
  • BMS
  • ECU
  • EV
  • ISO/SAE 21434
  • Infotainment
  • OTA Updates
  • OBD-II
  • Pwn2Own
  • RCE
  • SDVs
  • TCU
  • UNECE R155
India's two-part cyber rulebook now has a certification trail
Cybersecurity

India’s two-part cyber rulebook now has a certification trail

Colmobil shuts some counters after intruders reach its network
Cybersecurity

Colmobil shuts some counters after intruders reach its network

A supplier flaw handed car buyers' payment records to criminals
Cybersecurity

A supplier flaw handed car buyers’ payment records to criminals

Physical Security

Rental cars stored video of Norwegian troops and gate codes

Font ResizerAa
CarThreatCarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
Search
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Sign In Sign In
Follow US
© 2026 Carthreat.com. All right reserved.
Cybersecurity

Botslab dash cams ship with 13 flaws and no fix in sight

CISA flagged thirteen unpatched vulnerabilities in Botslab's G980H dash camera after the vendor stopped answering the agency's requests for help.

CarThreat Staff
Last updated: September 26, 2026 2:07 am
By
ctadmin
2 Min Read
SHARE

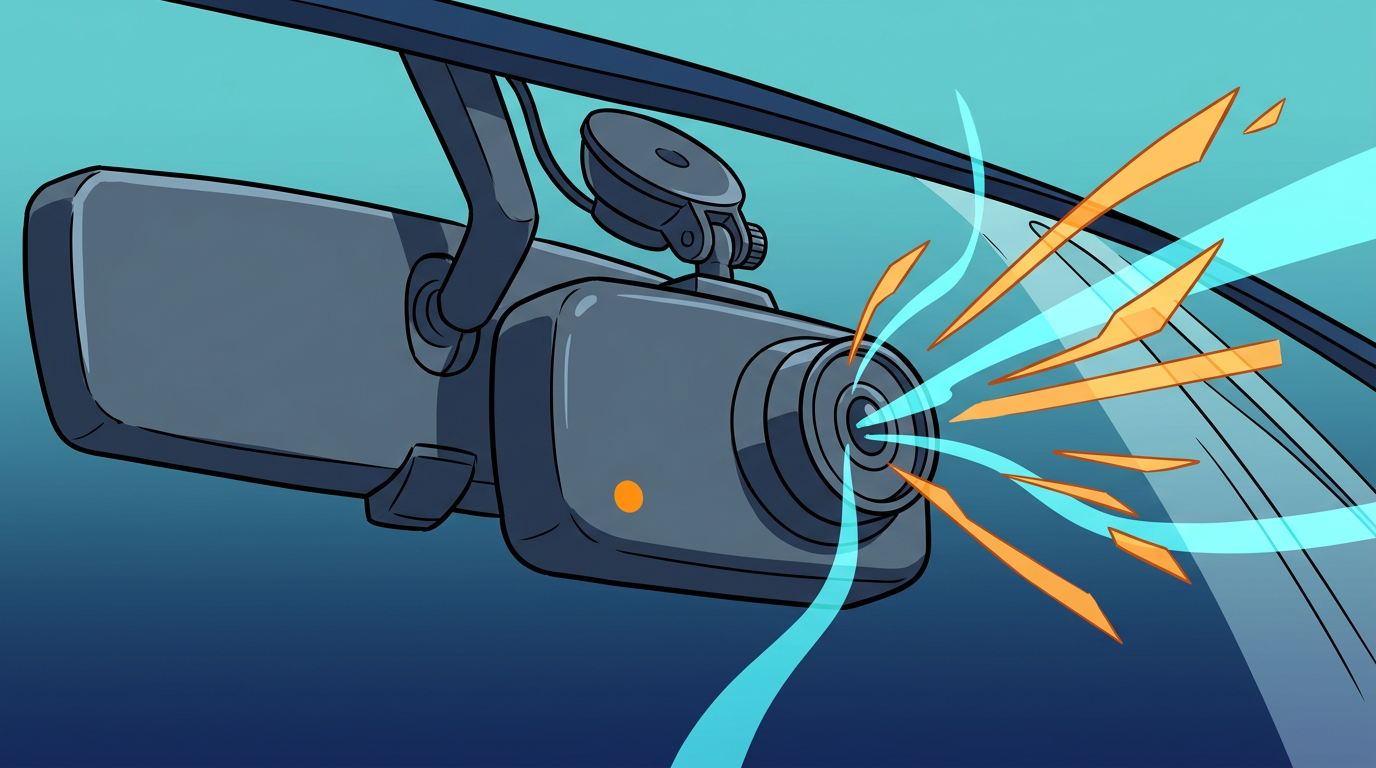
Thirteen vulnerabilities sit unpatched in Botslab’s G980H dash camera, and the vendor has not answered CISA’s requests to help close them. CISA published advisory ICSA-26-267-01 on September 24 and rated the cluster 8.8 under CVSS v3, filing the device under the transportation sector.

Session handling carries the worst of the set. CVE-2026-84399 lets one client reuse another connection’s authenticated session, so privileged commands run without checking who is asking. CVE-2026-82566 keeps that state alive after a connection dies, and CVE-2026-85496 builds session identifiers from a small sequential pool that an attacker on the same network can walk through.

Two more need no guesswork. CVE-2026-77967 accepts a captured authentication value a second time, from a different client. CVE-2026-88761 derives the default WiFi password from device details the camera itself broadcasts, leaving few characters to brute force.

Physical access is worse. Firmware 58_QHG980HMCN5291SysFW+ exposes a root account over UART with no password at all (CVE-2026-88956), and that interface prints the WiFi password during startup. Support logs left on removable storage carry stored credentials for anyone who pulls the card (CVE-2026-82716).

The rest cover hard-coded cryptographic keys, a path traversal, out-of-bounds writes, cleartext transmission and weak credentials. Affected units run firmware 30010_QHG980HN5294SysFW+ or 58_QHG980HMCN5291SysFW+. The advisory’s only mitigation is for owners to contact the vendor directly. A dash camera sits inside the cabin on the same wiring, and often the same network, as the head unit, which turns a camera that hands out root access into a vehicle problem rather than a gadget one.
Join Our Newsletter
Subscribe to our newsletter to get our newest articles instantly!
TAGGED:Automotive EthernetConnected VehiclesCybersecurityFirmware SecurityThreat IntelligenceVulnerabilities
SOURCES:CISA ICS Advisory ICSA-26-267-01
Share This Article
Facebook Email Copy Link

Follow US

Find US on Social Medias
FacebookLike
XFollow
YoutubeSubscribe

You Might Also Like

Cybersecurity

Automotive IQ names its top 20 cybersecurity leaders for 2026

By
ctadmin
July 12, 2026
Cybersecurity

Car companion apps hand driver details to advertisers, study finds

By
ctadmin
October 15, 2026
Cybersecurity

Flock offers staff buyouts as cities drop plate readers

By
ctadmin
September 22, 2026
Policy & Compliance

R155 and R156 turn car cyber compliance into a renewal cycle

By
ctadmin
September 24, 2026
Cel-shaded illustration of stalled robotic assembly arms above a car body with a cyan data loop feeding a glowing storage cube
Cybersecurity

Car industry recovery plans buckle within a single day

By
ctadmin
September 10, 2026
CybersecurityEV & Infrastructure

EV Energy charging platform flaws allow full grid hijack with no patch

By
ctadmin
July 18, 2026

CarThreat

Intelligence for the EV and automotive security market
  • News
  • Features
  • Spotlight
  • Events
  • About Carthreat
  • Our Mission
  • Services
  • Contact Us
  • OBD-II
  • Automotive Ethernet
  • TCU
  • Infotainment Systems
  • SDVs
  • BMS
  • ECU Security
  • CAN Bus
  • Threat Intelligence
  • Cybersecurity
  • Digital Keys
  • Bluetooth Security
  • OTA Updates
  • Vulnerabilities
  • Relay Attacks
  • RCE
  • Data Privacy
  • EVs
  • Autonomous Driving
  • Pwn2Own Automotive
  • ISO/SAE 21434
  • UNECE R155
  • Regulations

© 2026 Carthreat.com. All right reserved.  Privacy Policy | Legal

Welcome Back!

Sign in to your account

Username or Email Address
Password

Lost your password?