CarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Notification
  • Autonomous Driving
  • Automotive Ethernet
  • BMS
  • ECU
  • EV
  • ISO/SAE 21434
  • Infotainment
  • OTA Updates
  • OBD-II
  • Pwn2Own
  • RCE
  • SDVs
  • TCU
  • UNECE R155
Cybersecurity

Boston police tested Motorola and Axon readers as Flock exited

Cybersecurity

Leapmotor EVs carry cameras from a supplier Australia banned

Policy & Compliance

BYD rewrites Australian privacy policy after Four Corners questions

Cybersecurity

A passwordless port let a researcher command a moving BYD ute

Font ResizerAa
CarThreatCarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
Search
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Sign In Sign In
Follow US
© 2026 Carthreat.com. All right reserved.
Cybersecurity

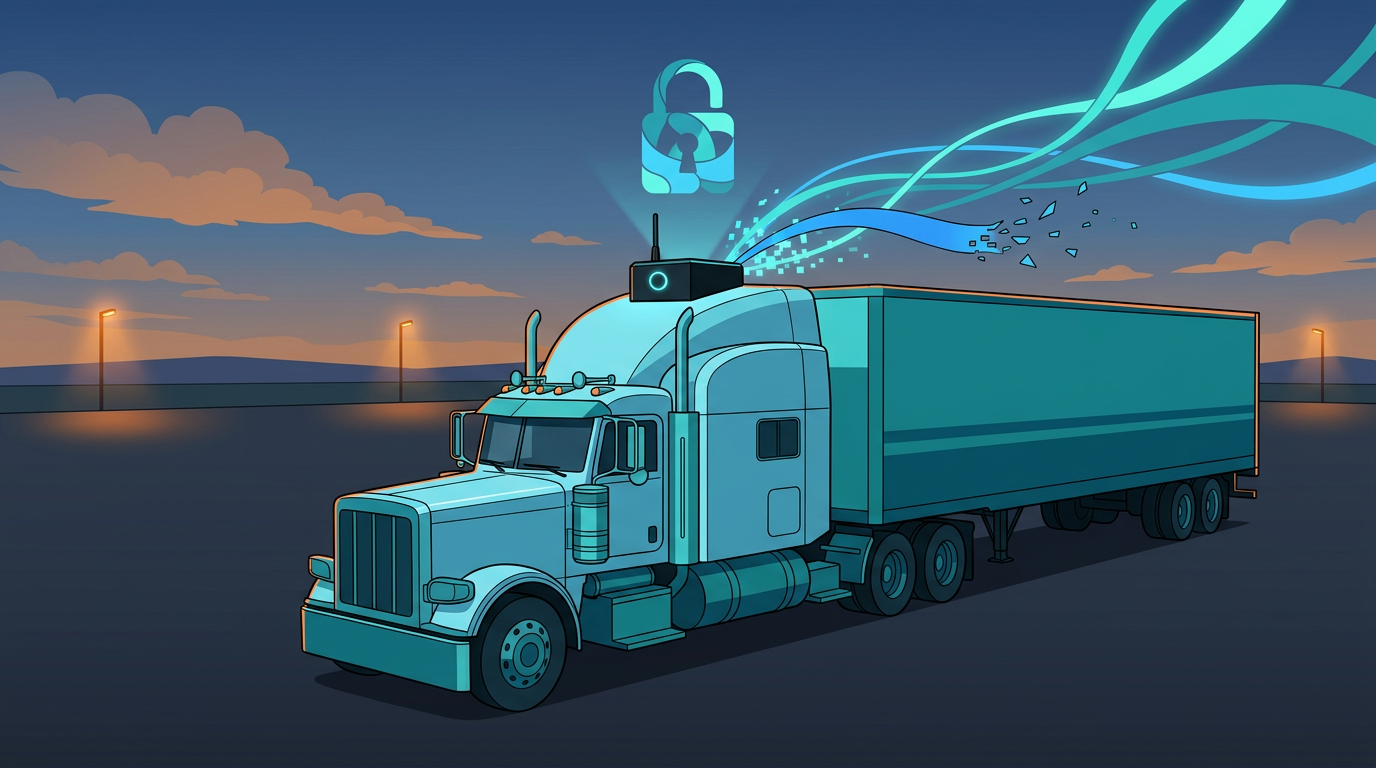
Hardcoded keys in a truck logging app expose fleet telemetry

A CISA advisory says hardcoded broker and FTP credentials in Bransys logging software let unauthenticated attackers read live telemetry from commercial fleets.

CarThreat Staff
Last updated: September 18, 2026 1:19 am
By
ctadmin
2 Min Read
SHARE

Bransys, a maker of electronic logging devices for commercial truck fleets, shipped its companion app with credentials baked into the binary. A CISA advisory published September 17 describes three flaws that let anyone reaching the company’s brokers read live telemetry from every active unit.

The worst is CVE-2026-86520, an 8.7 under CVSS 4.0. Hardcoded MQTT credentials grant read access to real-time data across a subset of carriers tied to the affected broker. CVE-2026-86689 covers cleartext transmission, which CISA says lets an attacker connect and pull everything flowing through. A third bug, CVE-2026-77960, leaves hardcoded FTP credentials in place, opening a second server to unauthenticated reads.

All three trace to basic hygiene failures, CWE-798 for embedded credentials and CWE-319 for the plaintext channel. CISA lists the sector as Transportation Systems, deployed in the United States.

The exposure is narrow. No code execution, no truck control, no path to the engine. What an attacker gets is location and status data for commercial vehicles, the kind regulators treat as sensitive because it reveals routes, schedules and driver behavior.

Bransys fixed the flaws through app store releases. Android needs version 11.00.00 or newer, iOS 1.1.54. Older installs stay vulnerable until a driver updates, so fleets that manage devices centrally should push the fix rather than wait.
Join Our Newsletter
Subscribe to our newsletter to get our newest articles instantly!
TAGGED:Connected VehiclesData PrivacyFirmware SecurityTelematics Control Units (TCU)Threat IntelligenceVulnerabilities
SOURCES:CISA ICS Advisory ICSA-26-260-01
Share This Article
Facebook Email Copy Link

Follow US

Find US on Social Medias
FacebookLike
XFollow
YoutubeSubscribe

You Might Also Like

Cybersecurity

GM widens in-car recording while promising footage stays local

By
ctadmin
September 12, 2026
Cybersecurity

Charger scan finds 720 of 1,000 exposed endpoints skip encryption

By
ctadmin
September 3, 2026
Anime illustration of a rental counter ID scanner leaking license data into a dark void
Cybersecurity

Rental car ID scans linked to 153 million license trove

By
ctadmin
September 3, 2026
Cybersecurity

May Mobility Challenges AV Scaling Norms with Predictive World Model Architecture

By
ctadmin
May 26, 2026
Cybersecurity

Valeo and Zuken Launch Joint AI Platform to Speed Up Automotive Electronics Design

By
ctadmin
May 30, 2026
Cybersecurity

Stealthy camera delay attack fools self-driving object detection

By
ctadmin
August 12, 2026

CarThreat

Intelligence for the EV and automotive security market
  • News
  • Features
  • Spotlight
  • Events
  • About Carthreat
  • Our Mission
  • Services
  • Contact Us
  • OBD-II
  • Automotive Ethernet
  • TCU
  • Infotainment Systems
  • SDVs
  • BMS
  • ECU Security
  • CAN Bus
  • Threat Intelligence
  • Cybersecurity
  • Digital Keys
  • Bluetooth Security
  • OTA Updates
  • Vulnerabilities
  • Relay Attacks
  • RCE
  • Data Privacy
  • EVs
  • Autonomous Driving
  • Pwn2Own Automotive
  • ISO/SAE 21434
  • UNECE R155
  • Regulations

© 2026 Carthreat.com. All right reserved.  Privacy Policy | Legal

Welcome Back!

Sign in to your account

Username or Email Address
Password

Lost your password?