CarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Notification
  • Autonomous Driving
  • Automotive Ethernet
  • BMS
  • ECU
  • EV
  • ISO/SAE 21434
  • Infotainment
  • OTA Updates
  • OBD-II
  • Pwn2Own
  • RCE
  • SDVs
  • TCU
  • UNECE R155
India's two-part cyber rulebook now has a certification trail
Cybersecurity

India’s two-part cyber rulebook now has a certification trail

Colmobil shuts some counters after intruders reach its network
Cybersecurity

Colmobil shuts some counters after intruders reach its network

A supplier flaw handed car buyers' payment records to criminals
Cybersecurity

A supplier flaw handed car buyers’ payment records to criminals

Physical Security

Rental cars stored video of Norwegian troops and gate codes

Font ResizerAa
CarThreatCarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
Search
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Sign In Sign In
Follow US
© 2026 Carthreat.com. All right reserved.
Electric Vehicles

Fake plug-and-charge stations bill EV owners for stranger fills

A rogue charging unit can relay a victim's plug-and-charge credentials and bill their account for a stranger's session.

CarThreat Staff
Last updated: August 9, 2026 10:43 pm
By
ctadmin
2 Min Read
Fake plug-and-charge stations bill EV owners for stranger fills
SHARE

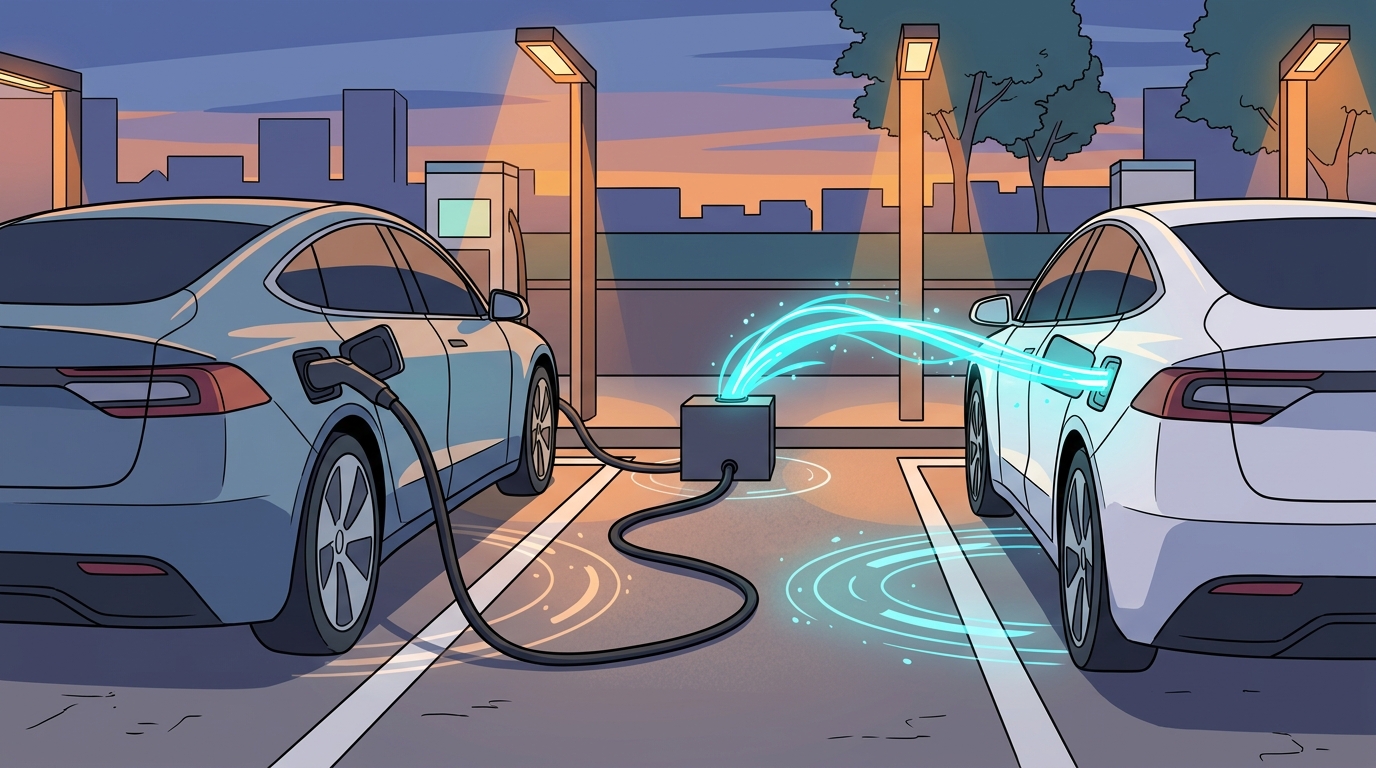
A new relay trick against the plug-and-charge payment system used in European DC fast charging could let a thief fill their battery while another driver’s account takes the hit. Researchers at Technische Hochschule Ingolstadt demonstrated the exploit chain at VehicleSec ’26 in Baltimore this week, with a proof of concept they built from scratch.

The scheme turns a fake charging unit into a man in the middle. When a victim plugs in, the rogue station captures the vehicle’s cryptographic identity during the authentication handshake and relays it onward to a real charger, which completes the session against the victim’s contract certificate. The driver of the vehicle never sees an authorization prompt.

The weakness sits in two places. The plug-and-charge signature carries no station-identifying information, so the billing system cannot tell which unit actually delivered the power. On top of that, the researchers found gaps in how the standard handles TLS certificates on the charging side.

The team, made up of Jakob Low, Vishwa Vasu, Thomas Hutzelmann, and Hans-Joachim Hof, argues the flaw will become more dangerous as plug-and-charge rolls out beyond Europe. Their suggested fixes include binding station identity into the payment signature and making certificate validation stricter on the vehicle side.

For owners the immediate risk is paying for somebody else’s session. For the industry, the work adds to a growing list of ISO 15118 findings and points to a standard that still treats the station as a trusted endpoint.
Join Our Newsletter
Subscribe to our newsletter to get our newest articles instantly!
TAGGED:Charging InfrastructureConnected VehiclesElectric Vehicles (EVs)ISO 15118Relay AttacksVulnerabilities
SOURCES:USENIX VehicleSec '26
Share This Article
Facebook Email Copy Link

Follow US

Find US on Social Medias
FacebookLike
XFollow
YoutubeSubscribe

You Might Also Like

Anime illustration of a fleet van whose rooftop telematics signal breaks apart
Cybersecurity

Fleet tracker Cartrack draws a South African privacy probe after August ransomware

By
ctadmin
September 19, 2026
Policy & Compliance

Missouri’s governor orders a 30-day limit on plate reader data

By
ctadmin
September 17, 2026
Electric Vehicles

How to Get High Quality, Affordable, Hassle-free Auto Repair

By
ctadmin
August 30, 2021
Policy & Compliance

Quebec report declares car data consent fundamentally broken

By
ctadmin
August 23, 2026
Policy & Compliance

India’s AIS-156 update makes wireless BMS hacking tests compulsory

By
ctadmin
September 9, 2026
Cybersecurity

Car networking tool spills stack memory onto CAN from one packet

By
ctadmin
August 19, 2026

CarThreat

Intelligence for the EV and automotive security market
  • News
  • Features
  • Spotlight
  • Events
  • About Carthreat
  • Our Mission
  • Services
  • Contact Us
  • OBD-II
  • Automotive Ethernet
  • TCU
  • Infotainment Systems
  • SDVs
  • BMS
  • ECU Security
  • CAN Bus
  • OTA Updates
  • Vulnerabilities
  • Relay Attacks
  • RCE
  • Threat Intelligence
  • Cybersecurity
  • Digital Keys
  • Bluetooth Security
  • ISO/SAE 21434
  • UNECE R155
  • Regulations
  • Data Privacy
  • EVs
  • Autonomous Driving
  • Pwn2Own Automotive

© 2026 Carthreat.com. All right reserved.  Privacy Policy | Legal

Welcome Back!

Sign in to your account

Username or Email Address
Password

Lost your password?