CarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Notification
  • Autonomous Driving
  • Automotive Ethernet
  • BMS
  • ECU
  • EV
  • ISO/SAE 21434
  • Infotainment
  • OTA Updates
  • OBD-II
  • Pwn2Own
  • RCE
  • SDVs
  • TCU
  • UNECE R155
India's two-part cyber rulebook now has a certification trail
Cybersecurity

India’s two-part cyber rulebook now has a certification trail

Colmobil shuts some counters after intruders reach its network
Cybersecurity

Colmobil shuts some counters after intruders reach its network

A supplier flaw handed car buyers' payment records to criminals
Cybersecurity

A supplier flaw handed car buyers’ payment records to criminals

Physical Security

Rental cars stored video of Norwegian troops and gate codes

Font ResizerAa
CarThreatCarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
Search
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Sign In Sign In
Follow US
© 2026 Carthreat.com. All right reserved.
Cybersecurity

Car networking tool spills stack memory onto CAN from one packet

Two remote bugs in an open-source AVTP tool can dump 18KB of stack memory onto a vehicle's CAN bus with a single UDP datagram.

CarThreat Staff
Last updated: August 19, 2026 11:17 pm
By
ctadmin
2 Min Read
SHARE

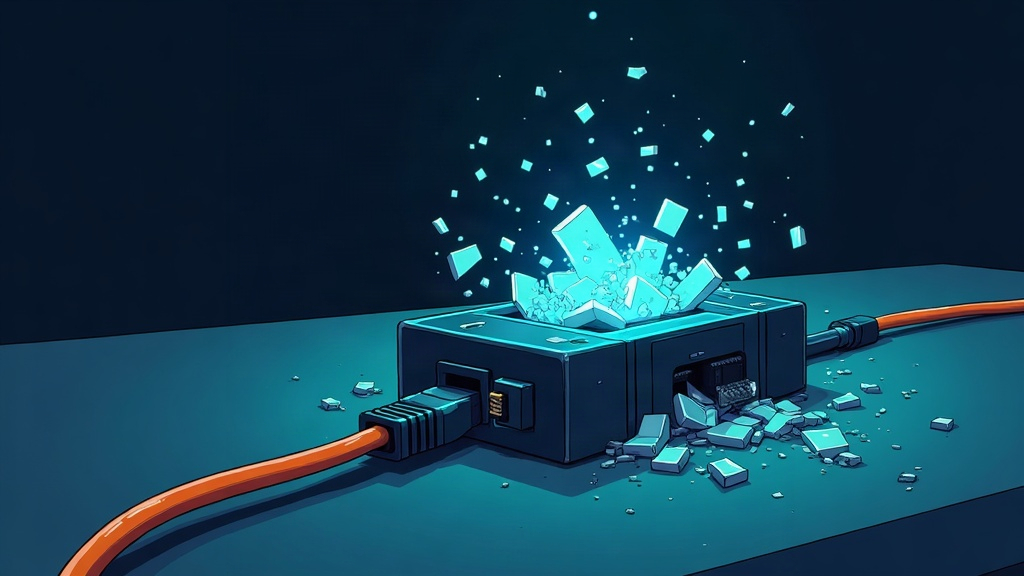
An open-source tool that moves audio, video and CAN traffic across automotive Ethernet can be forced to spill its own stack memory onto the car’s CAN bus with a single network packet. Researcher Fatullayev Asadbek disclosed the flaws through VulnCheck this week, and both sit in the ACF CAN listener of COVESA Open1722, reachable by unauthenticated remote attackers.

Attackers trigger CVE-2026-73522 with a UDP datagram that packs more than 15 ACF-CAN messages. avtp_to_can() advances a write index against a fixed 15-slot stack array without ever bounding it, so each extra message lands beyond the buffer’s end. Stream IDs ride in plaintext and no authentication is required, meaning any device on the network segment can fire the datagram. The result is corruption of adjacent stack memory, a path to arbitrary code execution or a denial-of-service crash.

The second flaw, CVE-2026-73523, is an integer truncation rated CVSS 8.7. The num_can_msgs variable is declared as uint8_t, which turns the -1 error return from avtp_to_can() into 255. The write loop then runs 255 times against the 15-slot array, leaking roughly 18KB of adjacent stack memory as about 240 CAN frames that any recipient on the bus can read.

Open1722 is the Connected Vehicle Systems Alliance’s open-source implementation of the IEEE 1722 (AVTP) standard, used to stream audio and video and tunnel CAN and LIN messages in vehicle development and test rigs. Both bugs affect versions through 0.9.2, the current release, and no patched build was available at disclosure time. The report was filed as GitHub issue 154, with a second advisory covering the overflow variant. For teams running Open1722 in gateways or validation benches, the memory disclosure puts a component’s internal state on the CAN bus for any other ECU to read.
Join Our Newsletter
Subscribe to our newsletter to get our newest articles instantly!
TAGGED:Automotive EthernetCAN BusConnected VehiclesCybersecurityFirmware SecurityRemote Code Execution (RCE)Vulnerabilities
SOURCES:VulnCheckVulnCheckCOVESA Open1722 on GitHub
Share This Article
Facebook Email Copy Link

Follow US

Find US on Social Medias
FacebookLike
XFollow
YoutubeSubscribe

You Might Also Like

Cybersecurity

Uber Invests $500M in Nuro Robotaxi Deal with Lucid Vehicles

By
ctadmin
June 12, 2026
Policy & Compliance

Texas halts highway permits for new plate reader cameras

By
ctadmin
September 20, 2026
AI Race

AI tool chains low-severity bugs into critical automotive attack paths

By
ctadmin
July 27, 2026
Cybersecurity

Truck recall firmware hid fixes for unlisted security flaws

By
ctadmin
August 6, 2026
Car NewsCybersecurity

Keyless car theft surges across North America as cyber techniques evolve

By
ctadmin
July 18, 2026
Policy & Compliance

Senator widens AI camera inquiry to Axon, Verkada and Motorola Solutions

By
ctadmin
September 5, 2026

CarThreat

Intelligence for the EV and automotive security market
  • News
  • Features
  • Spotlight
  • Events
  • About Carthreat
  • Our Mission
  • Services
  • Contact Us
  • OBD-II
  • Automotive Ethernet
  • TCU
  • Infotainment Systems
  • SDVs
  • BMS
  • ECU Security
  • CAN Bus
  • OTA Updates
  • Vulnerabilities
  • Relay Attacks
  • RCE
  • Threat Intelligence
  • Cybersecurity
  • Digital Keys
  • Bluetooth Security
  • ISO/SAE 21434
  • UNECE R155
  • Regulations
  • Data Privacy
  • EVs
  • Autonomous Driving
  • Pwn2Own Automotive

© 2026 Carthreat.com. All right reserved.  Privacy Policy | Legal

Welcome Back!

Sign in to your account

Username or Email Address
Password

Lost your password?