CarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Notification
  • Autonomous Driving
  • Automotive Ethernet
  • BMS
  • ECU
  • EV
  • ISO/SAE 21434
  • Infotainment
  • OTA Updates
  • OBD-II
  • Pwn2Own
  • RCE
  • SDVs
  • TCU
  • UNECE R155
India's two-part cyber rulebook now has a certification trail
Cybersecurity

India’s two-part cyber rulebook now has a certification trail

Colmobil shuts some counters after intruders reach its network
Cybersecurity

Colmobil shuts some counters after intruders reach its network

A supplier flaw handed car buyers' payment records to criminals
Cybersecurity

A supplier flaw handed car buyers’ payment records to criminals

Physical Security

Rental cars stored video of Norwegian troops and gate codes

Font ResizerAa
CarThreatCarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
Search
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Sign In Sign In
Follow US
© 2026 Carthreat.com. All right reserved.
Cybersecurity

Qualcomm critical Wi-Fi flaw reaches car cockpit chips

Qualcomm's August bulletin patches a critical WLAN firmware overflow that reaches Snapdragon automotive cockpit and connectivity chips.

CarThreat Staff
Last updated: August 7, 2026 3:28 pm
By
ctadmin
2 Min Read
SHARE

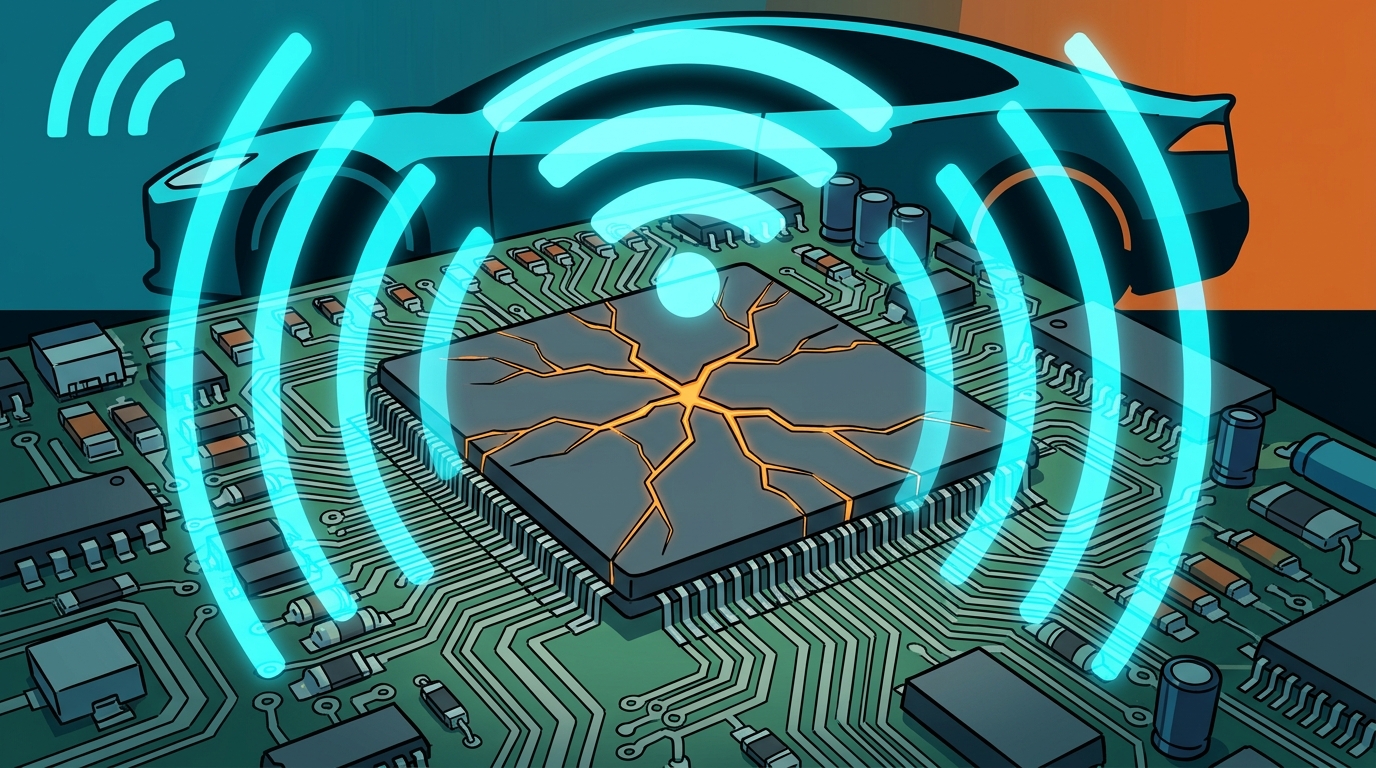
Qualcomm’s August 2026 security bulletin patches a critical flaw in WLAN firmware that affects a broad range of its chips, including automotive-grade parts used in connected vehicles.

The most severe issue, CVE-2026-25289, is a stack-based buffer overflow rated 9.6 on the CVSS scale. The bug is triggered by malformed Device Capability Extended attributes in certain NAN Service Discovery Frames, causing memory corruption. The attack vector is adjacent, meaning an attacker within Wi-Fi range can exploit it remotely without credentials or user interaction, with full impact on confidentiality, integrity, and availability.

The automotive chips in the affected list include the QCA6696 automotive Wi-Fi 6 solution, the SA8255P and SA8770P cockpit platform families, and other auto-grade parts such as the SA7255P, SA7775P, SA8620P, and SA9000P.

Two related fixes matter for cars too. CVE-2026-24083 is a high-severity untrusted pointer dereference in an automotive security driver, triggered by IOCTL requests with invalid arguments, and affects the SA8295P, QAM8295P, and QCA6696 — including the flagship Snapdragon Cockpit Gen 3 platform built on SA8295P. CVE-2026-21366 is a high-severity integer overflow in the data network stack with the same automotive chipset footprint.

Qualcomm says patches are being actively shared with OEMs, who are responsible for deploying fixes to released vehicles. For drivers, that means the timeline depends on automaker update programs, underscoring why over-the-air update capability is becoming a security feature in itself.
Join Our Newsletter
Subscribe to our newsletter to get our newest articles instantly!
TAGGED:Connected VehiclesCybersecurityFirmware SecurityOTA UpdatesVehicle SoftwareVulnerabilities
SOURCES:Qualcomm
Share This Article
Facebook Email Copy Link

Follow US

Find US on Social Medias
FacebookLike
XFollow
YoutubeSubscribe

You Might Also Like

Cybersecurity

EV charger worm escapes a Tesla wall plug and hops to rival brands

By
ctadmin
August 22, 2026
Cybersecurity

Analog fingerprints catch counterfeit ECUs that pass crypto checks

By
ctadmin
August 12, 2026
Cybersecurity

4D LiDAR Traffic Platform Chosen for Snowy City Intersections to Improve Road Safety

By
ctadmin
June 12, 2026
Policy & Compliance

R155 and R156 turn car cyber compliance into a renewal cycle

By
ctadmin
September 24, 2026
Cybersecurity

Report warns supplier hacks could cost automakers $100M

By
ctadmin
August 14, 2026
Cybersecurity

Chinese lidar faces federal review as lawmakers push bans

By
ctadmin
August 23, 2026

CarThreat

Intelligence for the EV and automotive security market
  • News
  • Features
  • Spotlight
  • Events
  • About Carthreat
  • Our Mission
  • Services
  • Contact Us
  • OBD-II
  • Automotive Ethernet
  • TCU
  • Infotainment Systems
  • SDVs
  • BMS
  • ECU Security
  • CAN Bus
  • OTA Updates
  • Vulnerabilities
  • Relay Attacks
  • RCE
  • Threat Intelligence
  • Cybersecurity
  • Digital Keys
  • Bluetooth Security
  • ISO/SAE 21434
  • UNECE R155
  • Regulations
  • Data Privacy
  • EVs
  • Autonomous Driving
  • Pwn2Own Automotive

© 2026 Carthreat.com. All right reserved.  Privacy Policy | Legal

Welcome Back!

Sign in to your account

Username or Email Address
Password

Lost your password?