CarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Notification
  • Autonomous Driving
  • Automotive Ethernet
  • BMS
  • ECU
  • EV
  • ISO/SAE 21434
  • Infotainment
  • OTA Updates
  • OBD-II
  • Pwn2Own
  • RCE
  • SDVs
  • TCU
  • UNECE R155
India's two-part cyber rulebook now has a certification trail
Cybersecurity

India’s two-part cyber rulebook now has a certification trail

Colmobil shuts some counters after intruders reach its network
Cybersecurity

Colmobil shuts some counters after intruders reach its network

A supplier flaw handed car buyers' payment records to criminals
Cybersecurity

A supplier flaw handed car buyers’ payment records to criminals

Physical Security

Rental cars stored video of Norwegian troops and gate codes

Font ResizerAa
CarThreatCarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
Search
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Sign In Sign In
Follow US
© 2026 Carthreat.com. All right reserved.
Car NewsCybersecurity

Tesla keyless theft vulnerability exposes CAN injection risks across EV fleets

PlaxidityX demonstrates CAN injection attack on Tesla Model 3 through OBD-II port.

CarThreat Staff
Last updated: July 18, 2026 7:19 am
By
ctadmin
2 Min Read
SHARE

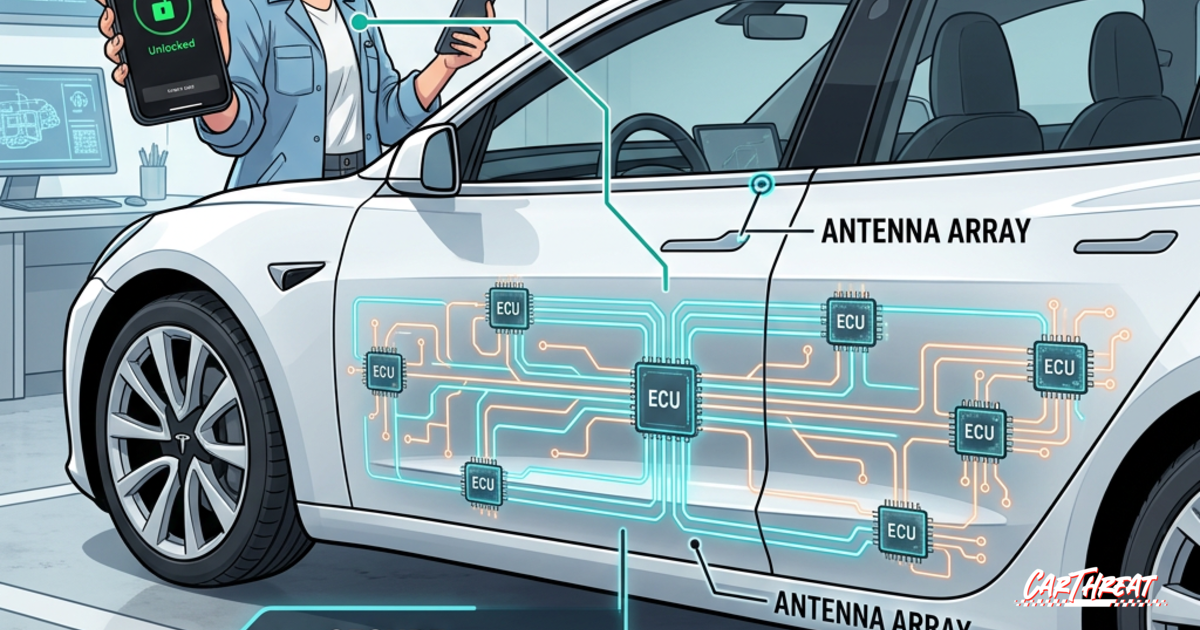
PlaxidityX Threat Labs has detailed a vulnerability in the Tesla Model 3 and Model Y that enabled keyless car theft via CAN injection attacks. Tracked as CVE-2025-6785, the flaw allowed attackers to inject malicious CAN messages into the vehicle network without key-based authentication or physical interior access.

Researchers connected a homemade device to the OBD-II port behind the rear seat and sent commands over the CAN bus to shift the car into drive and start the engine. The attack exploited the fact that in modern keyless entry systems, virtually all authentication occurs over the network, with no physical key mechanism required to start the vehicle.

UK data shows that 58% of vehicle thefts between April 2023 and March 2024 involved keyless techniques. The Tesla case study demonstrates that even industry-leading vehicles with advanced software security remain vulnerable to CAN bus injection attacks.

Tesla independently discovered the issue before disclosure and released firmware version 2023.44, which renders this specific theft method ineffective. However, the research highlights a broader industry challenge as keyless car theft continues to surge across North America and Europe.

PlaxidityX recommends OEMs adopt proactive, real-time anti-theft solutions that monitor CAN bus traffic for unauthorized injection patterns, rather than relying solely on factory-installed immobilizers and encryption.
Join Our Newsletter
Subscribe to our newsletter to get our newest articles instantly!
TAGGED:Automotive SecurityCAN Bus AttackKeyless EntryTeslaVehicle Theft
SOURCES:PlaxidityX
Share This Article
Facebook Email Copy Link

Follow US

Find US on Social Medias
FacebookLike
XFollow
YoutubeSubscribe

You Might Also Like

Cybersecurity

Truck recall firmware hid fixes for unlisted security flaws

By
ctadmin
August 6, 2026
Cybersecurity

Plate data misuse costs a San Jose officer his badge

By
ctadmin
September 14, 2026
Cybersecurity

EU Mandate for Driver Monitoring Raises Biometric Privacy in Connected Cars

By
ctadmin
July 12, 2026
Cybersecurity

Sydney court hears Tesla app gave an abuser remote car control

By
ctadmin
September 9, 2026
CybersecurityPolicy & Compliance

Canada opens its EV market while the privacy rules stay unwritten

By
ctadmin
October 11, 2026
Cybersecurity

US Bans Polestar EV Sales Under National Security Connected Vehicle Rule

By
ctadmin
July 1, 2026

CarThreat

Intelligence for the EV and automotive security market
  • News
  • Features
  • Spotlight
  • Events
  • About Carthreat
  • Our Mission
  • Services
  • Contact Us
  • OBD-II
  • Automotive Ethernet
  • TCU
  • Infotainment Systems
  • SDVs
  • BMS
  • ECU Security
  • CAN Bus
  • OTA Updates
  • Vulnerabilities
  • Relay Attacks
  • RCE
  • Threat Intelligence
  • Cybersecurity
  • Digital Keys
  • Bluetooth Security
  • ISO/SAE 21434
  • UNECE R155
  • Regulations
  • Data Privacy
  • EVs
  • Autonomous Driving
  • Pwn2Own Automotive

© 2026 Carthreat.com. All right reserved.  Privacy Policy | Legal

Welcome Back!

Sign in to your account

Username or Email Address
Password

Lost your password?