CAN XL carries every known weakness of the classic CAN protocol and adds seven more of its own, according to a Georgia Tech security review of the standard meant to wire tomorrow’s vehicles.
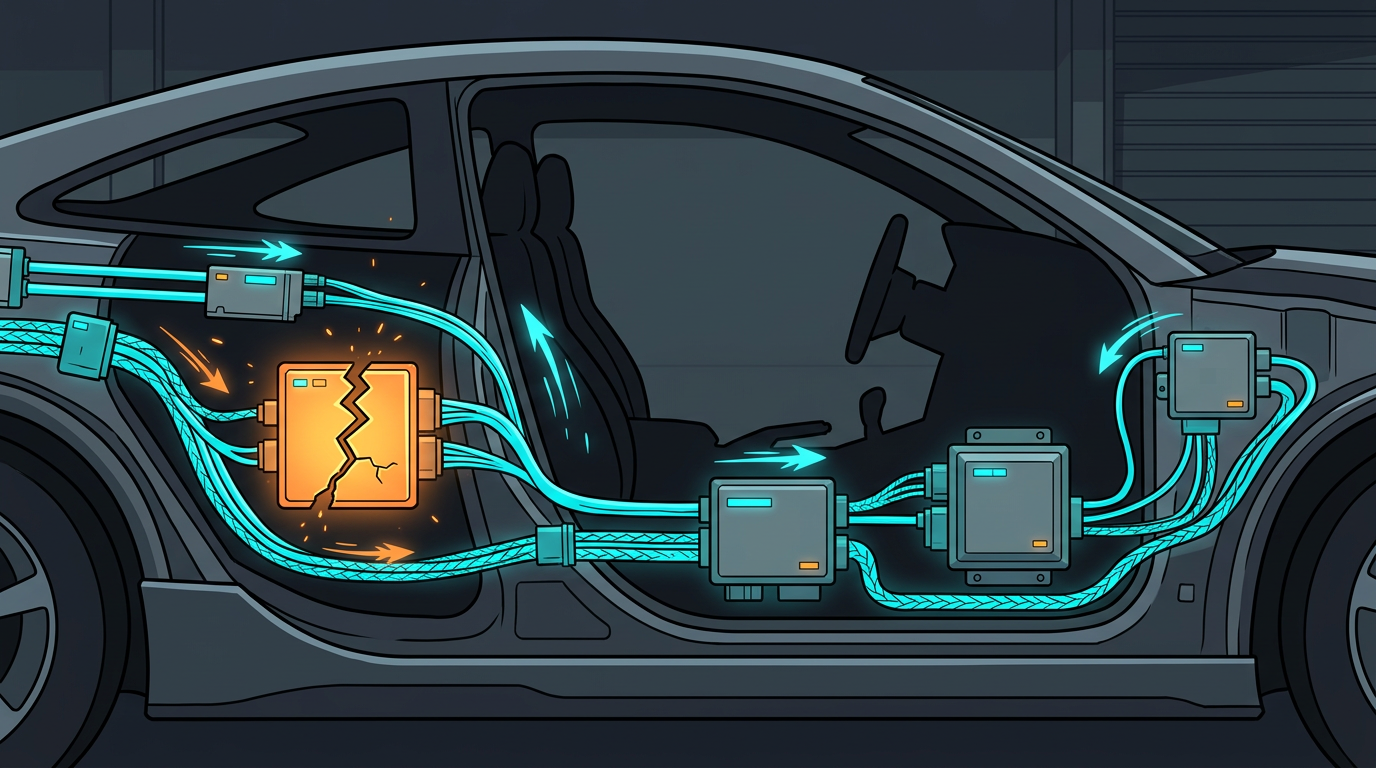
Each flaw turned up in commercial CAN XL hardware. The group then rebuilt the exploits on a bench rig wired to behave like a car’s network, showing how someone who already holds one computer on the bus can swap or intercept messages, silence a chosen machine, or feed different instructions to different systems.
Speed and stealth separate the new attacks from the old ones. Several ran faster and proved harder to spot than equivalent strikes against the decades-old protocol. CAN XL was written to carry bigger messages quicker and to add security features, but its rules for broadcasting messages and recovering from errors are the weak part.
Because the defects sit in the specification rather than in one product, Associate Professor Saman Zonouz said every device built to follow it inherits them.
None of this amounts to a way into a car from outside. What the paper describes is the damage available after someone reaches the internal network, and that is why timing matters: production vehicles have barely started using the standard.
One manufacturer has already patched. The team recommended edits to the CAN XL rules along with message authentication and anomaly detection. The work appeared at the 35th USENIX Security Symposium in Baltimore in August, where judges named it a runner-up for a distinguished paper award. Funding came from the Hyundai America Technical Center and the National Science Foundation’s CHORUS Center.