CarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Notification
  • Autonomous Driving
  • Automotive Ethernet
  • BMS
  • ECU
  • EV
  • ISO/SAE 21434
  • Infotainment
  • OTA Updates
  • OBD-II
  • Pwn2Own
  • RCE
  • SDVs
  • TCU
  • UNECE R155
Cybersecurity

Britain admits 125,000 public chargers have no uniform cyber bar

Cybersecurity

Bosch puts a security gatekeeper on connected motorcycles

Cybersecurity

Trucking group opens a capture-the-flag lab for mechanics

Physical Security

Two California drivers test Axon’s plate database in court

Font ResizerAa
CarThreatCarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
Search
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Sign In Sign In
Follow US
© 2026 Carthreat.com. All right reserved.
Policy & Compliance

EU incident reporting rules for car add-ons take effect September 11

Type-approved vehicles escape the EU Cyber Resilience Act, but telematics boxes and retrofit gear bolted on later face its fast incident reporting from September 11.

CarThreat Staff
Last updated: September 6, 2026 8:59 pm
By
ctadmin
2 Min Read
SHARE

Next Friday, the EU Cyber Resilience Act starts demanding fast incident reports from digital vehicle parts, and the exemption many automakers assumed covers their whole product line stops well short of it. Article 2(2)(c) carves out vehicles type-approved under Regulation (EU) 2019/2144, the framework that made UN R155 and R156 compulsory for EU certification. Parts sold apart from that approval are a different story.

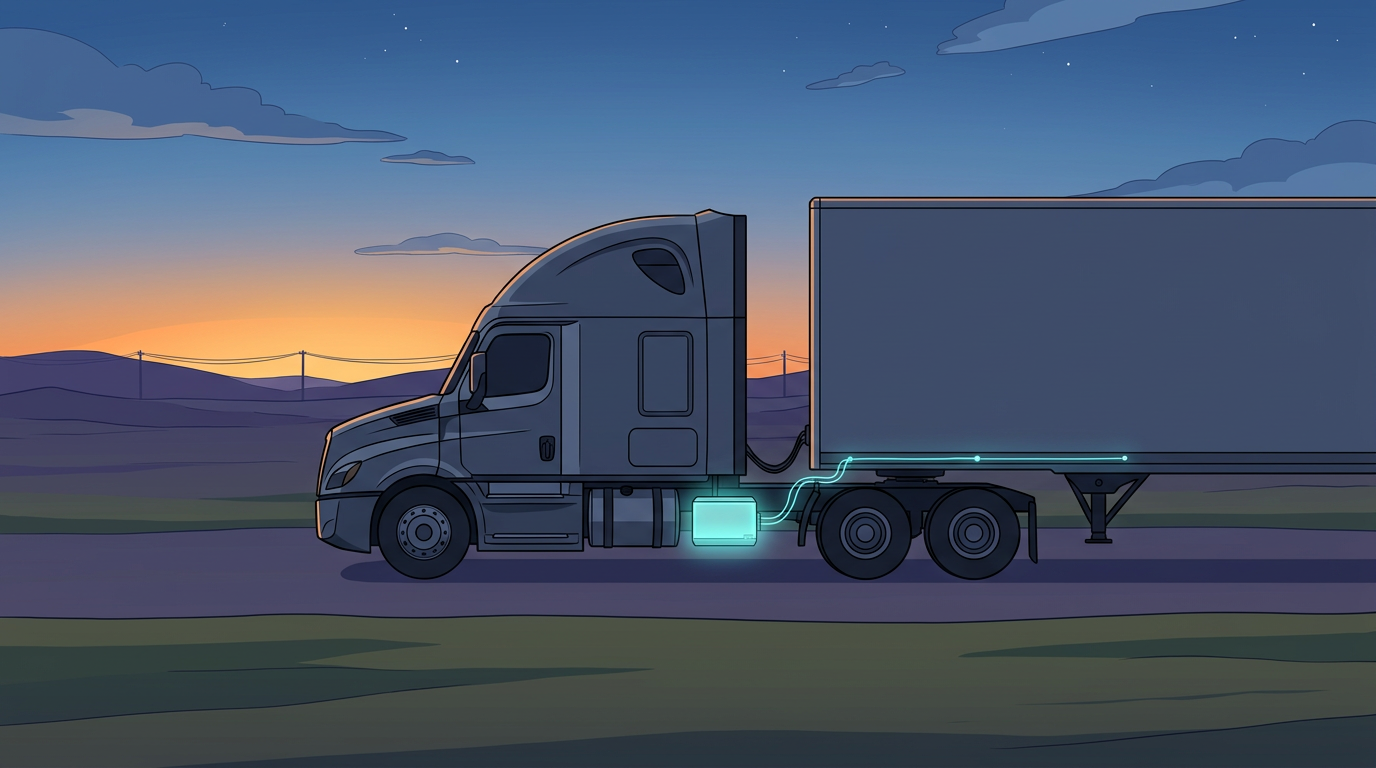
Separate products lose the vehicle’s shield once they leave the factory configuration, Automotive IQ’s new analysis warns. A telematics gateway or fleet box fitted after registration connects to a CAN bus whose security was assessed for type approval, yet that pedigree does not transfer. Retrofit hardware such as route optimization units, driver monitors and reefer refrigeration telemetry lands in CRA scope too, along with EV charging stations and standalone diagnostic tools that never qualified for the vehicle rules.

Once in scope, timelines move fast. An actively exploited vulnerability must reach ENISA as an early warning within 24 hours, a fuller notification follows inside 72 hours, and a final report is due within 14 days.

Trucks and buses complicate the boundary. A chassis maker, a body builder and a telematics vendor may each hold a separate slice of one vehicle’s digital architecture, and only the slice inside the 2019/2144 approval escapes CRA duties. Automotive IQ’s yardstick: a component sold on its own invoice line, outside the approved build, is in scope however tightly it later integrates with the vehicle.

The new rhythm clashes with how commercial vehicle security teams work. Most built incident response around R155’s scheduled audits, documentation-heavy and reviewed on a calendar. CRA notifications are event-driven, so an exploited flaw in a telematics product found late on a Friday starts the clock immediately, with no queue slot waiting for Monday’s triage.
Join Our Newsletter
Subscribe to our newsletter to get our newest articles instantly!
TAGGED:Connected VehiclesCybersecurityISO/SAE 21434RegulationsSoftware-Defined Vehicles (SDVs)UNECE R155
SOURCES:Automotive IQ
Share This Article
Facebook Email Copy Link

Follow US

Find US on Social Medias
FacebookLike
XFollow
YoutubeSubscribe

You Might Also Like

Policy & Compliance

Britain wants cyber rules for public chargers that are still optional

By
ctadmin
October 31, 2026
Policy & Compliance

Connected vehicle security act clears Senate committee hurdle

By
ctadmin
July 22, 2026
A dealership forecourt at night with a glowing cable running from the back office between parked cars
Cybersecurity

Car dealer networks face a year of relentless attacks, mostly phishing

By
ctadmin
September 30, 2026
CybersecurityPhysical Security

Henrico sends its crews up poles after Flock goes quiet

By
ctadmin
November 2, 2026
cel-shaded illustration of a small hatchback in an empty car-share bay with cyan data ribbons streaming away across the lot
Cybersecurity

Car-share service ties member record theft to one employee

By
ctadmin
September 16, 2026
AI Race

Engineers gave a chatbot control of a rented Corolla

By
ctadmin
October 2, 2026

CarThreat

Intelligence for the EV and automotive security market
  • News
  • Features
  • Spotlight
  • Events
  • About Carthreat
  • Our Mission
  • Services
  • Contact Us
  • OBD-II
  • Automotive Ethernet
  • TCU
  • Infotainment Systems
  • SDVs
  • BMS
  • ECU Security
  • CAN Bus
  • Threat Intelligence
  • Cybersecurity
  • Digital Keys
  • Bluetooth Security
  • OTA Updates
  • Vulnerabilities
  • Relay Attacks
  • RCE
  • Data Privacy
  • EVs
  • Autonomous Driving
  • Pwn2Own Automotive
  • ISO/SAE 21434
  • UNECE R155
  • Regulations

© 2026 Carthreat.com. All right reserved.  Privacy Policy | Legal

Welcome Back!

Sign in to your account

Username or Email Address
Password

Lost your password?