CarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Notification
  • Autonomous Driving
  • Automotive Ethernet
  • BMS
  • ECU
  • EV
  • ISO/SAE 21434
  • Infotainment
  • OTA Updates
  • OBD-II
  • Pwn2Own
  • RCE
  • SDVs
  • TCU
  • UNECE R155
Cybersecurity

Britain admits 125,000 public chargers have no uniform cyber bar

Cybersecurity

Bosch puts a security gatekeeper on connected motorcycles

Cybersecurity

Trucking group opens a capture-the-flag lab for mechanics

Physical Security

Two California drivers test Axon’s plate database in court

Font ResizerAa
CarThreatCarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
Search
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Sign In Sign In
Follow US
© 2026 Carthreat.com. All right reserved.
Electric Vehicles

Open Charge Alliance will review Korean tool that hijacked an EV charger

The Open Charge Alliance will review a Korean tool that took over a charger with one altered OCPP message during a live demo.

CarThreat Staff
Last updated: September 3, 2026 11:34 pm
By
ctadmin
2 Min Read
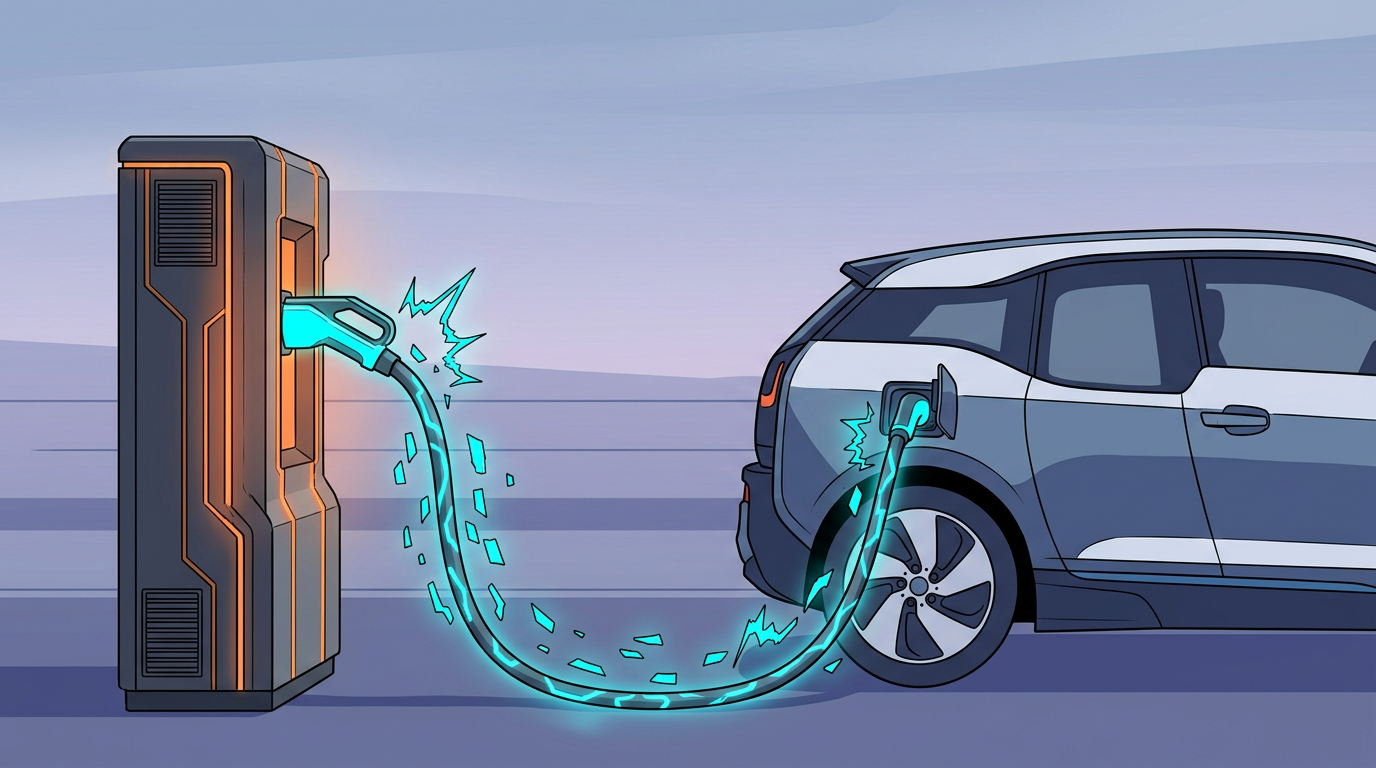
Anime illustration of corrupted data racing up an EV charging cable toward the car
SHARE

A single malformed message let a South Korean security firm seize an EV charger’s software, and the group that maintains the charger protocol now wants to study the tool behind the attack. The Open Charge Alliance has agreed to review Fuzzer, a test harness built by KSign with backing from a South Korean government research program.

KSign ran the demonstration for two OCA officials on September 2 and described the reception as very excellent research. The company modified one message in the Open Charge Point Protocol and pushed it to a charger, which handed over control of its software. Timing mattered: the flaw only fired mid-session, and an idle charger ignored the attack. To make the takeover visible, KSign forced an arbitrary webpage onto the unit’s display, replaying a vulnerability first exploited in a commercial charger at the 2024 Pwn2Own Automotive contest.

Which parts of OCA’s own security guidance can be proven with simulated attacks? That question now sits with KSign, and its answers could decide whether Fuzzer becomes a compliance tool that charger makers use to demonstrate adherence to international standards. The group also passed along a draft of its revised security operations guide. Joint testing events, cooperation with South Korean certification bodies and future Pwn2Own Automotive participation were all on the table for discussion.

Fuzzer grew out of a core information security technology program run by the Ministry of Science and ICT and the IITP evaluation agency. The stakes are grid-sized, senior KSign researcher Kim Seok-hwi argued: every charger is a link into a regional power network, so attackers who compromise large numbers of units at once could trigger outages and physical damage.
Join Our Newsletter
Subscribe to our newsletter to get our newest articles instantly!
TAGGED:CybersecurityEV Charging InfrastructureThreat IntelligenceVehicle SoftwareVulnerabilities
SOURCES:The Elec
Share This Article
Facebook Email Copy Link

Follow US

Find US on Social Medias
FacebookLike
XFollow
YoutubeSubscribe

You Might Also Like

Policy & Compliance

Britain wants cyber rules for public chargers that are still optional

By
ctadmin
October 31, 2026
Policy & Compliance

R155 and R156 turn car cyber compliance into a renewal cycle

By
ctadmin
September 24, 2026
Vehicle software engineers gathered around a blank whiteboard in a studio
CybersecurityInnovation

Japanese car developers name hacking their biggest software worry

By
ctadmin
October 29, 2026
Cybersecurity

Camouflaged patches can hide traffic lights from self-driving cars

By
ctadmin
August 13, 2026
CybersecurityInnovation

Swedish study finds car software flaws drift to the cloud

By
ctadmin
October 22, 2026
Cybersecurity

Hardcoded keys in a truck logging app expose fleet telemetry

By
ctadmin
September 18, 2026

CarThreat

Intelligence for the EV and automotive security market
  • News
  • Features
  • Spotlight
  • Events
  • About Carthreat
  • Our Mission
  • Services
  • Contact Us
  • OBD-II
  • Automotive Ethernet
  • TCU
  • Infotainment Systems
  • SDVs
  • BMS
  • ECU Security
  • CAN Bus
  • Vulnerabilities
  • Relay Attacks
  • RCE
  • Threat Intelligence
  • Cybersecurity
  • Digital Keys
  • Bluetooth Security
  • OTA Updates
  • ISO/SAE 21434
  • UNECE R155
  • Regulations
  • Data Privacy
  • EVs
  • Autonomous Driving
  • Pwn2Own Automotive

© 2026 Carthreat.com. All right reserved.  Privacy Policy | Legal

Welcome Back!

Sign in to your account

Username or Email Address
Password

Lost your password?