CarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Notification
  • Autonomous Driving
  • Automotive Ethernet
  • BMS
  • ECU
  • EV
  • ISO/SAE 21434
  • Infotainment
  • OTA Updates
  • OBD-II
  • Pwn2Own
  • RCE
  • SDVs
  • TCU
  • UNECE R155
India's two-part cyber rulebook now has a certification trail
Cybersecurity

India’s two-part cyber rulebook now has a certification trail

Colmobil shuts some counters after intruders reach its network
Cybersecurity

Colmobil shuts some counters after intruders reach its network

A supplier flaw handed car buyers' payment records to criminals
Cybersecurity

A supplier flaw handed car buyers’ payment records to criminals

Physical Security

Rental cars stored video of Norwegian troops and gate codes

Font ResizerAa
CarThreatCarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
Search
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Sign In Sign In
Follow US
© 2026 Carthreat.com. All right reserved.
Cybersecurity

EV charger firmware compilers escape independent security testing

A Car Hacking Village talk traces EV charger exploits to compilers that have never been independently tested against security standards.

CarThreat Staff
Last updated: August 6, 2026 8:54 pm
By
ctadmin
2 Min Read
SHARE

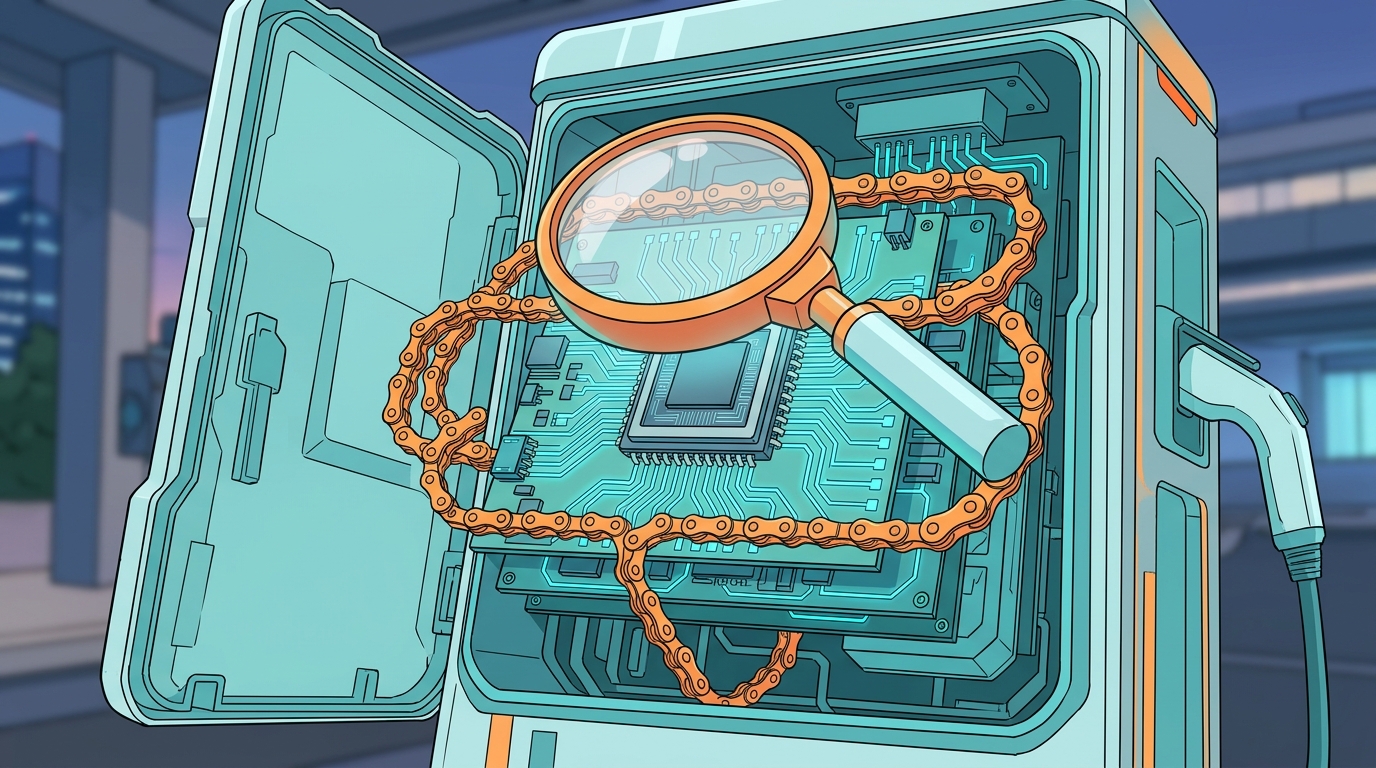
A Car Hacking Village talk at DEF CON 34 will argue that the weakest link in EV charger security may be the compiler, not the code.

Researcher Kangwon Lee points to Pwn2Own Automotive 2026, where a competitor ran Doom on a supercharger after triggering an out-of-bounds write in firmware that came out of an unverified build chain. Lee connects the contest’s exploit classes to an upstream blind spot: the toolchains that compile automotive and EVSE firmware have never been checked against safety or security standards.

The talk maps which compilers are actually qualified, where the coverage gaps are, and why Rust’s memory safety guarantees matter less than they seem if the compiler itself is not verified. A memory-safe language still depends on the toolchain that turns source into firmware behaving as documented.

Lee closes with a practical trust chain for the security community: develop, compile, verify, review. Teams evaluating toolchain integrity should treat the compiler as part of the attack surface, not a neutral black box.

With EV charging infrastructure expanding rapidly and regulators pushing charger makers toward compliance regimes, the session makes the case that firmware supply chain assurance has to include the build tools themselves.
Join Our Newsletter
Subscribe to our newsletter to get our newest articles instantly!
TAGGED:CybersecurityDEF CON 34EV Charging InfrastructureFirmware SecuritySupply ChainVulnerabilities
SOURCES:Car Hacking Village
Share This Article
Facebook Email Copy Link

Follow US

Find US on Social Medias
FacebookLike
XFollow
YoutubeSubscribe

You Might Also Like

iBoy Netflix film scene depicting remote car hacking
Cybersecurity

From Screen to Street: How a Netflix Film Exposes Real Car Hacking Risks

By
ctadmin
May 25, 2026
CybersecurityPolicy & Compliance

NHTSA opens a rewrite of its vehicle cybersecurity playbook

By
ctadmin
October 10, 2026
Cybersecurity

LAPD backs a $235M Axon deal and streetlight plate cameras

By
ctadmin
September 22, 2026
CybersecurityElectric VehiclesEV & Infrastructure

Car cyber incidents jump to 405 in Q1 as EV chargers become the new soft spot

By
ctadmin
July 12, 2026
cel-shaded illustration of a heavy truck brake drum with a glowing cyan barrier blocking orange wireless signal waves
Cybersecurity

Stoneridge puts truck brakes behind a hardware partition

By
ctadmin
September 16, 2026
Research & Innovation

Fake brake alerts in V2X networks can trigger phantom stops

By
ctadmin
August 9, 2026

CarThreat

Intelligence for the EV and automotive security market
  • News
  • Features
  • Spotlight
  • Events
  • About Carthreat
  • Our Mission
  • Services
  • Contact Us
  • OBD-II
  • Automotive Ethernet
  • TCU
  • Infotainment Systems
  • SDVs
  • BMS
  • ECU Security
  • CAN Bus
  • OTA Updates
  • Vulnerabilities
  • Relay Attacks
  • RCE
  • Threat Intelligence
  • Cybersecurity
  • Digital Keys
  • Bluetooth Security
  • ISO/SAE 21434
  • UNECE R155
  • Regulations
  • Data Privacy
  • EVs
  • Autonomous Driving
  • Pwn2Own Automotive

© 2026 Carthreat.com. All right reserved.  Privacy Policy | Legal

Welcome Back!

Sign in to your account

Username or Email Address
Password

Lost your password?