CarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Notification
  • Autonomous Driving
  • Automotive Ethernet
  • BMS
  • ECU
  • EV
  • ISO/SAE 21434
  • Infotainment
  • OTA Updates
  • OBD-II
  • Pwn2Own
  • RCE
  • SDVs
  • TCU
  • UNECE R155
India's two-part cyber rulebook now has a certification trail
Cybersecurity

India’s two-part cyber rulebook now has a certification trail

Colmobil shuts some counters after intruders reach its network
Cybersecurity

Colmobil shuts some counters after intruders reach its network

A supplier flaw handed car buyers' payment records to criminals
Cybersecurity

A supplier flaw handed car buyers’ payment records to criminals

Physical Security

Rental cars stored video of Norwegian troops and gate codes

Font ResizerAa
CarThreatCarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
Search
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Sign In Sign In
Follow US
© 2026 Carthreat.com. All right reserved.
Car NewsCybersecurity

Critical buffer overflow in EV charging protocol puts vehicles at risk

A stack-based buffer overflow in the SLAC protocol implementation affects both EVs and charging stations.

CarThreat Staff
Last updated: July 18, 2026 7:20 am
By
ctadmin
2 Min Read
SHARE

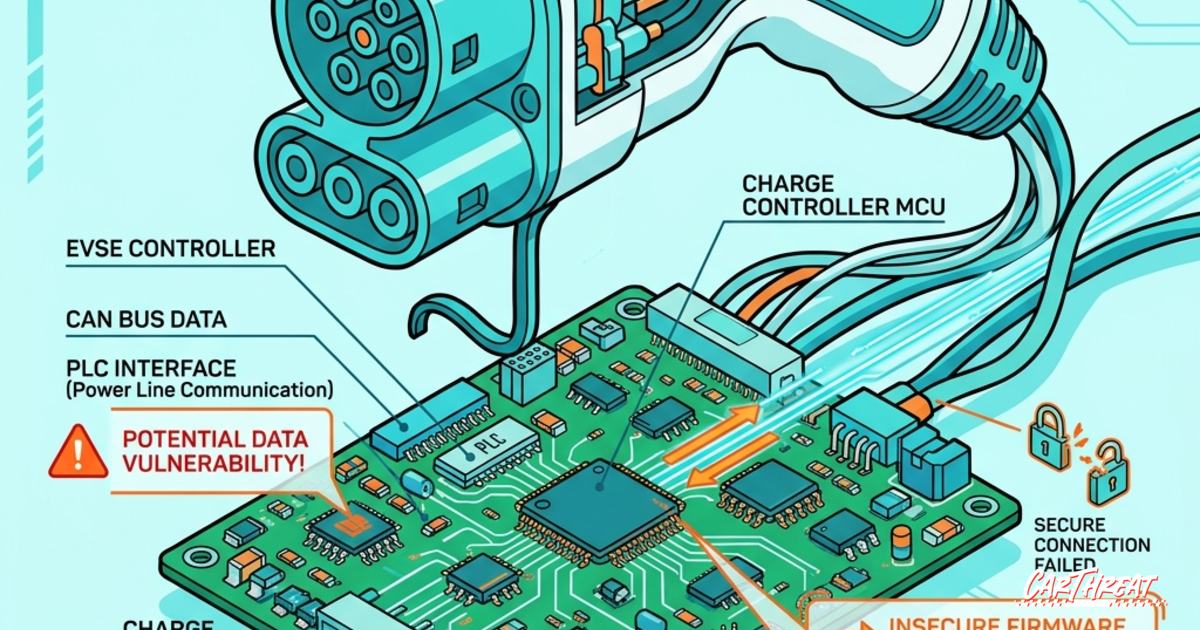
PlaxidityX researchers have disclosed a critical stack-based buffer overflow vulnerability in the open-source implementation of the Signal Level Attenuation Characterization protocol used in EV charging communication. Tracked as CVE-2025-27071, the flaw resides in the open-plc-utils toolkit that implements the SLAC protocol defined by ISO 15118 and DIN SPEC 70121.

Both electric vehicles and charging stations are affected. The vulnerability allows an attacker to trigger arbitrary code execution by sending a crafted packet where the “Number of Groups” field is not validated before being used in a memcpy operation, creating a stack-based buffer overflow.

The SLAC protocol ensures reliable Powerline Communication between EVs and charging stations, handling the handshake process before IP communication begins. The open-plc-utils project provides tools for interacting with Qualcomm Atheros Powerline chips, making the vulnerable code present in many charging station implementations that run on Linux.

PlaxidityX reported the issue to Qualcomm in December 2024, leading to a security advisory in August 2025 and a subsequent patch. The vulnerability was found in both the EV side and the charging station side of the protocol implementation.

As EV adoption grows alongside Vehicle-to-Grid integration, securing protocol implementations becomes critical. This finding highlights the need for rigorous memory-safety validation in charging infrastructure firmware, where a single unvalidated byte can cascade into full system compromise.
Join Our Newsletter
Subscribe to our newsletter to get our newest articles instantly!
TAGGED:Automotive Attack SurfaceBuffer OverflowCISAEV ChargingEV Charging Security
SOURCES:CISA
Share This Article
Facebook Email Copy Link

Follow US

Find US on Social Medias
FacebookLike
XFollow
YoutubeSubscribe

You Might Also Like

Cybersecurity

T-Systems Builds Dedicated Private Cloud for Volkswagen Group to Centralize App Infrastructure

By
ctadmin
July 2, 2026
Car News

New 2022 Porsche Panamera Reviews, Pricing & Specs

By
ctadmin
August 30, 2021
Cybersecurity

Chinese lidar faces federal review as lawmakers push bans

By
ctadmin
August 23, 2026
Cybersecurity

ShinyHunters claims 200,000-record haul from Florida motor vehicle database

By
ctadmin
September 9, 2026
CybersecurityResearch & Innovation

Researchers count the trackers riding along in 21 cars

By
ctadmin
September 30, 2026
Cybersecurity

NHTSA tells self-driving car makers to stop blocking ambulances

By
ctadmin
July 12, 2026

CarThreat

Intelligence for the EV and automotive security market
  • News
  • Features
  • Spotlight
  • Events
  • About Carthreat
  • Our Mission
  • Services
  • Contact Us
  • OBD-II
  • Automotive Ethernet
  • TCU
  • Infotainment Systems
  • SDVs
  • BMS
  • ECU Security
  • CAN Bus
  • Vulnerabilities
  • Relay Attacks
  • RCE
  • Threat Intelligence
  • Cybersecurity
  • Digital Keys
  • Bluetooth Security
  • OTA Updates
  • ISO/SAE 21434
  • UNECE R155
  • Regulations
  • Data Privacy
  • EVs
  • Autonomous Driving
  • Pwn2Own Automotive

© 2026 Carthreat.com. All right reserved.  Privacy Policy | Legal

Welcome Back!

Sign in to your account

Username or Email Address
Password

Lost your password?