CarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Notification
  • Autonomous Driving
  • Automotive Ethernet
  • BMS
  • ECU
  • EV
  • ISO/SAE 21434
  • Infotainment
  • OTA Updates
  • OBD-II
  • Pwn2Own
  • RCE
  • SDVs
  • TCU
  • UNECE R155
India's two-part cyber rulebook now has a certification trail
Cybersecurity

India’s two-part cyber rulebook now has a certification trail

Colmobil shuts some counters after intruders reach its network
Cybersecurity

Colmobil shuts some counters after intruders reach its network

A supplier flaw handed car buyers' payment records to criminals
Cybersecurity

A supplier flaw handed car buyers’ payment records to criminals

Physical Security

Rental cars stored video of Norwegian troops and gate codes

Font ResizerAa
CarThreatCarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
Search
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Sign In Sign In
Follow US
© 2026 Carthreat.com. All right reserved.
Cybersecurity

Times Car members told an intrusion may have taken license files

A Japanese car-sharing operator says intruders may have reached member names, license details and identity documents before engineers cut the connection.

CarThreat Staff
Last updated: September 30, 2026 3:31 am
By
ctadmin
2 Min Read
SHARE

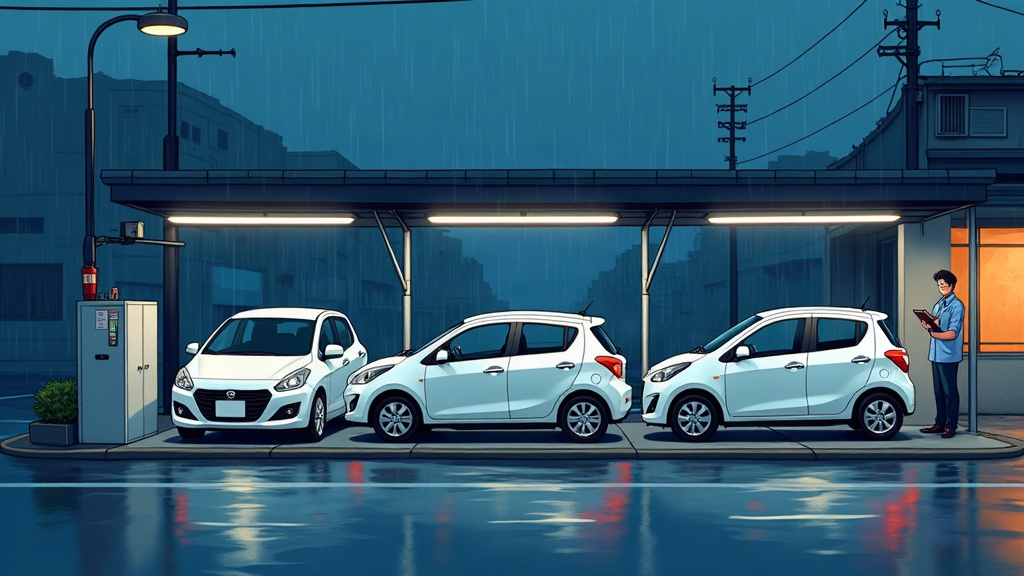
Park24, the Japanese operator behind the Times Car sharing network, has told customers that someone outside the company reached its member files.

Its monitoring systems flagged the intrusion at 9:07 am on September 25. By 7:25 am the next morning, engineers had cut the route the attacker used, blocked traffic from the source and confirmed the door was shut. The company says it is still watching.

What may have left the building is broad. Park24 lists names, addresses, dates of birth, phone numbers, email addresses, membership numbers, license information, identity verification documents, corporate member details and linked service IDs. Former members are included, not only current ones.

teiss reported that the haul covered roughly 6.6 million accounts. Park24’s investor filing on September 28 confirmed the breach at a consolidated subsidiary and said no widespread publication or misuse of the records had been found so far.

The operator has reported the incident to Japan’s Personal Information Protection Commission and brought in outside specialists to trace the cause and the full blast radius. It is also warning members about emails, calls and text messages that impersonate the brand, and reminding them that it never asks for passwords or card numbers.

Car sharing asks for more than a payment method. Sign-up requires a driving license and identity documents, which makes a car-share database a compact supply of the exact material fraudsters use to open accounts and clear verification checks. That is why the painful part here is not the volume but the document images.
Join Our Newsletter
Subscribe to our newsletter to get our newest articles instantly!
TAGGED:Connected VehiclesCybersecurityData PrivacyRegulationsThreat IntelligenceVulnerabilities
SOURCES:Park24 news releaseteissPark24 investor disclosure
Share This Article
Facebook Email Copy Link

Follow US

Find US on Social Medias
FacebookLike
XFollow
YoutubeSubscribe

You Might Also Like

Policy & Compliance

An ownership clause snags the vote to ban Chinese cars for good

By
ctadmin
September 26, 2026
Cybersecurity

Sony patches seven car radio flaws reachable over Bluetooth

By
ctadmin
October 15, 2026
Cybersecurity

Autocrypt reclaims DEF CON car hacking crown with AI crew

By
ctadmin
August 14, 2026
cel-shaded illustration of an IT appliance on a workbench in a dark dealership service bay, a cyan cable running out through the open bay door
Cybersecurity

Dealer software vendor traces Storm intrusion to a support tool

By
ctadmin
September 16, 2026
Cybersecurity

Identity-based crypto removes plaintext keys from CCS charging

By
ctadmin
August 12, 2026
Cybersecurity

Dealer-installed alarm exposes 2 million cars to Bluetooth theft attacks

By
ctadmin
July 21, 2026

CarThreat

Intelligence for the EV and automotive security market
  • News
  • Features
  • Spotlight
  • Events
  • About Carthreat
  • Our Mission
  • Services
  • Contact Us
  • OBD-II
  • Automotive Ethernet
  • TCU
  • Infotainment Systems
  • SDVs
  • BMS
  • ECU Security
  • CAN Bus
  • OTA Updates
  • Vulnerabilities
  • Relay Attacks
  • RCE
  • Threat Intelligence
  • Cybersecurity
  • Digital Keys
  • Bluetooth Security
  • ISO/SAE 21434
  • UNECE R155
  • Regulations
  • Data Privacy
  • EVs
  • Autonomous Driving
  • Pwn2Own Automotive

© 2026 Carthreat.com. All right reserved.  Privacy Policy | Legal

Welcome Back!

Sign in to your account

Username or Email Address
Password

Lost your password?