CarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Notification
  • Autonomous Driving
  • Automotive Ethernet
  • BMS
  • ECU
  • EV
  • ISO/SAE 21434
  • Infotainment
  • OTA Updates
  • OBD-II
  • Pwn2Own
  • RCE
  • SDVs
  • TCU
  • UNECE R155
India's two-part cyber rulebook now has a certification trail
Cybersecurity

India’s two-part cyber rulebook now has a certification trail

Colmobil shuts some counters after intruders reach its network
Cybersecurity

Colmobil shuts some counters after intruders reach its network

A supplier flaw handed car buyers' payment records to criminals
Cybersecurity

A supplier flaw handed car buyers’ payment records to criminals

Physical Security

Rental cars stored video of Norwegian troops and gate codes

Font ResizerAa
CarThreatCarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
Search
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Sign In Sign In
Follow US
© 2026 Carthreat.com. All right reserved.
Cybersecurity

VicOne hooks fresh CVE feeds into vehicle risk models

VicOne and CYMETRIS have linked vulnerability intelligence to vehicle architecture models so OEMs can tell which fresh CVEs actually touch a specific car programme.

CarThreat Staff
Last updated: September 24, 2026 2:38 am
By
ctadmin
2 Min Read
SHARE

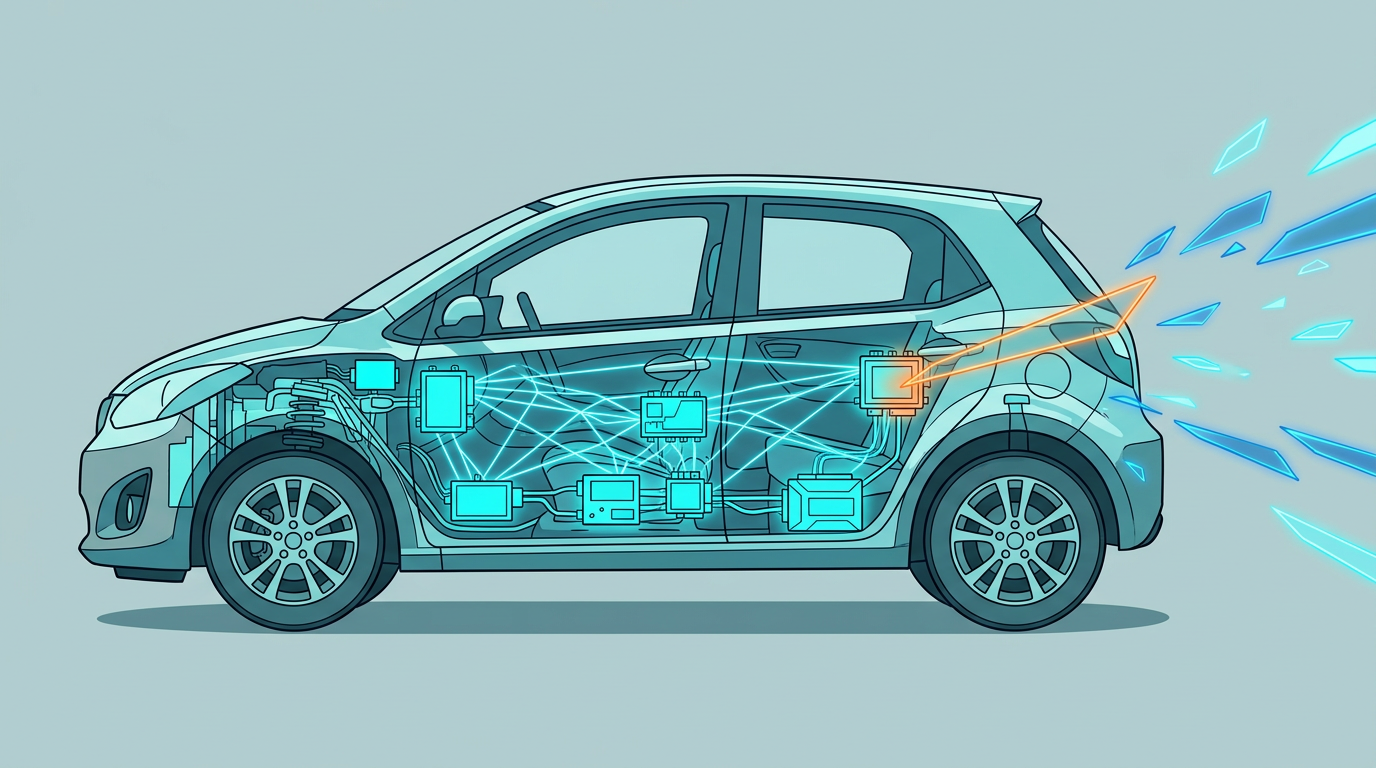
A fresh CVE lands, and a product security team has minutes to answer an awkward question: does this one actually touch our car? VicOne and CYMETRIS have wired their tools together to answer it automatically.

CYMETRIS supplies the system-level risk model built by the Munich-based cyber risk engineering firm. VicOne feeds it automotive vulnerability and software bill of materials intelligence gathered by its xZETA platform, including a proprietary impact rating and zero-day data from Trend Micro’s ZDI programme. A bidirectional API carries findings between the two, mapping them onto assets and ECUs, testing whether existing controls could be circumvented and recording every treatment decision. Architecture context travels back the other way, so a finding is judged against a system model rather than a flat component list.

The companies call the result Live TARA: threat analysis and risk assessment that stays current as software and threats shift.

Volume is the reason. An Epoch AI analysis cited by VicOne counted roughly 2,500 high and critical CVEs disclosed by 21 major technology organisations in July 2026, about 60% above June’s figure and five times the monthly high recorded before April 2026.

“Do not send us more alerts” is the message VicOne chief executive Max Cheng gives, arguing teams need to know which findings can affect a specific vehicle and what to do next.

VicOne says the workflow produces evidence for ISO/SAE 21434 and UN R155 work. Live demonstrations are scheduled for Baden-Baden’s ELIV 2026 on October 14 and 15, and for Nuremberg’s it-sa show from October 27 to 29.
Join Our Newsletter
Subscribe to our newsletter to get our newest articles instantly!
TAGGED:ECU SecurityISO/SAE 21434Software-Defined Vehicles (SDVs)Threat IntelligenceVehicle SoftwareVulnerabilities
SOURCES:VicOne
Share This Article
Facebook Email Copy Link

Follow US

Find US on Social Medias
FacebookLike
XFollow
YoutubeSubscribe

You Might Also Like

Cybersecurity

EU Mandate for Driver Monitoring Raises Biometric Privacy in Connected Cars

By
ctadmin
July 12, 2026
AI Race

Engineers gave a chatbot control of a rented Corolla

By
ctadmin
October 2, 2026
CybersecurityElectric VehiclesEV & Infrastructure

Car cyber incidents jump to 405 in Q1 as EV chargers become the new soft spot

By
ctadmin
July 12, 2026
Cybersecurity

Tokyo Connected Car Security Seminar Tackles ECU Hardening and Autonomous Protection

By
ctadmin
May 22, 2026
Cybersecurity

PlaxidityX vDome Wins CLEPA Innovation Award for Proactive Anti-Theft Tech

By
ctadmin
May 22, 2026
CybersecurityPolicy & Compliance

EU issues 2026 mandate for connected vehicle cybersecurity requirements

By
ctadmin
July 18, 2026

CarThreat

Intelligence for the EV and automotive security market
  • News
  • Features
  • Spotlight
  • Events
  • About Carthreat
  • Our Mission
  • Services
  • Contact Us
  • OBD-II
  • Automotive Ethernet
  • TCU
  • Infotainment Systems
  • SDVs
  • BMS
  • ECU Security
  • CAN Bus
  • OTA Updates
  • Vulnerabilities
  • Relay Attacks
  • RCE
  • Threat Intelligence
  • Cybersecurity
  • Digital Keys
  • Bluetooth Security
  • ISO/SAE 21434
  • UNECE R155
  • Regulations
  • Data Privacy
  • EVs
  • Autonomous Driving
  • Pwn2Own Automotive

© 2026 Carthreat.com. All right reserved.  Privacy Policy | Legal

Welcome Back!

Sign in to your account

Username or Email Address
Password

Lost your password?