CarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Notification
  • Autonomous Driving
  • Automotive Ethernet
  • BMS
  • ECU
  • EV
  • ISO/SAE 21434
  • Infotainment
  • OTA Updates
  • OBD-II
  • Pwn2Own
  • RCE
  • SDVs
  • TCU
  • UNECE R155
India's two-part cyber rulebook now has a certification trail
Cybersecurity

India’s two-part cyber rulebook now has a certification trail

Colmobil shuts some counters after intruders reach its network
Cybersecurity

Colmobil shuts some counters after intruders reach its network

A supplier flaw handed car buyers' payment records to criminals
Cybersecurity

A supplier flaw handed car buyers’ payment records to criminals

Physical Security

Rental cars stored video of Norwegian troops and gate codes

Font ResizerAa
CarThreatCarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
Search
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Sign In Sign In
Follow US
© 2026 Carthreat.com. All right reserved.
Cybersecurity

First car head unit malware hides inside Android update channel

Kaspersky finds the first Android malware built for car head units, delivered through the devices' own update channel.

CarThreat Staff
Last updated: August 22, 2026 9:52 pm
By
ctadmin
2 Min Read
SHARE

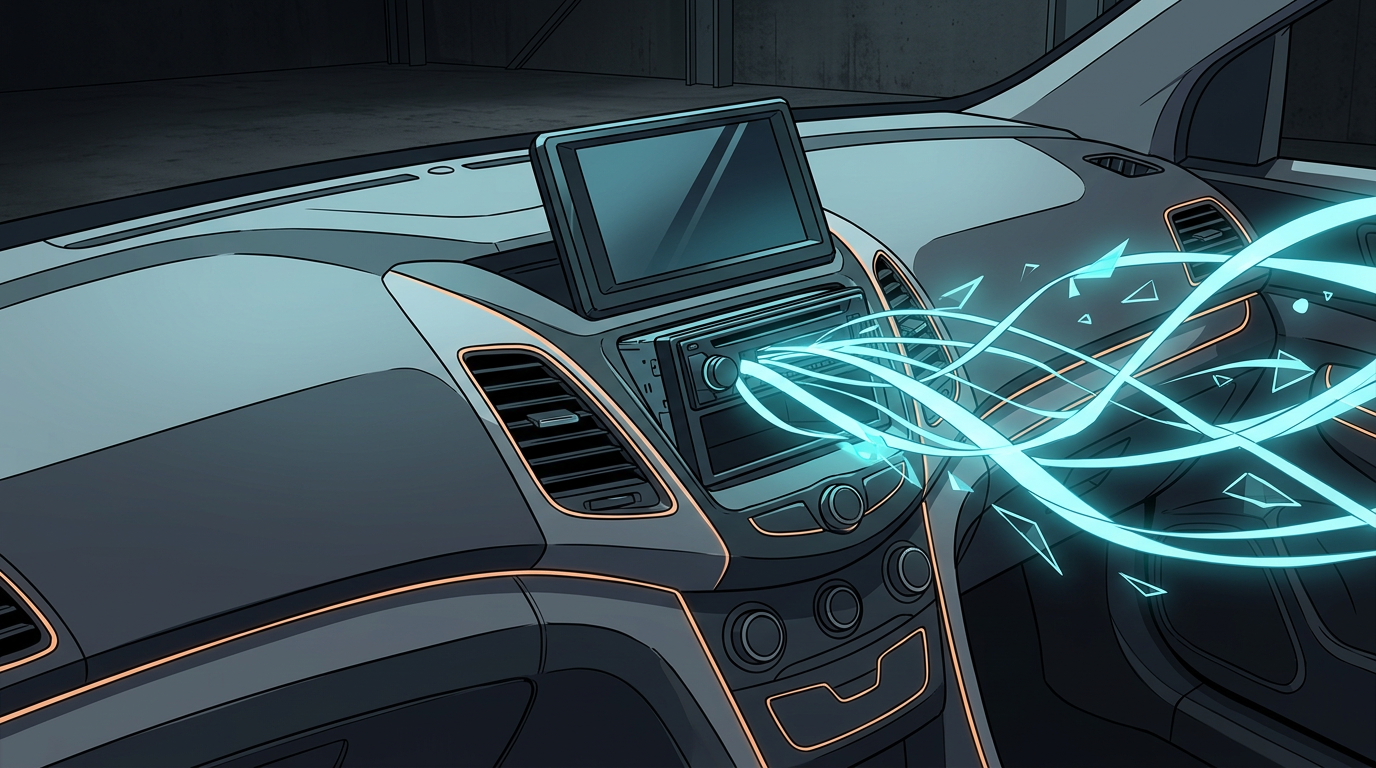
Kaspersky has documented what it calls the first Android malware campaign built specifically for car head units, a family that hitches a ride on the devices’ legitimate update channel to plant ad fraud and proxy botnet code.

The malware targets infotainment firmware developed by DoFun, which powers aftermarket head units and some factory-built systems. Researchers found it distributed through the update mechanism of a system app called TWCore, which normally fetches analytics and APK updates over an MQTT broker hosted on a cardoor.cn subdomain. Attackers weaponized that channel to drop a loader named JarService, which installs a covert payload that reports to a command-and-control endpoint every 90 minutes.

Security researcher Dmitry Kalinin said this is the first documented case of malware on a car head unit with an infection chain specific to that device type. Kaspersky attributes the campaign with high confidence to the MoYu Group, the crew behind the BADBOX ad fraud and residential proxy scheme that Google sued over in July 2025.

Head units are an attractive target because they sit at the center of the cockpit, blend multimedia with partial vehicle control, and carry a SIM slot for navigation and updates. Kalinin noted that delivery methods keep evolving, from pre-installed backdoors to compromised apps, and that this case abused the software update functionality of a legitimate system component. The vendor addressed the flaw after responsible disclosure, and owners should install the latest firmware while treating head unit app sources with the same caution as smartphone downloads.
Join Our Newsletter
Subscribe to our newsletter to get our newest articles instantly!
TAGGED:Connected VehiclesFirmware SecurityInfotainment SystemsMalwareOTA UpdatesRemote Code Execution (RCE)Threat IntelligenceVehicle Software
SOURCES:The Hacker News
Share This Article
Facebook Email Copy Link

Follow US

Find US on Social Medias
FacebookLike
XFollow
YoutubeSubscribe

You Might Also Like

Cybersecurity

Generative AI Tools Heighten Vehicle Vulnerability Risks, South Korean Experts Warn

By
ctadmin
June 19, 2026
Cybersecurity

Extortion group Helix claims a million files from Uber Freight

By
ctadmin
August 13, 2026
Cybersecurity

GM widens in-car recording while promising footage stays local

By
ctadmin
September 12, 2026
Cybersecurity

Stellantis and Microsoft Expand Partnership to Tackle Automotive AI Security

By
ctadmin
May 22, 2026
Cybersecurity

Repeated patterns hijack depth readings of car stereo cameras

By
ctadmin
August 13, 2026
CybersecurityElectric VehiclesEV & Infrastructure

Car cyber incidents jump to 405 in Q1 as EV chargers become the new soft spot

By
ctadmin
July 12, 2026

CarThreat

Intelligence for the EV and automotive security market
  • News
  • Features
  • Spotlight
  • Events
  • About Carthreat
  • Our Mission
  • Services
  • Contact Us
  • OBD-II
  • Automotive Ethernet
  • TCU
  • Infotainment Systems
  • SDVs
  • BMS
  • ECU Security
  • CAN Bus
  • Vulnerabilities
  • Relay Attacks
  • RCE
  • Threat Intelligence
  • Cybersecurity
  • Digital Keys
  • Bluetooth Security
  • OTA Updates
  • ISO/SAE 21434
  • UNECE R155
  • Regulations
  • Data Privacy
  • EVs
  • Autonomous Driving
  • Pwn2Own Automotive

© 2026 Carthreat.com. All right reserved.  Privacy Policy | Legal

Welcome Back!

Sign in to your account

Username or Email Address
Password

Lost your password?