CarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Notification
  • Autonomous Driving
  • Automotive Ethernet
  • BMS
  • ECU
  • EV
  • ISO/SAE 21434
  • Infotainment
  • OTA Updates
  • OBD-II
  • Pwn2Own
  • RCE
  • SDVs
  • TCU
  • UNECE R155
India's two-part cyber rulebook now has a certification trail
Cybersecurity

India’s two-part cyber rulebook now has a certification trail

Colmobil shuts some counters after intruders reach its network
Cybersecurity

Colmobil shuts some counters after intruders reach its network

A supplier flaw handed car buyers' payment records to criminals
Cybersecurity

A supplier flaw handed car buyers’ payment records to criminals

Physical Security

Rental cars stored video of Norwegian troops and gate codes

Font ResizerAa
CarThreatCarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
Search
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Sign In Sign In
Follow US
© 2026 Carthreat.com. All right reserved.
Electric Vehicles

Charging framework bugs let sessions run on after remote stop

An audit of the open-source everest-core charging stack found 11 concurrency bugs that can bypass payment controls.

CarThreat Staff
Last updated: August 9, 2026 10:43 pm
By
ctadmin
2 Min Read
Charging framework bugs let sessions run on after remote stop
SHARE

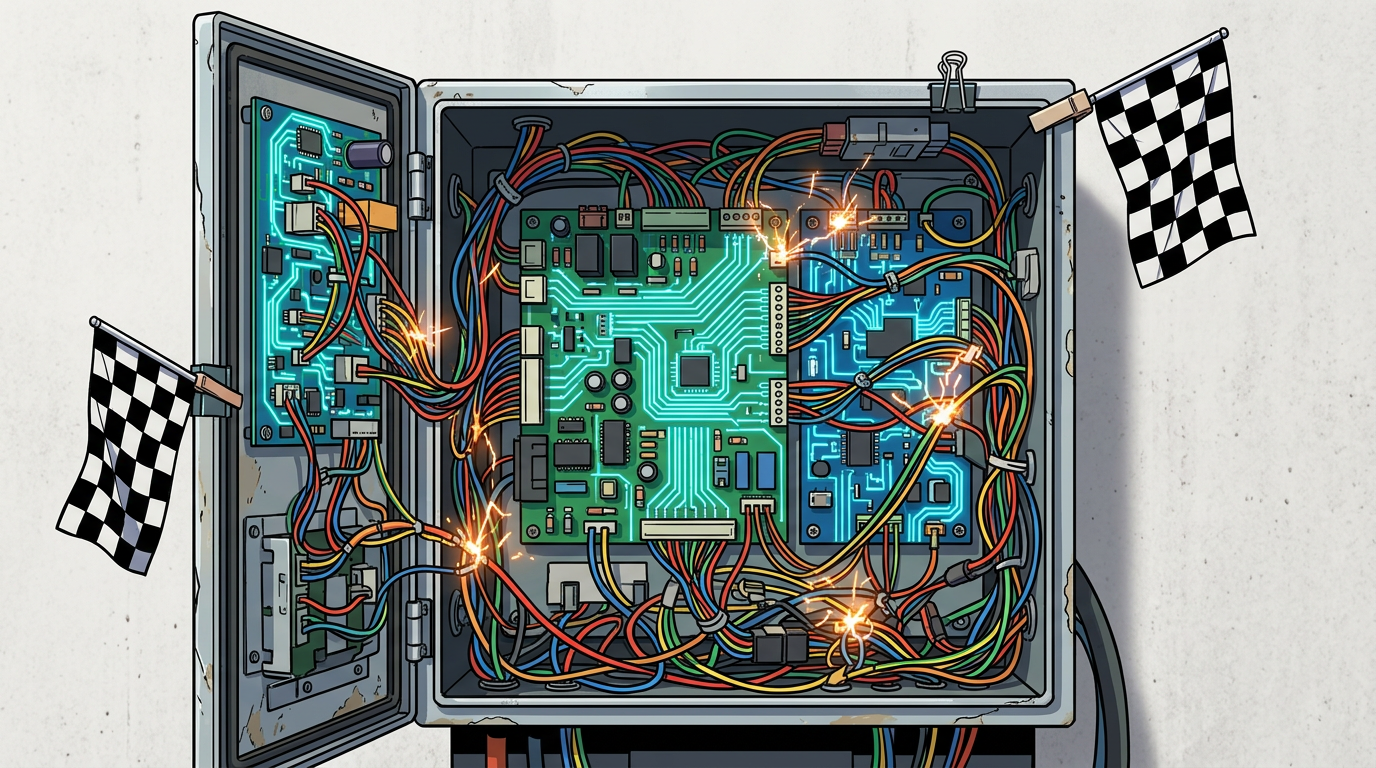
An audit of everest-core, the open-source charging framework under the Linux Foundation Energy umbrella, turned up 11 concurrency flaws with public CVE IDs. The findings were presented at VehicleSec ’26 in Baltimore by Jaeyeong Lee and Seonhyeong Lee.

The problems cluster around how the software manages shared state. Eight of the bugs were reproduced as data races with the TSan, ASan, and UBSan sanitizers, and the other three were confirmed through logic-based proof-of-concept exploits that violate state integrity.

The impact reaches into the parts of a charging station that handle money and power. A session can keep drawing current after an operator sends a remote stop, an authorization withdrawal can be sidestepped, and memory corruption can knock the station offline entirely.

The authors point to three recurring causes in the code: locking discipline that is not applied consistently, state transitions that lack atomicity, and asynchronous events that arrive without validation. everest-core runs on top of hardware control, communication protocols, and cloud management all at once, so a single callback misstep ripples through the stack.

Because the framework is shared infrastructure, the researchers say the CVEs deserve fast attention from charge point operators and vendors. A patch applied upstream protects the whole ecosystem, and an unpatched deployment leaves the same exposed code paths in payment and authorization flows.
Join Our Newsletter
Subscribe to our newsletter to get our newest articles instantly!
TAGGED:Charging InfrastructureElectric Vehicles (EVs)Firmware SecurityThreat IntelligenceVehicle SoftwareVulnerabilities
SOURCES:USENIX VehicleSec '26
Share This Article
Facebook Email Copy Link

Follow US

Find US on Social Medias
FacebookLike
XFollow
YoutubeSubscribe

You Might Also Like

Policy & Compliance

BYD rewrites Australian privacy policy after Four Corners questions

By
ctadmin
September 21, 2026
Policy & Compliance

Australia’s car dealers demand answers as BYD opens a review

By
ctadmin
September 26, 2026
Cybersecurity

CARS24 files complaint over 3,100 customer records sold to rival

By
ctadmin
September 6, 2026
Cybersecurity

DEF CON demo drains a locked EV battery with no keys

By
ctadmin
August 6, 2026
Cybersecurity

$1 Texas auto fee secretly bankrolled Flock camera network

By
ctadmin
August 31, 2026
CybersecurityElectric Vehicles

E-rickshaw hacking scare exposes cybersecurity flaws in connected EVs

By
ctadmin
July 21, 2026

CarThreat

Intelligence for the EV and automotive security market
  • News
  • Features
  • Spotlight
  • Events
  • About Carthreat
  • Our Mission
  • Services
  • Contact Us
  • OBD-II
  • Automotive Ethernet
  • TCU
  • Infotainment Systems
  • SDVs
  • BMS
  • ECU Security
  • CAN Bus
  • Threat Intelligence
  • Cybersecurity
  • Digital Keys
  • Bluetooth Security
  • OTA Updates
  • Vulnerabilities
  • Relay Attacks
  • RCE
  • Data Privacy
  • EVs
  • Autonomous Driving
  • Pwn2Own Automotive
  • ISO/SAE 21434
  • UNECE R155
  • Regulations

© 2026 Carthreat.com. All right reserved.  Privacy Policy | Legal

Welcome Back!

Sign in to your account

Username or Email Address
Password

Lost your password?