CarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Notification
  • Autonomous Driving
  • Automotive Ethernet
  • BMS
  • ECU
  • EV
  • ISO/SAE 21434
  • Infotainment
  • OTA Updates
  • OBD-II
  • Pwn2Own
  • RCE
  • SDVs
  • TCU
  • UNECE R155
India's two-part cyber rulebook now has a certification trail
Cybersecurity

India’s two-part cyber rulebook now has a certification trail

Colmobil shuts some counters after intruders reach its network
Cybersecurity

Colmobil shuts some counters after intruders reach its network

A supplier flaw handed car buyers' payment records to criminals
Cybersecurity

A supplier flaw handed car buyers’ payment records to criminals

Physical Security

Rental cars stored video of Norwegian troops and gate codes

Font ResizerAa
CarThreatCarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
Search
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Sign In Sign In
Follow US
© 2026 Carthreat.com. All right reserved.
Cybersecurity

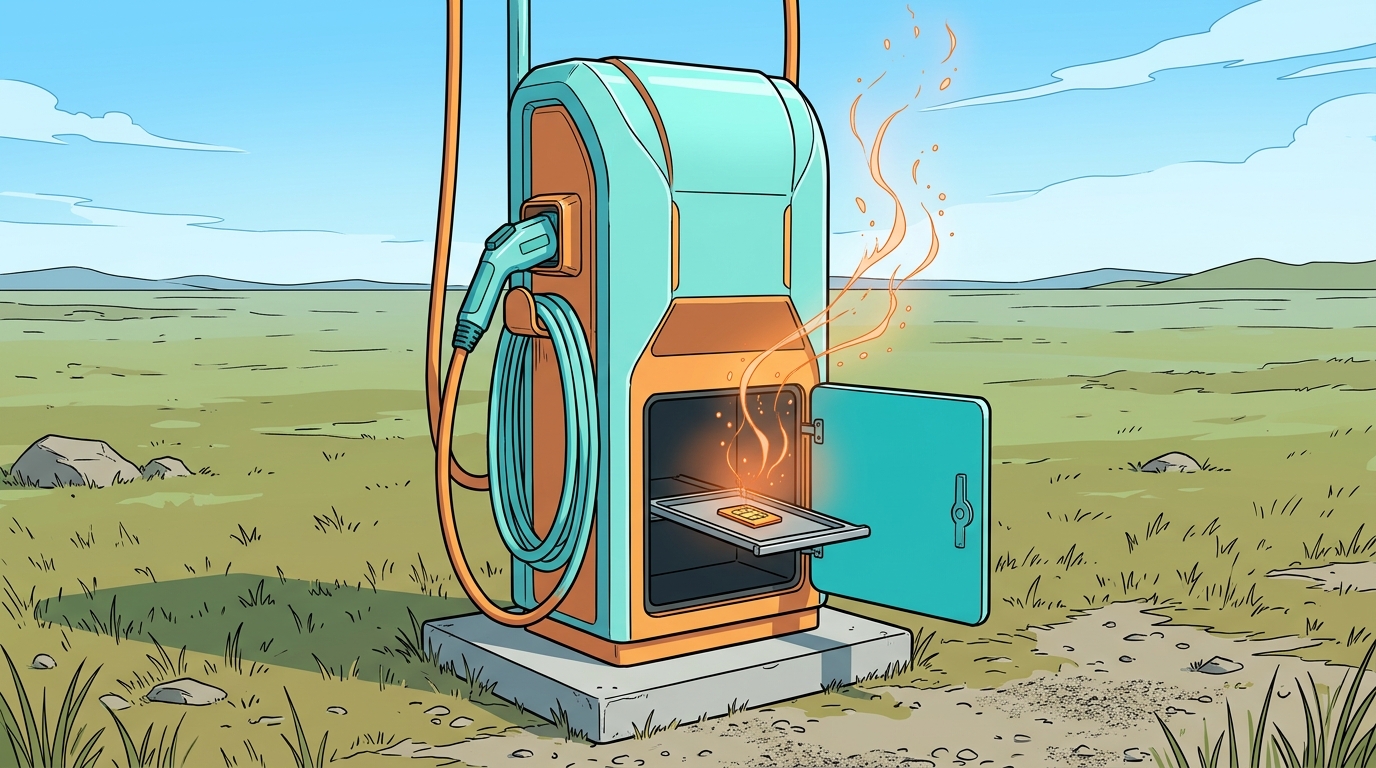
Rogue SIM cards hijack EV chargers through a hidden modem command

A hostile SIM card can command the modems inside EV chargers and car telematics units to run attacker code.

CarThreat Staff
Last updated: August 12, 2026 3:59 am
By
ctadmin
2 Min Read
SHARE

Researchers from the University of Birmingham and the firm Fuzzware demonstrated that a SIM card swapped into the right device can force the modem it sits in to run attacker-chosen commands. Their proof of concept executed custom code on a store-bought EV charger, and they say car telematics units face the same exposure.

The lever is RUN AT, an obscure feature that lets a card push instructions to the modem before the modem asks for anything. When enabled, it hands the SIM the modem’s AT command language, the control interface that chip vendors extend with their own commands. In a survey of 26 phones and cellular modules, nine devices accepted the instruction. Six of eight cellular modules did, including five Quectel parts drawn from an EV charger, an industrial router, and a vehicle telematics control unit. Only three of 18 phones did, all Android handsets.

All nine devices run Qualcomm communication processors, though five other Qualcomm phones rejected the command, a gap the paper attributes to vendor customization. Qualcomm says it has produced a hardened configuration that turns the interface off by default, and Quectel reports mitigating the file-access flaw while still working on the interface itself. Neither vendor has released an advisory, and no real-world exploitation has surfaced.

The card has to be in the slot to matter, which means a physical swap, a thin interposer, a corrupted carrier employee, or tampering on the production line. Unattended chargers with reachable SIM trays are the obvious target. The researchers want the interface hardened, deprecated, or removed, and advise fleet operators to ask suppliers whether RUN AT ships enabled in their firmware and whether it can be disabled.
Join Our Newsletter
Subscribe to our newsletter to get our newest articles instantly!
TAGGED:Charging InfrastructureCybersecurityElectric Vehicles (EVs)Firmware SecurityRemote Code Execution (RCE)Telematics Control Units (TCU)Vulnerabilities
SOURCES:The Hacker News
Share This Article
Facebook Email Copy Link

Follow US

Find US on Social Medias
FacebookLike
XFollow
YoutubeSubscribe

You Might Also Like

Congress moves to make its Chinese car ban permanent
Policy & Compliance

Congress moves to make its Chinese car ban permanent

By
ctadmin
September 25, 2026
Physical Security

Columbus closes a theft lawsuit against Kia and Hyundai for $1M

By
ctadmin
September 28, 2026
Cybersecurity

$60 mirror can make self-driving cars brake for ghosts

By
ctadmin
August 10, 2026
Cybersecurity

DEF CON 34 talk will tear down a store-bought relay theft tool

By
ctadmin
August 9, 2026
Cybersecurity

Seoul consortium builds one chip to shield cars from quantum threats

By
ctadmin
August 19, 2026
Policy & Compliance

India’s AIS-156 update makes wireless BMS hacking tests compulsory

By
ctadmin
September 9, 2026

CarThreat

Intelligence for the EV and automotive security market
  • News
  • Features
  • Spotlight
  • Events
  • About Carthreat
  • Our Mission
  • Services
  • Contact Us
  • OBD-II
  • Automotive Ethernet
  • TCU
  • Infotainment Systems
  • SDVs
  • BMS
  • ECU Security
  • CAN Bus
  • Threat Intelligence
  • Cybersecurity
  • Digital Keys
  • Bluetooth Security
  • OTA Updates
  • Vulnerabilities
  • Relay Attacks
  • RCE
  • Data Privacy
  • EVs
  • Autonomous Driving
  • Pwn2Own Automotive
  • ISO/SAE 21434
  • UNECE R155
  • Regulations

© 2026 Carthreat.com. All right reserved.  Privacy Policy | Legal

Welcome Back!

Sign in to your account

Username or Email Address
Password

Lost your password?