CarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Notification
  • Autonomous Driving
  • Automotive Ethernet
  • BMS
  • ECU
  • EV
  • ISO/SAE 21434
  • Infotainment
  • OTA Updates
  • OBD-II
  • Pwn2Own
  • RCE
  • SDVs
  • TCU
  • UNECE R155
India's two-part cyber rulebook now has a certification trail
Cybersecurity

India’s two-part cyber rulebook now has a certification trail

Colmobil shuts some counters after intruders reach its network
Cybersecurity

Colmobil shuts some counters after intruders reach its network

A supplier flaw handed car buyers' payment records to criminals
Cybersecurity

A supplier flaw handed car buyers’ payment records to criminals

Physical Security

Rental cars stored video of Norwegian troops and gate codes

Font ResizerAa
CarThreatCarThreat
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
Search
  • Home
  • News
  • Features
  • Spotlight
  • Events
  • About
    • Our Mission
    • Services
    • Contact
Sign In Sign In
Follow US
© 2026 Carthreat.com. All right reserved.
Cybersecurity

US automakers scramble to strip Chinese parts from connected cars

Federal connected vehicle rules force automakers to replace Chinese hardware as an Ohio startup scrambles to fill the supply gap.

CarThreat Staff
Last updated: July 24, 2026 2:17 am
By
ctadmin
2 Min Read
SHARE

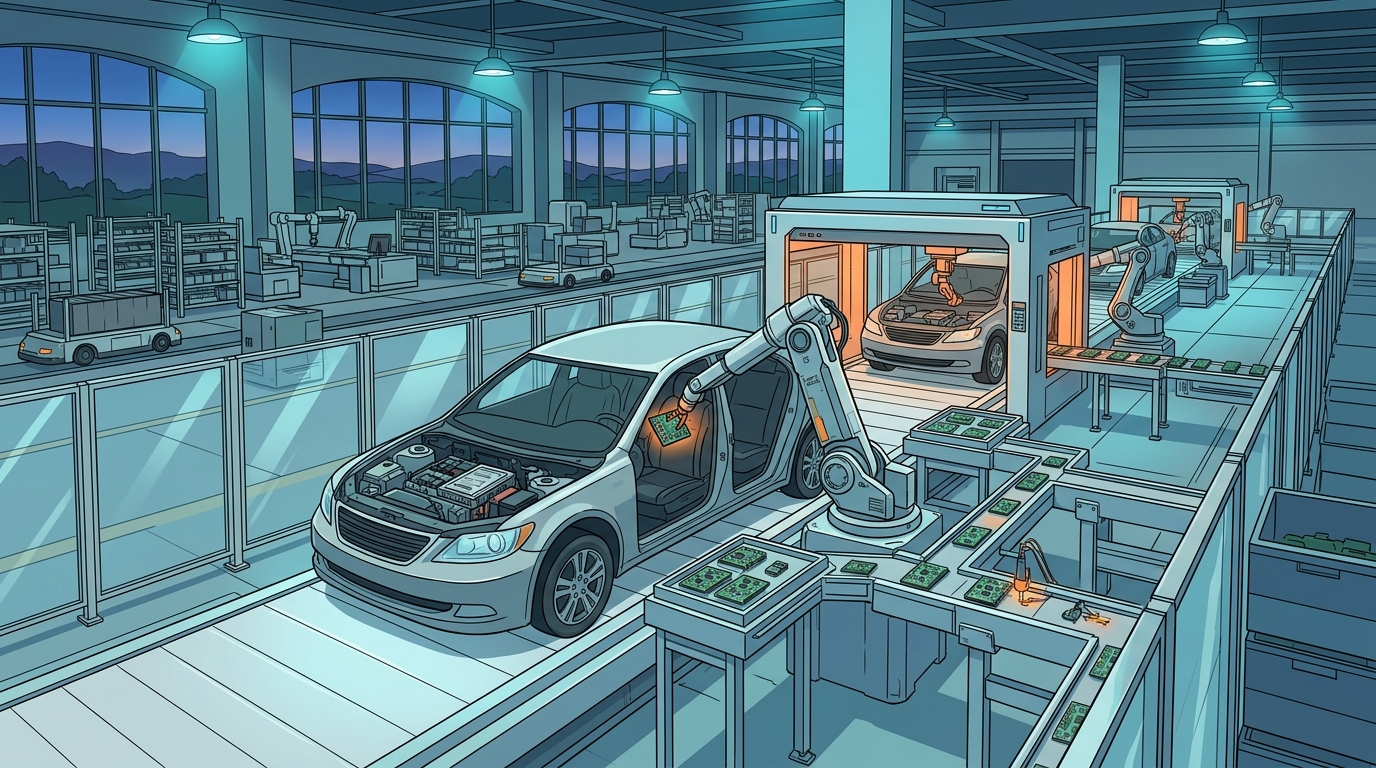
The US auto industry is racing to replace Chinese-made connected vehicle hardware ahead of federal deadlines, with a new Ohio factory at the center of the supply chain overhaul.

Eagle Wireless, formed in late 2025 specifically to address the looming regulations, is scaling production of wireless connectivity modules at its Solon, Ohio facility. The company started with 140 employees and aims to reach 1,000 within three years, with revenue expectations surging nearly 100% to $100M, according to President TJ Dembinski.

The push stems from a Bureau of Industry and Security rule adopted in January 2025 that bans Chinese connectivity software from model year 2027 vehicles and Chinese-designed or manufactured hardware from model year 2030. The rule, kept in place under the Trump administration, targets components such as satellite communications systems, external antennas, and microcontrollers that enable external vehicle connectivity.

Chinese vendors currently account for nearly half of global automotive cellular IoT module shipments, making the transition costly. Shifting sourcing away from China adds 5% to 15% to module costs, industry executives say. The rule “requires a deep examination of supply chains and aggressive compliance timelines,” said Hilary Cain of the Alliance for Automotive Innovation.

Automakers including Ford have already sought authorization to continue importing some China-produced models. The Polestar ban in June under the same rule heightened industry concern, as the Geely-owned EV maker was blocked from US sales. Rivian says it is better positioned than legacy automakers to shift suppliers quickly.

Eagle competes against established players like Rolling Wireless and LG in North America. Security firm Finite State CEO Matt Wyckhouse, an Eagle adviser, said the affected components span satellite systems, antennas, and microcontrollers critical to vehicle connectivity. The company expects to reach a 2-million-module annual run rate by the end of Q3 2026.
Join Our Newsletter
Subscribe to our newsletter to get our newest articles instantly!
TAGGED:Connected VehiclesCybersecurityRegulationsSupply ChainTelematics Control Units (TCU)V2X Communications
SOURCES:Reuters
Share This Article
Facebook Email Copy Link

Follow US

Find US on Social Medias
FacebookLike
XFollow
YoutubeSubscribe

You Might Also Like

Cybersecurity

A passwordless port let a researcher command a moving BYD ute

By
ctadmin
September 21, 2026
Cybersecurity

India Mandates AIS-189 Cybersecurity Norms for Connected Vehicles by 2029

By
ctadmin
June 30, 2026
CybersecurityPolicy & Compliance

NHTSA opens a rewrite of its vehicle cybersecurity playbook

By
ctadmin
October 10, 2026
Car NewsCybersecurity

Tesla keyless theft vulnerability exposes CAN injection risks across EV fleets

By
ctadmin
July 18, 2026
Physical Security

Columbus closes a theft lawsuit against Kia and Hyundai for $1M

By
ctadmin
September 28, 2026
Cybersecurity

VicOne research reveals ransomware threats targeting global logistics fleets

By
ctadmin
July 18, 2026

CarThreat

Intelligence for the EV and automotive security market
  • News
  • Features
  • Spotlight
  • Events
  • About Carthreat
  • Our Mission
  • Services
  • Contact Us
  • OBD-II
  • Automotive Ethernet
  • TCU
  • Infotainment Systems
  • SDVs
  • BMS
  • ECU Security
  • CAN Bus
  • OTA Updates
  • Vulnerabilities
  • Relay Attacks
  • RCE
  • Threat Intelligence
  • Cybersecurity
  • Digital Keys
  • Bluetooth Security
  • ISO/SAE 21434
  • UNECE R155
  • Regulations
  • Data Privacy
  • EVs
  • Autonomous Driving
  • Pwn2Own Automotive

© 2026 Carthreat.com. All right reserved.  Privacy Policy | Legal

Welcome Back!

Sign in to your account

Username or Email Address
Password

Lost your password?